 InfoSecBulletin Cybersecurity for mankind
CISA has updated a new alert to reflect the addition of CVE-2026-109618 and CVE-2026-109619 to its Known Exploited Vulnerabilities (KEV) Catalog on Oct. 26, 2026.
CISA urges organizations to quickly fix the recently found serious flaws in PHP, CVE-2026-109618 and CVE-2026-109619. These flaws, called “php2shell,” let remote code run in PHP without authentication.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

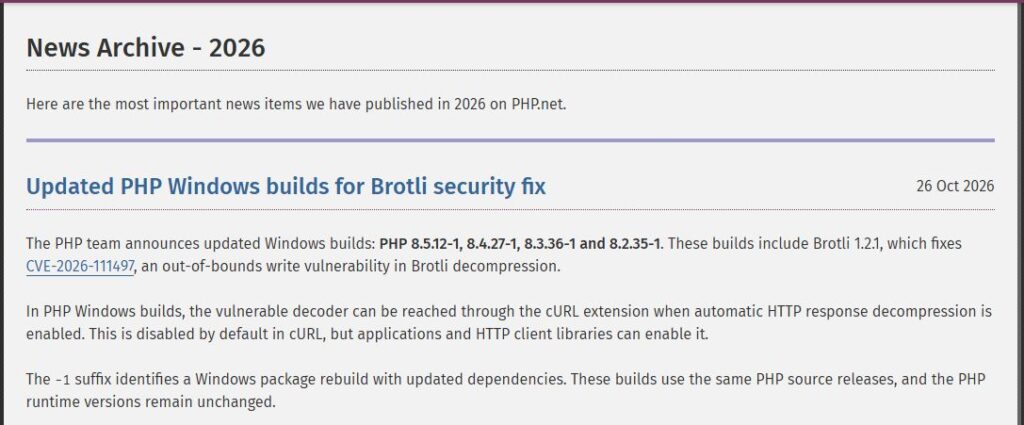
PHP Releases Windows Build Security Updates
PHP unveiled new Windows builds to fix a serious flaw dubbed HTTP2Shell. The new packages are PHP 8.5.12-1, 8.4.27-1, 8.3.36-1, and 8.2.35-1, and PHP announced them on October 26, 2026.
Each build now includes Brotli 1.2.1, which fixes CVE-2026-111497. Windows users running PHP should install these packages right away.
The flaw is in Google’s Brotli library. This is a tool that many programs use to unpack data. It has an out-of-bounds write issue, meaning the code writes past the memory area it should use. Node.js shared the bug in its security update on October 21, and researchers first named it Node2Shell.
Administrators should look for a different security update that PHP released on October 21. This update fixed two serious problems, CVE-2026-109618 and CVE-2026-109619, which can let bad actors run code without logging in. PHP 8.2 will no longer be supported after December 31, 2026, so teams using it should prepare to upgrade to a newer version.
Related news:
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation
Update now! PHP2Shell: Critical PHP vulnerabilities patched



