 InfoSecBulletin Cybersecurity for mankind
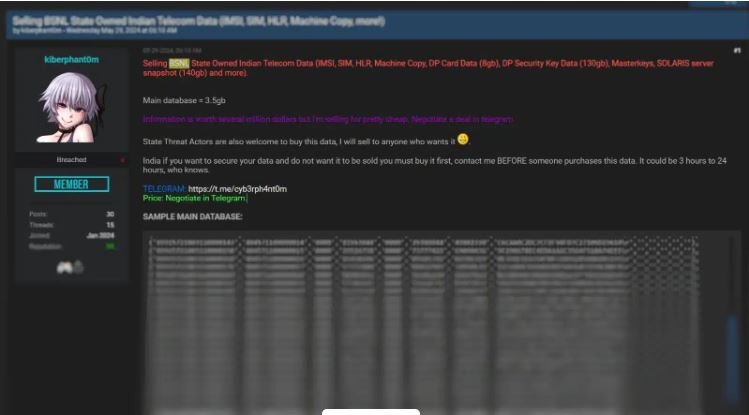
According to digital risk management firm Athenian Technology, BSNL, India’s state-owned telecom provider, suffered a significant data breach. A cybercriminal named “kiberphant0m” performed the attack, resulting in the exposure of a large amount of sensitive data. This puts millions of users at risk.
Zee news reported, Kanishk Gaur, CEO of Athenian Technology stated that the data breach at BSNL was carried out by a threat actor named ‘kiberphant0m’, as per report by ET. Gaur further explained, The breach involved over 278 GB of data from BSNL’s telecom operations. This includes server snapshots which could be used for activities like SIM cloning and extortion.
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

The report reveals that the cybercriminal responsible for the BSNL data breach is selling the stolen data for $5,000. This offer was available only from May 30 to May 31, 2024.
Cyber express reported, “The hacker also posted details of call log samples which leaked sensitive information like mobile numbers of users, the date and duration of calls, and the amount charged for the call in Indian Rupees. The call log samples were being leaked in two sets: one for the month of May 2024 and another from 2020. This indicates that the data breach was a recent attack raising questions over the security checks in place at BSNL.”
Risks of SIM Cloning:
– Duplicate SIM Cards: “creating an exact copy of the original”
– Interception: Cloned SIM cards can intercept communications intended for the original user.
– Bypassing Security: They can bypass two-step verification.
– Financial Fraud: Can be used for accessing bank accounts and committing fraud using someone else’s identity.
– Personal Security Compromise: Puts personal information at risk, potentially leading to financial harm.
Cybersecurity experts at Athenian Tech suggest that BSNL needs to act quickly to control the breach, secure network endpoints, and review access logs. They advise improving security measures, performing regular security audits, and using advanced threat detection technologies.
In December 2023, a hacker named ‘Perell’ leaked a dataset with 32,000 lines of data on a dark web forum. This dataset revealed private information about BSNL’s fiber and landline service users.
(Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided is for reference only, and users are responsible for relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)



