 InfoSecBulletin Cybersecurity for mankind
Booking.com, a major online travel agency, reported that customers have been targeted by hackers. While the agency’s systems are secure, online criminals have scammed many customers by stealing login credentials from the agency’s partner hotels. These criminals then pose as hotel staff to deceive customers.
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

What have the online attacks on Booking.com been like?
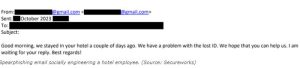
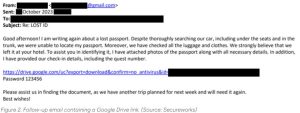
Fraudsters deceive hotels by pretending to be recent guests who left behind valuable items. They do this by calling the front desk and then sending an email with a link to a file on Google Drive.
The file was expected to be a picture of the item. But it turned out to be a malicious file called Vidar Infostealer. When the customer service representative opened it, it automatically stole login information from the hotel system and sent it to the fraudsters.
Hackers steal login information from Booking.com and use it to deceive hotel guests. They pretend to be hotels and ask guests to pay fake fees. Instead of using the official website, they send guests to a fake website or ask for credit card details over the phone. This scam is successful because the messages appear to come from legitimate hotel accounts on Booking.com.
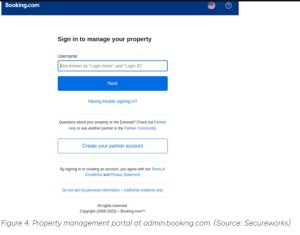
Booking.com login credentials were found for sale on the Dark Web at a price of around $2,000. This suggests that these login details are highly effective. Booking.com has acknowledged the cyber-attacks on its partner hotels and is taking measures to stop them.



