 InfoSecBulletin Cybersecurity for mankind
National Attack Surface (NAS) report for the first half of 2024 reveals that 56.6% of cyberattacks in Bangladesh targeted educational institutions, indicating a serious lack of maintenance and updates for school websites, making them highly vulnerable.
During this period, 32.4% of attacks targeted government websites, revealing significant security flaws. The remaining 11% affected private and business websites, highlighting the broad reach of cyber threats in the country.
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Attack Patterns:
The NAS report, prepared by BCSI, also outlined the primary patterns of attacks across Bangladeshi websites:
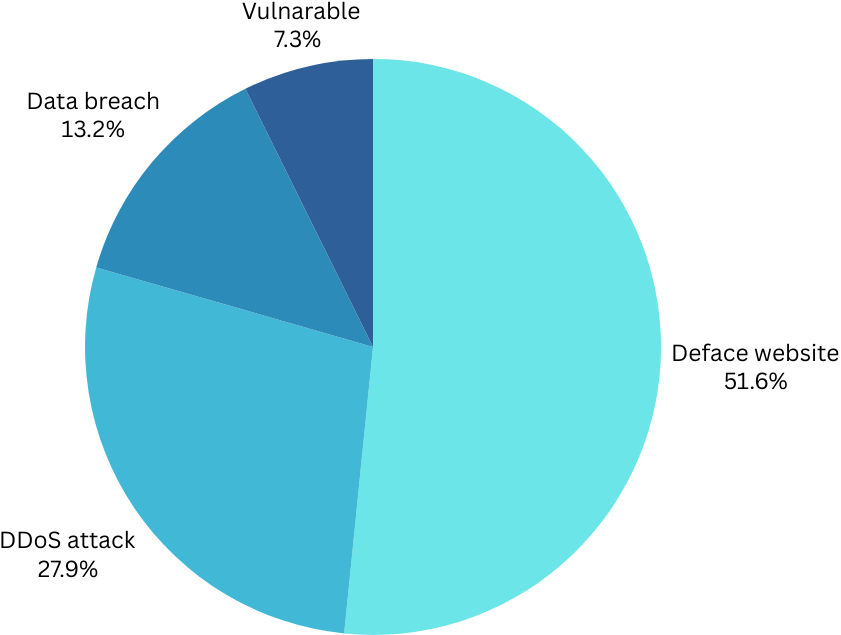
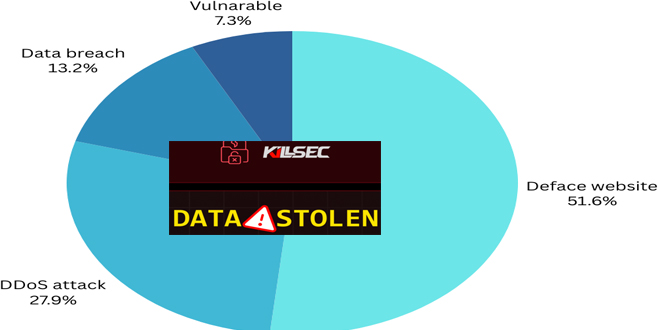
* Attackers damaged the public image and functionality of 51.6% of websites by defacing them.
* 27.85% experienced DDoS attacks, disrupting services and access to important resources.
* 13.24% experienced significant data breaches, risking the exposure of sensitive information to unauthorized individuals.
* 7.31% of websites remained vulnerable because attackers still had access to their admin panels.
The National Attack Surface (NAS) report for the first half of 2024 reveals a concerning trend: 56.6% of cyberattacks in Bangladesh targeted educational institutions. This suggests a significant failure to maintain and update school websites, making them vulnerable to these attacks.
Meanwhile, The ransomware group “KillSec” has attacked “বঙ্গবন্ধু সরকারি কলেজ, তারাকান্দা, ময়মনসিংহ,” stealing sensitive data. They announced the breach on their Dark Web site on October 4th, revealing control over student records, academic data, and the college’s application systems. A countdown for the full data release is set for 7 days, 2 hours, and 59 minutes, but KillSec has not revealed their ransom demands.
According to KillSec’s description, the data they have taken includes:
File system structure, directory names, and file names
Application framework structure and database information
Error logs and configuration files
Student records, including academic data and course information
Student names, exam dates, subject names, grade levels, student IDs, and marks/scores
Institutional details like academic years, class sections, and curriculum details
This isn’t KillSec’s first attack on a Bangladeshi institution. Earlier this year, they breached a financial organization, raising concerns about the nation’s cybersecurity. Their recent attack on Bangabandhu Government College further establishes them as one of the most dangerous cyber threats to Bangladesh’s digital infrastructure.
Cyberattacks are becoming more common and advanced, so all sectors must focus on cybersecurity by updating systems regularly and training staff to handle threats effectively.



