 InfoSecBulletin Cybersecurity for mankind
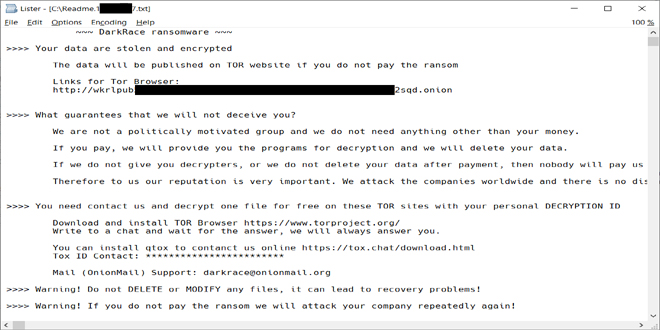
Avast researchers found a security flaw in the DoNex ransomware and its previous versions, which allowed them to create a tool to decrypt the files. They shared this discovery at the Recon 2024 conference. Avast released a free decryptor in March 2024 to help victims recover their files.
“All brands of the DoNex ransomware are supported by the decryptor.” reads the announcement. “DoNex uses targeted attacks on its victims and it was most active in the US, Italy, and Belgium based on our telemetry.”
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

The company has been working with the police to secretly give victims a tool to unlock their data and prevent the ransomware author from learning how it was created.
DoNex is a new version of Muse and DarkRace ransomware. It was first seen in April 2022.
When running, CryptGenRandom() creates an encryption key. The harmful code then uses the key to start the ChaCha20 symmetric key and encrypt files. After encrypting a file, the symmetric file key is encrypted with RSA-4096 and added to the end of the file. Files are chosen by their extension, and the extensions are listed in the ransomware XML config.
The ransomware encrypts small files completely. For files larger than 1MB, it uses intermittent encryption by splitting the files into separate blocks that are encrypted individually.
DoNex ransomware and its previous versions have XOR-encrypted configurations that include settings for whitelisted extensions, files, services to kill, and other encryption-related data.
The researchers suggest using the 64-bit version for better performance, as it requires a lot of memory for the password-cracking process. Experts advise making a backup of encrypted files before using the decryption tool, in case something goes wrong. The researchers also provided Indicators of Compromise (IOCs) for this threat.



