Sunday , November 15 2026
Bahrain

Anonymous Collective claim
Anonymous Collective claim attack on Bahrain’s E Visa Service

Hacktivist group, Anonymous Collective claim to cyber attack the E Visa service of the Bahrain government. The cyberattack on Bahrain government has raised concerns about the cyber security arena of sensitive data protection.
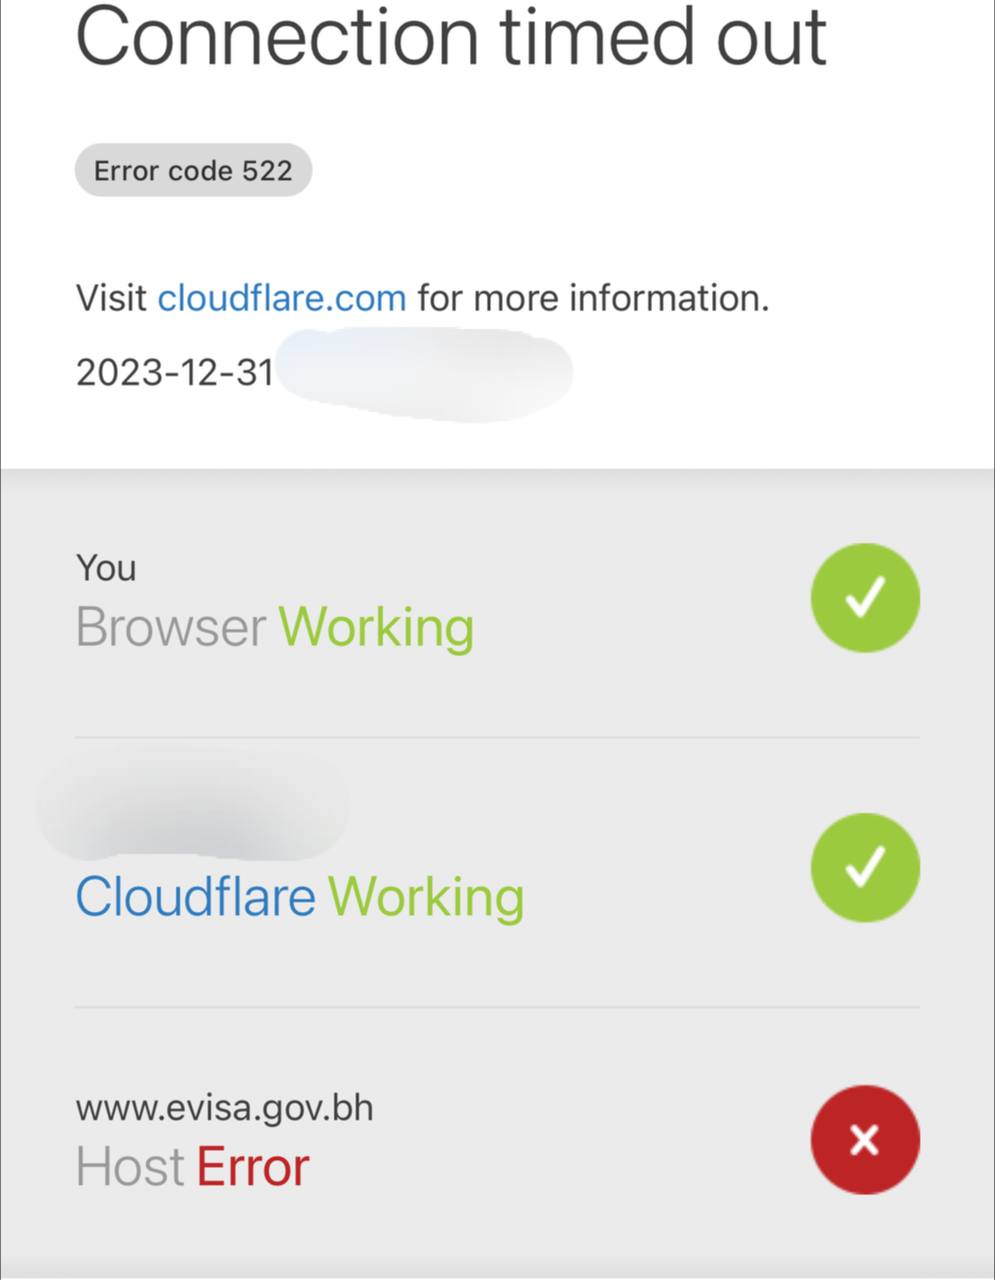
Source: Anonymous collective’s social handle

The hacktivist group shared a screen shot of attack of the E Visa services on their social handle as a proof of their attack to be credible. (https://check-host.net/check-report/144796f7k307) The group also placed a link of check host. But crucial details regarding the extent of the breach, compromised information, and the motive behind the attack remain undisclosed.

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

The Cyber Express reported that they reached out to the official channels for verification of the cyberattack claim. However, as of now, there has been no response from the government’s end.

While publishing the report, the E visa services appears to be fully functional. It raises the possibility that the hacktivist group may be using the cyberattack as a tactic to gain attention or there might be a different motive behind the assault.

The lack of an official statement has left both citizens and cybersecurity experts in suspense, eagerly awaiting clarification on the situation.

(Media Disclaimer: This report is based on internal and external research obtained through various means. The information provided is for reference purposes only, and users bear full responsibility for their reliance on it. Infosecbulletin assumes no liability for the accuracy or consequences of using this information.)


Check Also

ARTEX

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Hackers used ARTEX, a free tool for testing security with AI, to attack over 200 …