 InfoSecBulletin Cybersecurity for mankind

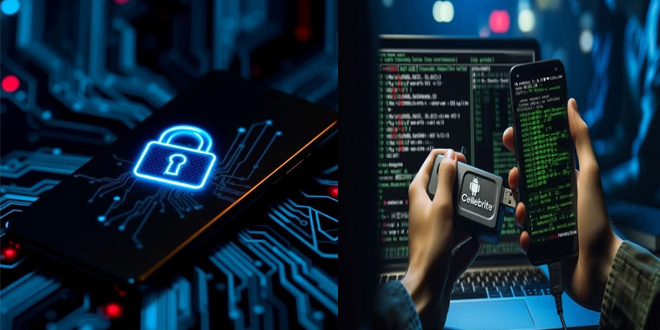
Amnesty International’s Security Lab discovered a cyber-espionage campaign in Serbia, where officials used a zero-day exploit from Cellebrite to unlock a student activist’s Android phone.
On December 25, 2024, an attack used flaws in Linux kernel USB drivers to bypass the lock screen on a Samsung Galaxy A32.
Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation
AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Anthropic prepares “Claude Money” to analyze bank account and financial data

GhostCode Phishing Kit Evades Microsoft 365 MFA to Hijack Accounts in 78 Seconds

CISA Warns of Cisco Secure Email Gateway 0-Day Flaw Actively Exploited in Attacks

VPN flaw exposed 246,000 personnel records in japan

Hackers deploy Casbaneiro Trojan that activates on bank websites

German police read Signal, Telegram, WhatsApp messages without breaking encryption

Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

Forensic analysis showed that vulnerabilities in an outdated USB driver were exploited to gain root access, allowing data theft and attempts to install surveillance software. This incident highlights the misuse of digital forensics tools on civil society and reveals significant weaknesses in Android’s defenses against physical attacks.
Exploit Chain Targets, USB Driver:
The attack used a complex series of fake USB devices to exploit memory corruption issues in the Linux kernel. Forensic logs reveal that authorities connected several harmful devices using Cellebrite’s Turbo Link adapter, including:
A Chicony CNF7129 UVC Webcam (VID:0x04f2) exploiting CVE-2024-53104, an out-of-bounds write in the USB Video Class driver’s frame-rate restriction quirk.
A Creative Extigy SoundBlaster (VID:0x041e) leveraging CVE-2024-53197, which allowed descriptor corruption during ALSA sound card initialization.
An Anton Touch Pad (VID:0x1130) exploiting CVE-2024-50302 to leak uninitialized kernel memory via HID reports.
These vulnerabilities, fixed in Linux kernel versions 6.6 and in the February 2025 Android Security Bulletin, originated from code written between 2010 and 2013.
Attackers exploited vulnerabilities to gain higher privileges, as kernel logs indicate root shell access occurred just 10 seconds after connecting the last USB HID device.
A 23-year-old student named “Vedran” was detained by plainclothes officers during protests against Serbia’s ruling party in December 2024. Device logs support his claims.
Post-exploitation activity included file system enumeration using find/grep and deployment of Cellebrite’s “falcon” binary for advanced data extraction. While the target APK installation failed due to a biometric lockout, the breach exposed call logs, messages, and protest coordination details.
Google’s Threat Analysis Group worked with Amnesty to address three CVEs, resulting in patches. However, more than 40% of Android devices were still unpatched as of March 2025 because of uneven vendor update cycles. On February 25, 2025, Cellebrite suspended its Serbian clients, stating:
“We found it appropriate to stop use of our products by relevant customers… Our compliance program ensures ethical, lawful use.”
Critics say the measure is not transparent because Cellebrite hasn’t revealed how long its suspension will last or the human rights protections for reinstatement. The company’s Premium UFED toolkit is still in use in 78 countries, despite reports of abuse in 12 states since 2022.



