Sunday , November 1 2026
Passwords

Nearly 12,000 API Keys and Passwords Found in Public Datasets

Security researchers found that datasets used by companies to develop large language models included API keys, passwords, and other sensitive credentials.

Large language models are dominating the online landscape, with companies promoting AI solutions that claim to solve all problems.

Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks
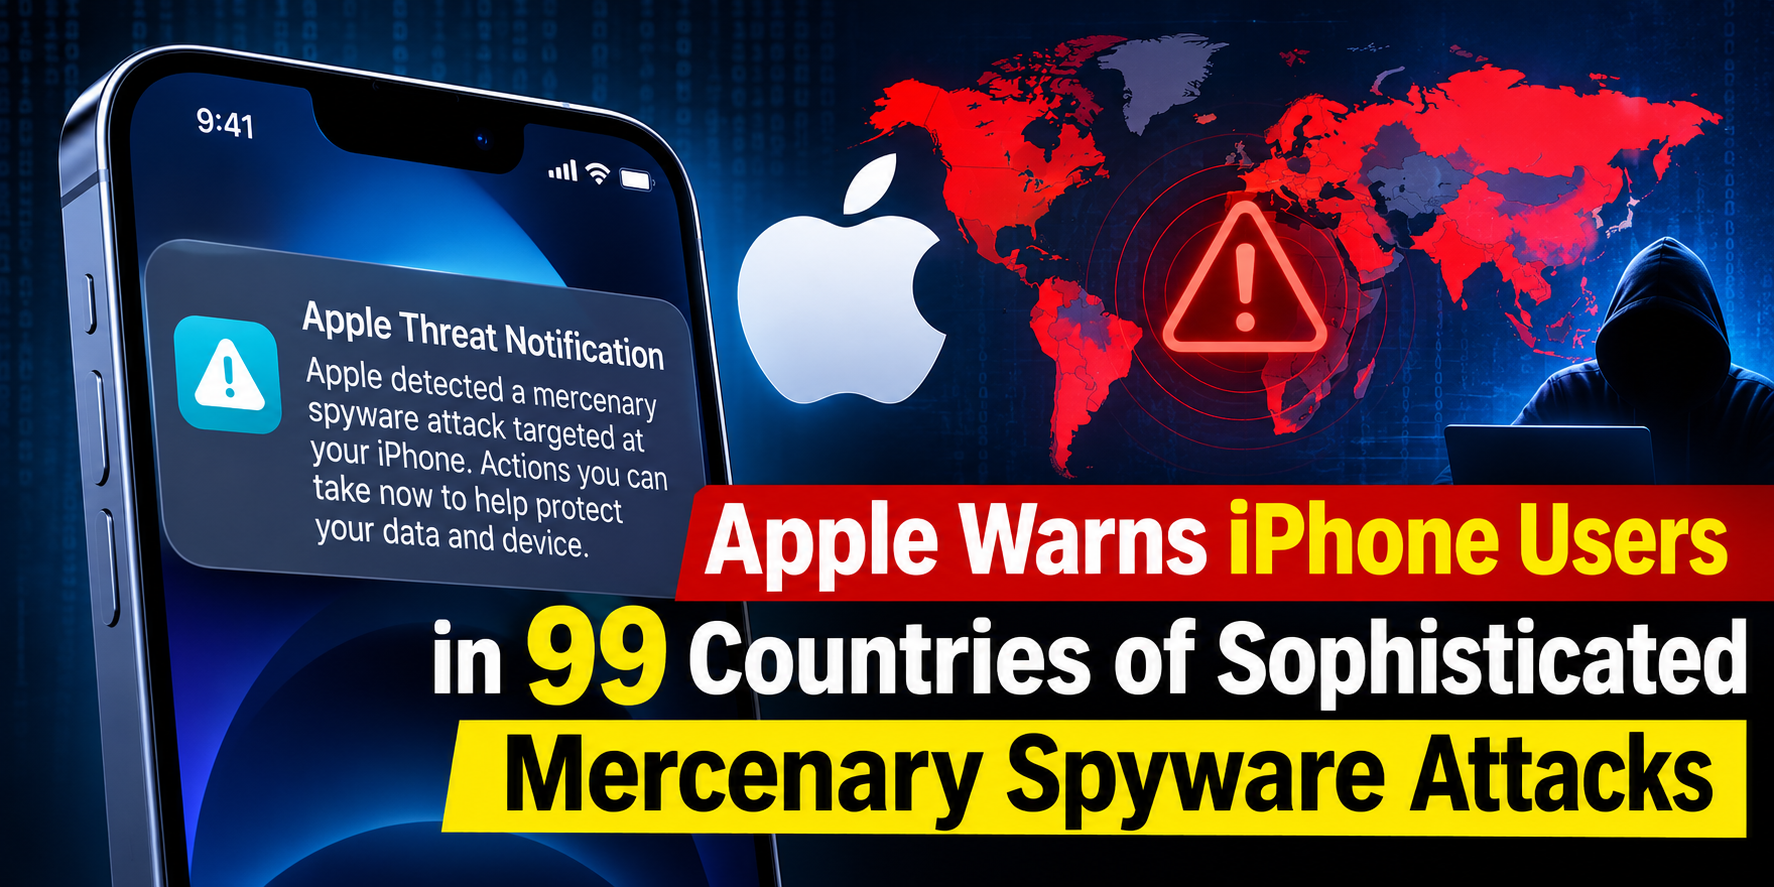
Apple has sent new threat warnings to some iPhone users in 99 countries. They said these users may be targeted...
Read More
Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks

Daily Cyber security update for 31.10. 2026
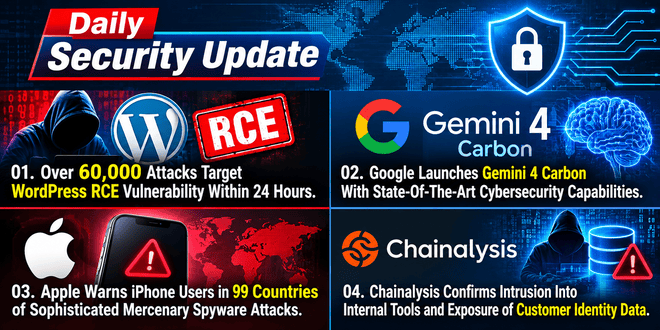
Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 31.10. 2026

NetamLoader malware to attack Win10: Customized for Gov.t in Asia

A new malware framework named NetamLoader is attacking a special version of Windows 10 used only by government agencies in...
Read More
NetamLoader malware to attack Win10: Customized for Gov.t in Asia

‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

A security expert shared information about a zero-click Android bug known as “SMS of Death.” Just one bad text message...
Read More
‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

NIST Unveiled Guidance for Post-Quantum Cryptography Transition

The National Institute of Standards and Technology (NIST) has shared advice on switching to post-quantum cryptography. This helps federal agencies...
Read More
NIST Unveiled Guidance for Post-Quantum Cryptography Transition

Daily Cyber security update for 29.10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 29.10. 2026

Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

Rapid7 researchers found 17 security flaws in Zimbra Collaboration Suite (ZCS) that mess up authentication, mailbox isolation, and host privileges....
Read More
Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) provides two free tools to help organizations spot security flaws in Microsoft...
Read More
CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

Apple launched iOS 27.2 and iPadOS 27.2 on October 26, 2026, fixing 163 security flaws. The update is for iPhone...
Read More
Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

CISA has updated a new alert to reflect the addition of CVE-2026-109618 and CVE-2026-109619 to its Known Exploited Vulnerabilities (KEV)...
Read More
CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

For an AI to be effective, it needs extensive training data, much of which is gathered from the Internet by specialized companies and organizations.

Common Crawl provides datasets for companies to train their AI, gathering information from the internet, which may include sensitive data.

Researchers from Truffle Security discovered that credentials, API keys, and passwords are being exposed. The main issue is that some web developers hardcode sensitive information into websites, which then ends up in LLM training data.

Researchers discovered 11,908 live secrets, such as API keys and passwords, across 2.76 million websites.

“Leaked keys in Common Crawl’s dataset should not reflect poorly on their organization; it’s not their fault developers hardcode keys in front-end HTML and JavaScript on web pages they don’t control. And Common Crawl should not be tasked with redacting secrets; their goal is to provide a free, public dataset based on the public Internet for organizations like Truffle Security to conduct this type of research,” explained the researchers.

Companies that create LLMs have warned against hardcoding sensitive information on websites. They advise avoiding this practice, as users may unintentionally share the code in their work, worsening the issue.
Check Also

Security

Daily Cyber security update for 25. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These …