InfoSecBulletin Cybersecurity for mankind
In a world where cybercrime is becoming more difficult to prevent, many security leaders are putting pressure on IT professionals to bury the truth.
New research released by cybersecurity vendor Bitdefender today surveyed over 400 IT and security professionals who work in companies with 1,000 or more employees. Bitdefender found that 42% of IT and security professionals surveyed had been told to keep breaches confidential — i.e., to cover them up — when they should have been reported.
PHP updates fix 18 flaws, with critical RCE bugs included

F5 Issues Out-of-Band Security Advisory Covering 22 Flaws Across NGINX and BIG-IP Products

Over 1 million credit cards stolen in attack across 20 countries

Knight Squad Academy now serves as Bangladesh’s first CVE Numbering Authority

Daily Cyber security update for 18.11. 2026

Japan’s “Fugaku” supercomputer went offline after cyberattack

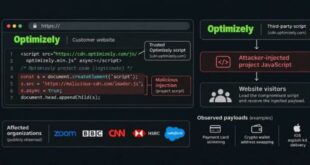
Hijacked Optimizely Scripts infect CNN, HSBC, BBC, Zoom, Salesforce sites with malware

Researcher Uncover 150 M Kik Profile Images Publicly Accessible Database

Months-old flaw led to a global Microsoft outage: said Microsoft

OWASP Top 10 Neocloud & AI Data Center Security Risks

Perhaps even more shockingly, 29.9% of respondents admitted to actually keeping a breach confidential instead of reporting it.
This research highlights that an alarming number of organizations are willing to ignore their obligations to report data breaches to regulators and customers, in an attempt to avoid legal and financial penalties.
The research comes less than a year after the FTC convicted former Uber CSO Joseph Sullivan for attempting to cover up a hack of Uber in 2016. The case highlighted that lying about data breaches is a serious criminal offense in many jurisdictions.
So why are so many tech leaders pressuring their staff to bury data breaches? The answer is that the cyberthreat landscape is becoming more and more demanding, with 52% of organizations experiencing a data breach within the past 12 months.
The five threats that respondents reported they are most concerned about are software vulnerabilities and zero-days (53.9%), phishing and social engineering (52.2%), supply chain attacks (49%), ransomware (48.5%) and insider threats (36.5%).
“Worldwide, organizations [are] under tremendous pressure to contend with evolving threats such as ransomware, zero-day vulnerabilities and espionage, while struggling with [the] complexities of extending security coverage across environments and an ongoing skills shortage,” said Andrei Florescu, deputy general manager and senior vice president of products at Bitdefender business solutions group.
While it’s difficult to guarantee that an organization will address cyber-incidents responsibly, proactive security leaders can look to decrease the chance of deceit by decreasing the burden on human security teams.
This includes investing in threat prevention, detection and response solutions that enable users to address and resolve security incidents faster, so that there is less impact on the organization and less exposure to legal and financial risk.
”The results of this survey demonstrate, more than ever, the importance of layered security that delivers advanced threat prevention, detection and response across the entire business while improving efficiencies that allow security teams to do more with less,” Florescu said.