InfoSecBulletin Cybersecurity for mankind
Key Ransomware Statistics:
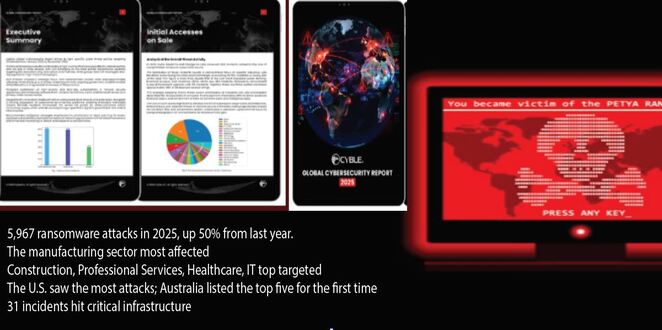
5,967 ransomware attacks in 2025, up 50% from last year.
The manufacturing sector most affected
Construction, Professional Services, Healthcare, IT top targeted
The U.S. saw the most attacks; Australia listed the top five for the first time
31 incidents hit critical infrastructure
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

2025 will be noted for an explosion in cyber threats, with nearly 6,000 ransomware cases, 6,000 data breaches, and over 3,000 compromised corporate access sales. Companies worldwide confronted an extremely dangerous digital environment. Manufacturing processes stopped, government agencies battled leaks, and critical infrastructure was directly attacked. The Cyble Global Cybersecurity Report 2025 reveals a 50% annual increase in ransomware attacks.
The Global Cybersecurity Report 2025 revealed that data breaches reached the second-highest level ever and the market for stolen access thrived.
The Cyble Global Cybersecurity Report 2025 recorded 5,967 ransomware attacks, a 50% increase from last year. It also noted 6,046 data breaches and leaks, the second-highest level ever.
The underground market for compromised initial access flourished, with 3,013 sales boosting the global cybercrime economy.
Daksh Nakra, Senior Manager of Research and Intelligence at Cyble treated 2025 as a “Major power shift in the threat landscape,” noting that new ransomware groups quickly filled the void left by law enforcement crackdowns. The combination of supply chain attacks and rapid weaponization of zero-day vulnerabilities created what he called “a perfect storm” for enterprises worldwide.
In 2025, two groups were notable. Akira ransomware became the second-most active group after Qilin, launching persistent attacks in Construction, Manufacturing, and Professional Services. Their opportunistic approach let them target almost every major industry.
CL0P ransomware proved its expertise in zero-day attacks. In February 2025, it launched a widespread campaign targeting enterprise file transfer software, affecting hundreds of victims at once, particularly in Consumer Goods, Transportation & Logistics, and IT sectors.
Government and law enforcement agencies faced the most breaches with 998 incidents (16.5% of total). The BFSI sector had 634 incidents. Combined, they made up over a quarter of all breaches, showing that attackers target sensitive citizen data and financial information.
Sales of stolen corporate access are driving cybercrime. Cyble found 3,013 cases of access sales, with the Retail sector most affected at 594 incidents (about 20%). BFSI had 284 incidents, and Government agencies reported 175.
The Cyble Global Cybersecurity Report 2025 noted that critical vulnerabilities in common enterprise technologies were key entry points for attacks. The most exploited included:
CVE-2025-61882 (Oracle E-Business Suite RCE) – leveraged by CL0P
CVE-2025-10035 (GoAnywhere MFT RCE) – exploited by Medusa
Multiple vulnerabilities in Fortinet, Ivanti, and Cisco products with CVSS scores above 9.0
In 2025, 94 zero-day vulnerabilities were found, with 25 rated above 9.0. Over 86% of CISA’s Known Exploited Vulnerabilities had CVSS ratings of 7.0 or higher, affecting Microsoft, Fortinet, Apple, Cisco, and Oracle the most.
Geopolitical Hacktivism Surges:
Cyble’s global cybersecurity report for 2025 reveals that hacktivist activity soared, resulting in over 40,000 data leaks affecting 41,400 different domains, primarily due to geopolitical conflicts.
The Israel-Iran conflict triggered operations by 74 hacktivist groups
India-Pakistan tensions generated 1.5 million intrusion attempts
North Korea’s IT worker fraud schemes infiltrated global companies
DDoS attacks, website defacements, and breaches targeted governments and critical infrastructure
Industry-Specific Insights
Manufacturing: Most attacked sector due to reliance on OT/ICS environments and low tolerance for downtime
Construction: Heavily targeted by Akira; time-sensitive projects created maximum pressure points
Professional Services: Law firms and consultancies compromised for sensitive client data and supply chain leverage
Healthcare: Continued to face attacks from groups like BianLian, Abyss, and INC Ransom due to critical data availability needs
IT & ITES: Service providers exploited to enable cascading supply chain attacks against downstream customers
Ransomware increased by 50%, thousands of breaches occurred, and the black market for hacked access is thriving. The Cyble global cybersecurity report 2025 emphasizes the need for businesses to enhance their security as critical infrastructure, government agencies, and key industries face rising threats.