
Wednesday , November 11 2026
admin

50K Cisco firewalls vulnerable to actively exploited flaws

50k Cisco ASA and FTD devices on the internet are at risk due to two vulnerabilities being exploited by hackers. Flaws CVE-2025-20333 and CVE-2025-20362 allow remote code execution and access to restricted VPN URLs without authentication.

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 million) in a cyber heist...
Read More
Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

On September 25, Cisco warned that the issues were actively exploited in attacks that started before patches were available to customers. There are no solutions for either flaw, but temporary measures could involve limiting VPN web interface access and enhancing logging and monitoring for unusual VPN logins and requests.

The Shadowserver Foundation reported that over 48,800 exposed ASA and FTD instances are still vulnerable to CVE-2025-20333 and CVE-2025-20362.
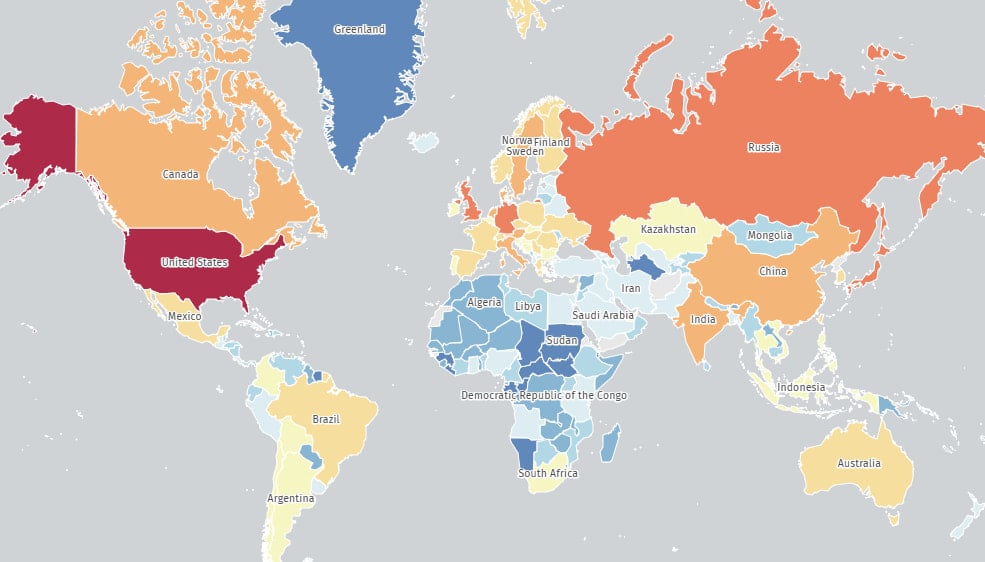
Global exposure of unpatched Cisco ASA/FTD devices Source: The Shadowserver Foundation

Most IPs are from the United States, followed by the United Kingdom, Japan, Germany, Russia, Canada, and Denmark.

As of September 29, these figures show a failure to address ongoing exploitation and earlier warnings.

Greynoise warned on September 4 about suspicious scans targeting Cisco ASA devices that began in late August. These scans often indicate potential undocumented flaws in 80% of cases.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued an urgent directive, allowing 24 hours for all Federal Civilian Executive Branch (FCEB) agencies to find and upgrade compromised Cisco ASA and FTD instances on their networks.

CISA also advised that ASA devices reaching their end of support (EoS) should be disconnected from federal organization networks by today (the end of the month).


 

Check Also

128

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin …

