 InfoSecBulletin Cybersecurity for mankind
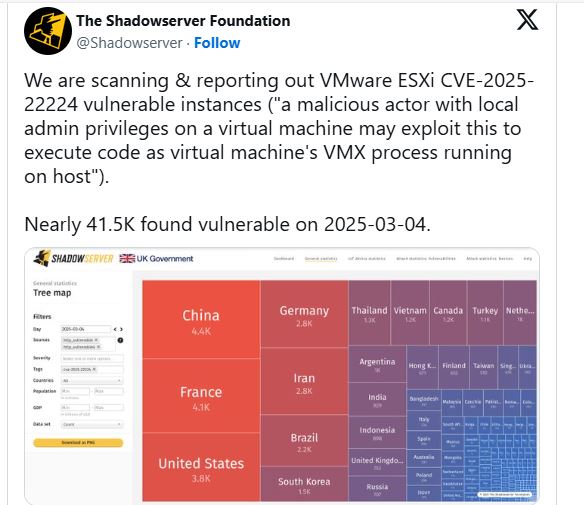
As of March 4, 2025, Shadowserver found that over 41,500 internet-exposed VMware ESXi hypervisors are vulnerable to the actively exploited CVE-2025-22224.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

41,500 unpatched ESXi instances represent a major part of global virtualization, especially in healthcare, finance, and telecommunications.
Broadcom released an emergency update to fix a vulnerability that allows attackers with local admin access to a virtual machine (VM) to run malicious code on the hypervisor, posing serious risks to cloud infrastructure and enterprise networks.
Hypervisor Escape via TOCTOU Flaw:
CVE-2025-22224 (CVSS 9.3) is a TOCTOU vulnerability found in VMware ESXi and Workstation. It lets attackers cause an out-of-bounds write in the VMX process, which manages individual VMs.
Exploitation occurs when an attacker gains administrative access to a virtual machine’s guest operating system, allowing them to escalate privileges to the host system. This gives them complete control over all virtual machines on the hypervisor, data stores, and connected networks.
The Microsoft Threat Intelligence Center found vulnerabilities and informed Broadcom, highlighting their use in ransomware and APT campaigns. The U.S. CISA added CVE-2025-22224 to its Known Exploited Vulnerabilities list on March 4, requiring federal agencies to fix it by March 25, 2025.
Mitigations:
Broadcom released patches for all affected products, including:
VMware ESXi 8.0: Update to ESXi80U3d-24585383 or ESXi80U2d-24585300
VMware ESXi 7.0: Update to ESXi70U3s-24585291
VMware Cloud Foundation 5.x/4.5.x: Apply async patches detailed in KB389385.
Organizations should quickly isolate ESXi management interfaces from the internet, review VM administrative access, and monitor unusual VMX activity. Rapid7 and Tenable have added detection checks in their platforms to find exposed systems.



