
Friday , November 13 2026
840

17K+ SharePoint Servers Exposed to Internet : 840 Servers Vuln to 0-Day Attacks

Over 17k Microsoft SharePoint servers are exposed to internet attacks, with 840 vulnerable to the critical zero-day vulnerability CVE-2025-53770, according to Shadowserver Foundation.
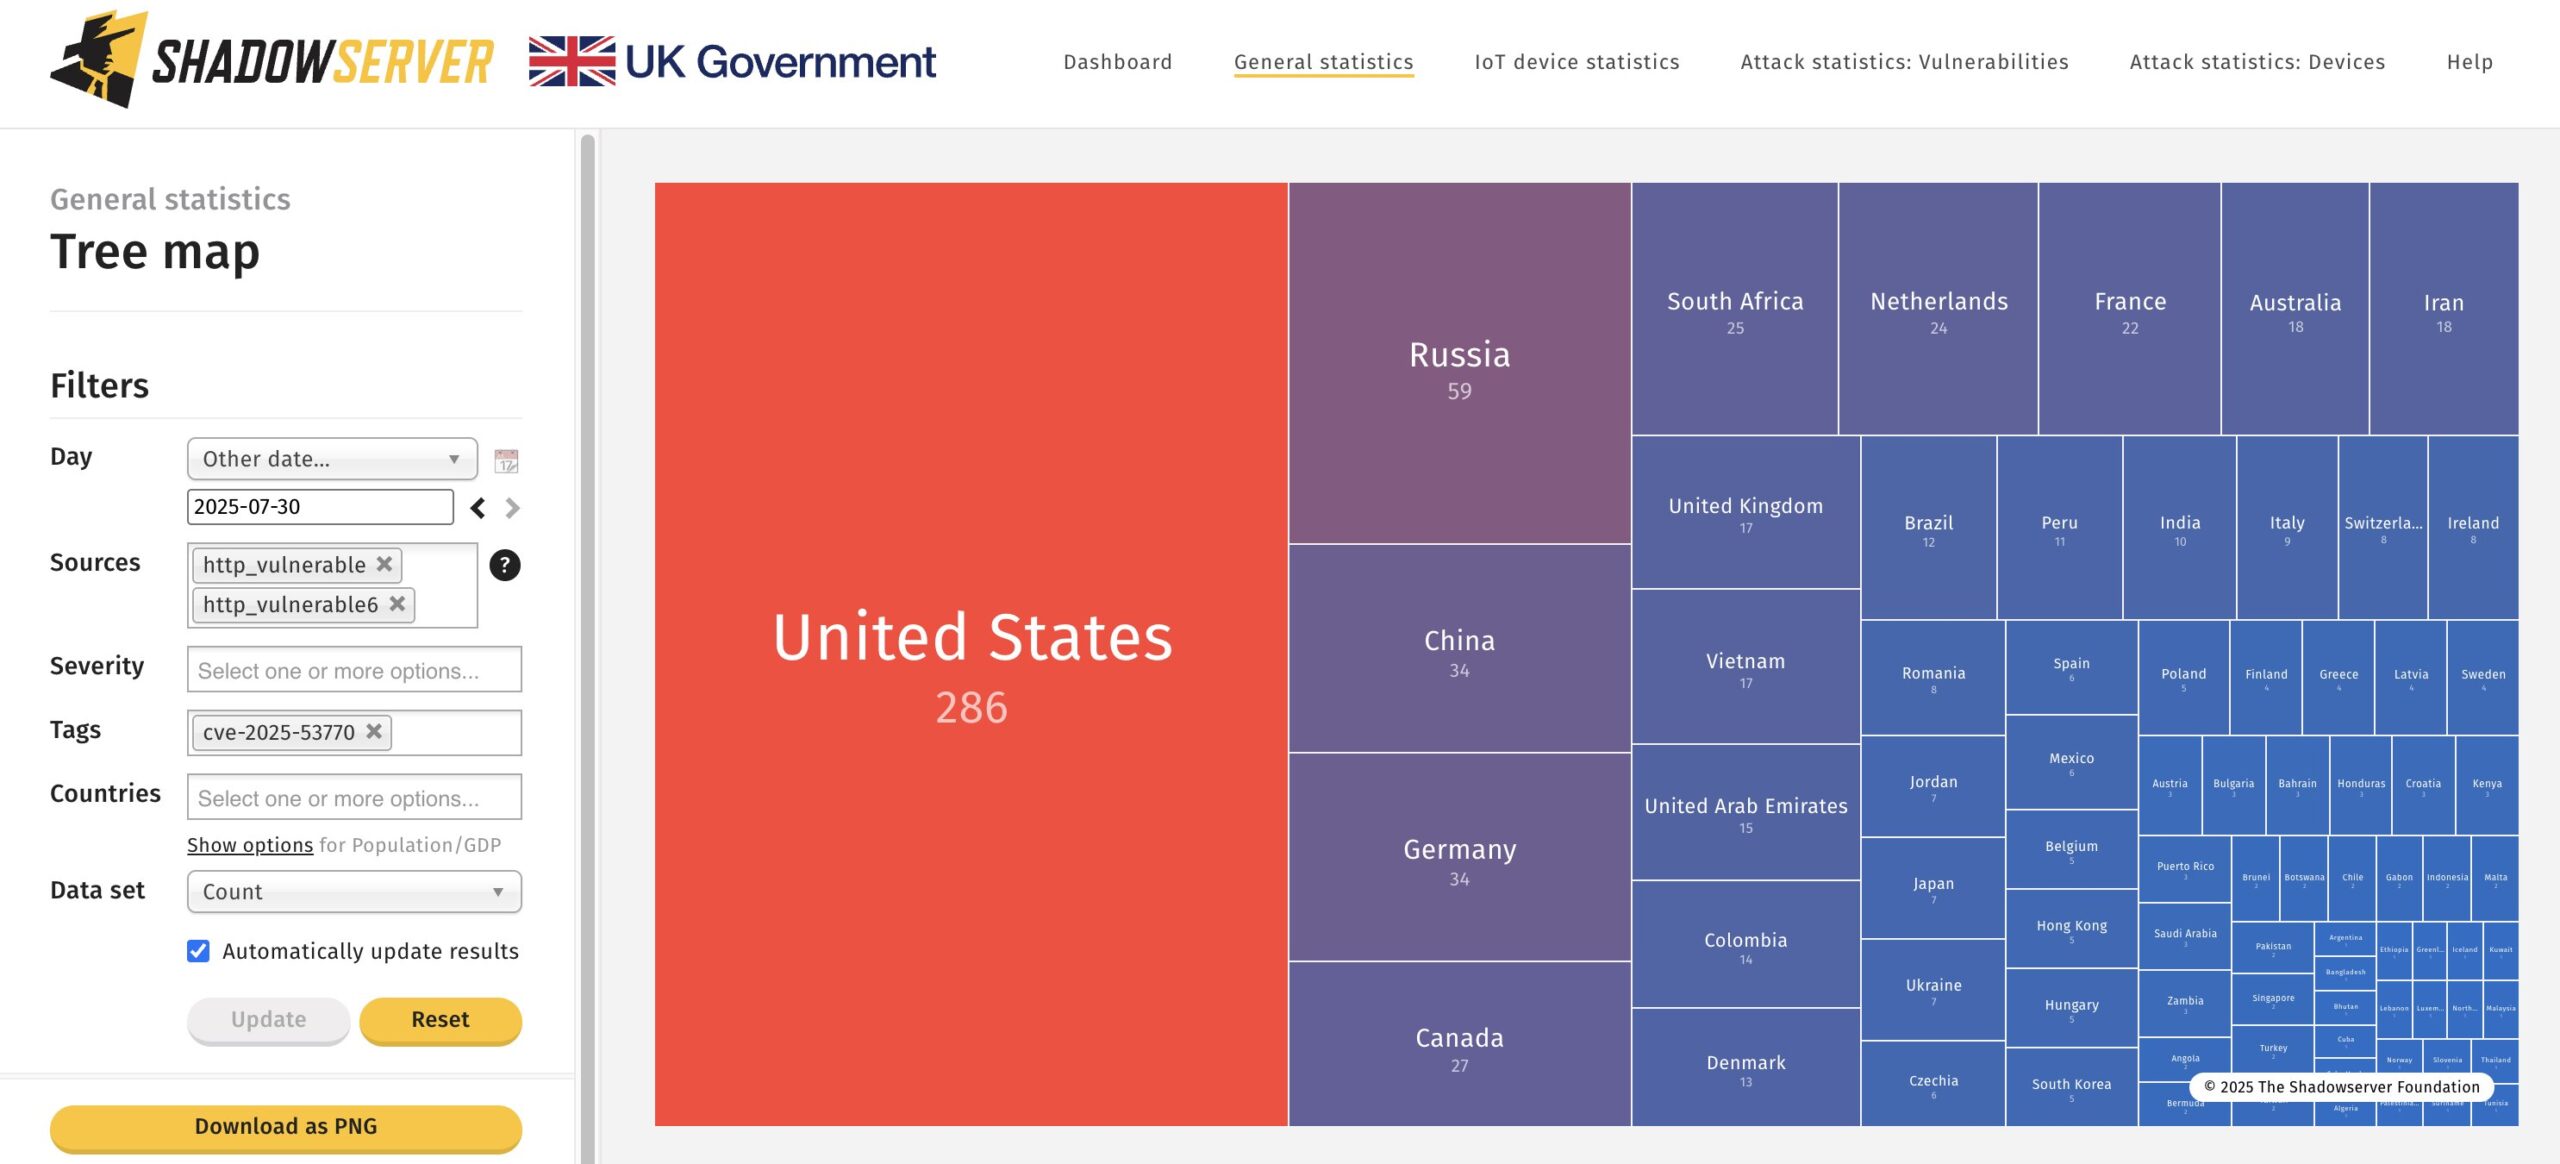
                                                                            Source: Shadowserver foundation

The “ToolShell” vulnerability has a critical CVSS score of 9.8 and lets unauthorized users run arbitrary code on on-premises SharePoint servers.

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Microsoft has attributed the attacks to three Chinese threat actors: Linen Typhoon (APT27), Violet Typhoon (APT31), and Storm-2603. The exploitation campaign has been active since July 7, 2025, with researchers observing a rapid escalation following the initial discovery.

Eye Security, which initially reported the attacks on July 18, has identified over 400 victim organizations across various sectors like government, healthcare, finance, and education.
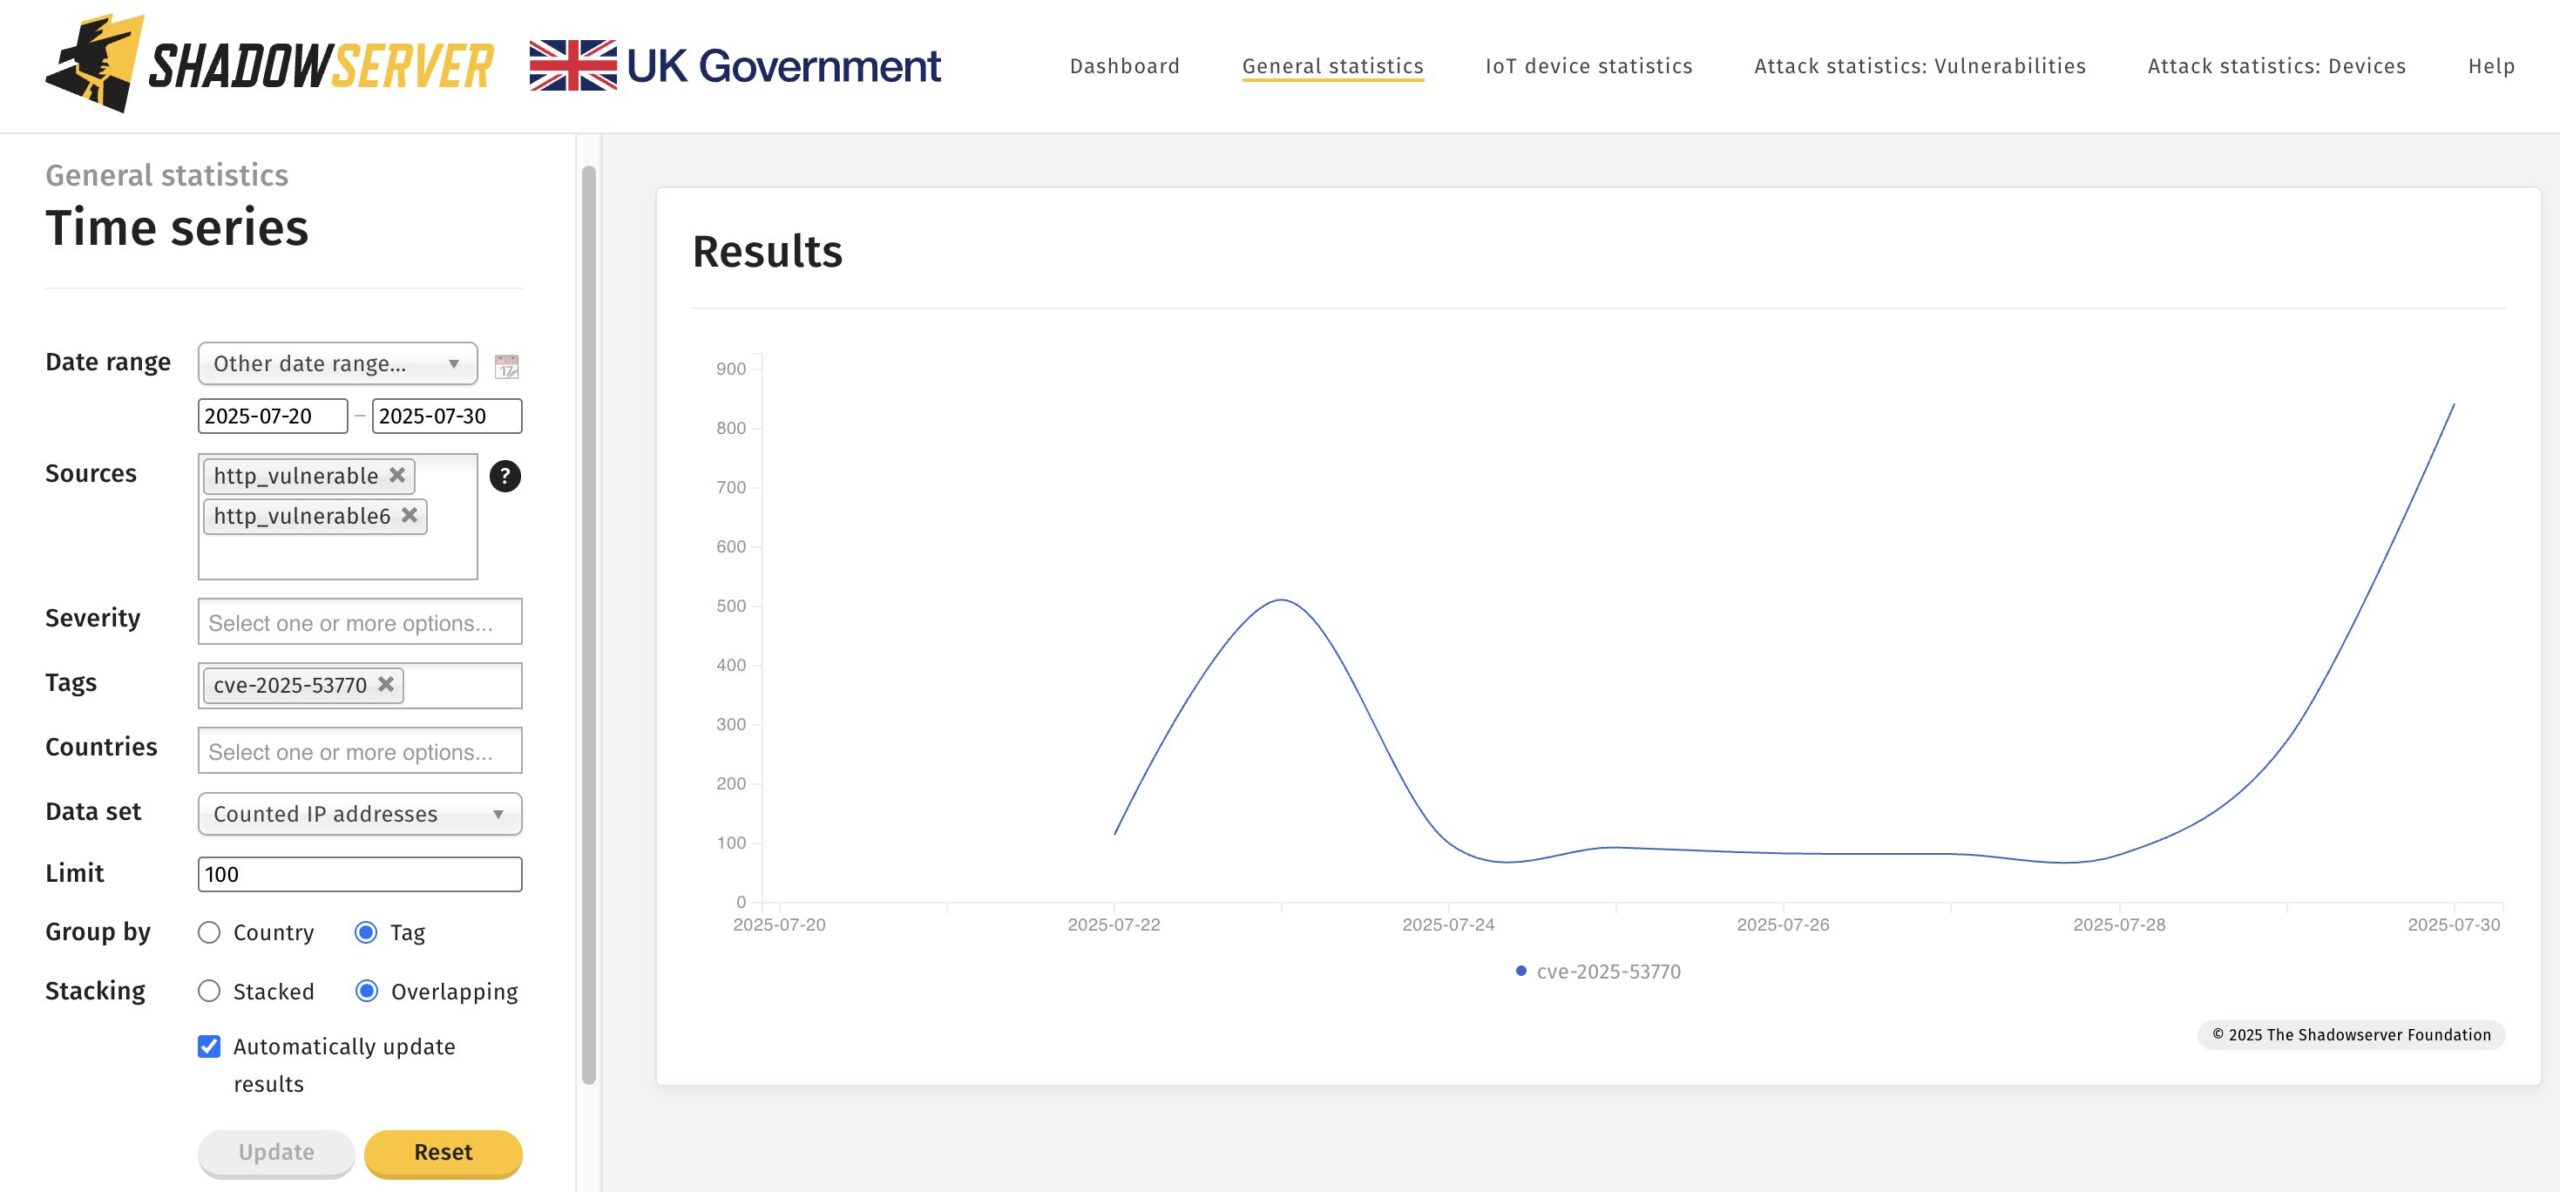
                                                                             Source: Shadowserver foundation

Microsoft has released emergency patches for all supported SharePoint versions. Organizations must rotate machine keys, enable Anti-Malware Scan Interface (AMSI), and conduct thorough security assessments.

CISA has added CVE-2025-53770 to its Known Exploited Vulnerabilities catalog with an emergency remediation deadline, underscoring the severity of the threat to critical infrastructure.

Multiple U.S. federal agencies, including the Department of Energy’s National Nuclear Security Administration and the Departments of Homeland Security, Health and Human Services, and Education, have been confirmed as victims. Additionally, state and local agencies nationwide have been affected.


BD Bank and CIRT alert for cyber attack


Check Also

SAP

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, …

