Sunday , October 11 2026

U.S. Weighs Ban on Chinese-Made Router TP-Link: WSJ reports

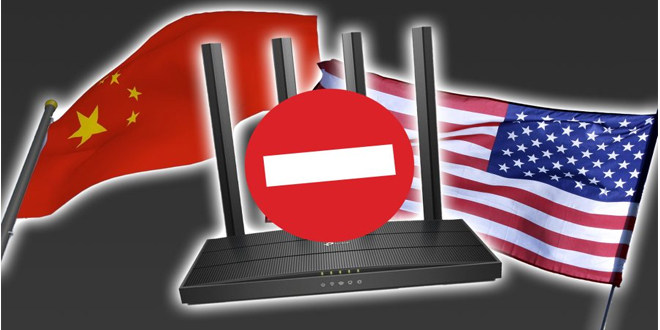
The US government is considering banning a well-known brand of Chinese-made home internet routers TP-Link due to concerns that they may be linked to cyberattacks and pose a national security risk.

TP-Link, which holds a 65% market share in the U.S. for high-speed cable modems, routers, and smart home devices, is under investigation by multiple federal agencies, as reported by the Wall Street Journal.

Anthropic unveils “OSS Scanner” Free AI Vulnerability Scanner for Open-Source Projects

Anthropic unveiled OSS Scanner on Thursday as an opt-in vulnerability scanner designed to enhance security within the open-source ecosystem through...
Read More
Anthropic unveils “OSS Scanner” Free AI Vulnerability Scanner for Open-Source Projects

Rise on RCE Exploits Targeting Hikvision Camera Flaw

There was a rise in scanning and remote code execution attempts on video surveillance devices in Ukraine from September 21...
Read More
Rise on RCE Exploits Targeting Hikvision Camera Flaw

FortiBleed Attack Compromised 80,000+ Devices, SonicWall Patches 4 SMA1000 Flaws CVSS 10

The FBI and U.S. Secret Service released a joint warning about cybersecurity. The warning said that the FortiBleed campaign is...
Read More
FortiBleed Attack Compromised 80,000+ Devices, SonicWall Patches 4 SMA1000 Flaws  CVSS 10

Critical Atlassian & IBM Flaws Expose Files and Enable Remote Code Execution

Atlassian has fixed CVE-2026-21589, a serious flaw in Atlassian Data Center with a score of 9.3. This bug allows an...
Read More
Critical Atlassian & IBM Flaws Expose Files and Enable Remote Code Execution

Citrix NetScaler SAML 0-Day Flaw Under Attack

Citrix has put out emergency security updates for a NetScaler SAML flaw that hackers are using. Known as CVE-2026-88779, this...
Read More
Citrix NetScaler SAML 0-Day Flaw Under Attack

Major Danish university breached, 200,000 users at risk

Hackers got into the identity and access management system at the Technical University of Denmark (DTU) and downloaded a lot...
Read More
Major Danish university breached, 200,000 users at risk

Microsoft’s X account hijacked to promote Clippy crypto scam

Microsoft's official X account was taken over to promote an unapproved Clippy-themed cryptocurrency. The tech giant’s X account, with 13...
Read More
Microsoft’s X account hijacked to promote Clippy crypto scam

Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

CPanel has put out security updates to fix three problems in cPanel & WHM. These problems could let attackers take...
Read More
Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Nearly 100,000 Bee Cheng Hiang customers had their email addresses leaked when an employee used an AI tool to generate...
Read More
Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Hackers to exploit a flaw in Zimbra mail servers that are connected to the Internet. They send special emails that...
Read More
Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

The Departments of Commerce, Defense, and Justice are investigating the company, according to sources.

A ban on TP-Link product sales may be implemented next year after President-elect Donald Trump takes office, according to the Journal.

TP-Link is the top choice on Amazon and provides web communications for the Defense Department and other federal agencies, according to the report.

In October, Microsoft released a cybersecurity report highlighting concerns about Chinese-made routers, revealing that hackers are using compromised devices from TP-Link.

Shares of Netgear (NTGR.O), opens new tab, a San Jose-based home networking company and a TP-Link rival, jumped more than 12% on Wednesday following the report, Reuters said.

New York post reported, “We welcome any opportunities to engage with the US government to demonstrate that our security practices are fully in line with industry security standards, and to demonstrate our ongoing commitment to the US market, US consumers, and addressing US national security risks,” an office spokeswoman told the Journal. 

Data breach! Ireland fines Meta $264 million, Australia $50m
Check Also

Money

Anthropic prepares “Claude Money” to analyze bank account and financial data

Anthropic is making a new Claude feature called “Money.” It’s a separate tab in the …