 InfoSecBulletin Cybersecurity for mankind
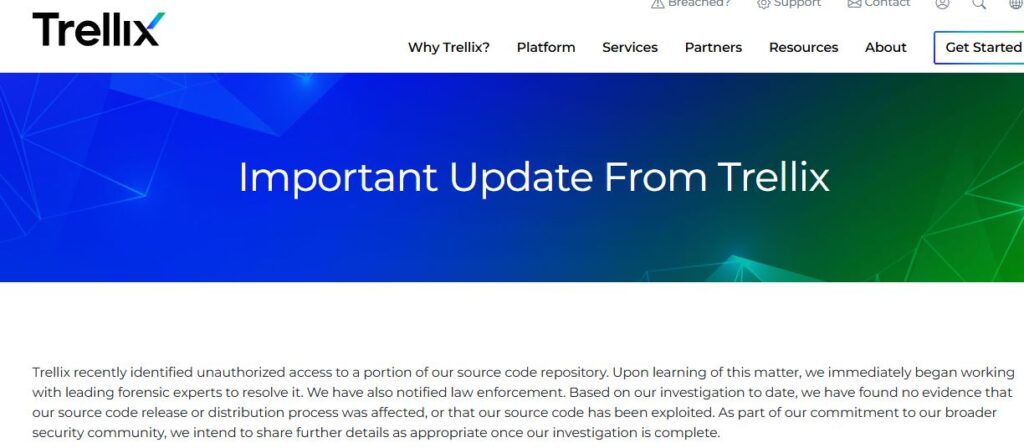
Trellix reported a security flaw that impacted part of its source code repository, but the company states there is no evidence of code being used wrongly. It quickly started a probe with experts and informed the law enforcement agency.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

“Trellix recently identified unauthorized access to a portion of our source code repository. Upon learning of this matter, we immediately began working with leading forensic experts to resolve it. We have also notified law enforcement.” reads the update published by the security firm. “Based on our investigation to date, we have found no evidence that our source code release or distribution process was affected, or that our source code has been exploited. As part of our commitment to our broader security community, we intend to share further details as appropriate once our investigation is complete.”
The company did not say who did the attack or how he did it. It is not clear how long the attackers had access to the repository.
Unauthorized access to a part of a source code can reveal important details, APIs, or passwords. Attackers might look at the code to find weaknesses, create attacks, or plan specific strikes. This can also result in stolen ideas, damage to reputation, and risks to the supply chain if changed code is shared with customers or partners.
Source code repositories are main targets for attackers who want to find weak spots, insert backdoors, or carry out supply chain attacks on customers.
The event is like other big code hacks that hit Microsoft, Okta, and LastPass in the last few years. Trellix has pledged transparency, stating it intends to share further technical details with the broader security community once its investigation concludes.



