 InfoSecBulletin Cybersecurity for mankind
In late October 2024, Cleafy’s Threat Intelligence team noticed a surge in a new Android malware known as TgToxic. However, deeper analysis showed that, despite some similarities to TgToxic commands, the code is quite different. Many typical TgToxic features are missing, and some commands are just placeholders. Consequently, the team have started tracking this malware as ToxicPanda.
ToxicPanda is part of the new generation of mobile malware, enabling hackers to take over accounts directly from infected devices using the On Device Fraud technique. This method has also been utilized by banking trojans like Medusa, Copybara, and BingoMod. A manual approach to this malware has benefits: it needs less skilled developers, allows targeting any banking customers, and can evade many detection measures used by banks and financial services.
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Cleafy’s Threat Intelligence team found that the attackers behind ToxicPanda are Chinese speakers. It’s unusual for them to focus on banking fraud in Europe and LATAM, suggesting a possible shift in their operational targets.
Further analysis of the ToxicPanda botnet infrastructure granted our team access to comprehensive telemetry data, revealing the full extent of this campaign:
Over 1500 Android devices were infected and remotely controlled during the ToxicPanda fraud campaign. Italy is the primary hotspot, accounting for more than 50% of the infected devices, followed by Portugal, Spain, France, and Perù.
This geographical distribution underscores the ToxicPanda botnet’s significant reach and adaptability. These numbers suggest that the operators are expanding their focus beyond primary European targets, hinting at a potential shift towards Latin America.
The Cleafy team notes, “While it shares some bot command similarities with the TgToxic family, the code diverges considerably from its original source”. This divergence led to the malware being reclassified as ToxicPanda.
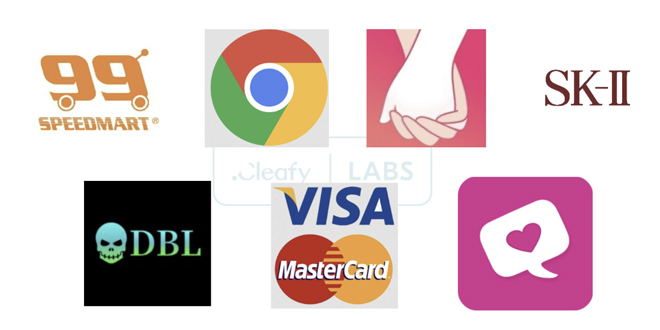
Cleafy’s Threat Intelligence team analysts identified the following icons during this investigation. It is evident that TA employs a mix of well-known brands (e.g., Google Chrome, VISA) and decoy icons resembling dating apps to enhance the malware’s deceptive capabilities and broaden its reach.
This malware is a modern remote access tool (RAT) that lets attackers conduct On-Device Fraud (ODF) on compromised Android devices. By operating directly on the device, attackers can avoid detection by security systems used by banks and financial institutions.
ToxicPanda leverages several advanced features that make it highly effective in banking fraud:
Accessibility Service Abuse:
By using Android’s accessibility services, ToxicPanda can gain higher permissions, alter user inputs, and collect data from banking apps, making it especially effective at compromising financial transactions.
Remote Control and Real-Time Fraud:
ToxicPanda allows attackers to remotely control infected devices, enabling them to initiate transactions, change account settings, and intercept OTPs to bypass two-factor authentication.
Obfuscation Techniques:
To avoid detection, the malware employs various obfuscation techniques, using “code-hiding techniques to make it difficult for security researchers to analyse the malware.”
Unique Botnet Structure and C2 Communication:
ToxicPanda’s botnet uses three hardcoded domains to connect with its command and control (C2) server. This setup streamlines initial connections and allows for controlled remote configuration.



