Friday , November 13 2026
warn

ALERT
Thousands of IP addresses compromised nationwide: CIRT warn

As Bangladesh prepares for the extended Eid-ul-Adha holidays, the BGD e-GOV Computer Incident Response Team (CIRT) has issued an urgent cybersecurity alert, warning of heightened cyber threats due to reduced monitoring and operational oversight during the festive period.
Source: BGD e-GOv CIRT

Current Threat Landscape:

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

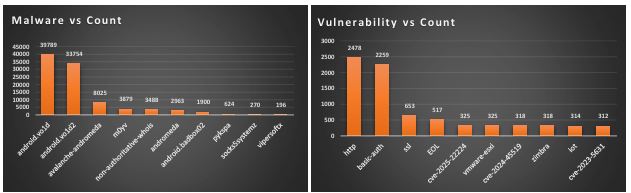
The CIRT’s Cyber Threat Intelligence Unit has detected widespread malware activity across the nation. Notably:
Android.vo1d and Avalanche-Andromeda malware variants have infected over 370,000 IP addresses.
24,362 IP addresses were flagged as vulnerable in the past week alone.

These malware campaigns exploit common security gaps, including:
Weak authentication protocols
Outdated or unpatched software
Critical Remote Code Execution (RCE) vulnerabilities

Top Threats Identified:

Recent threat intelligence highlights include:
High infection rates across mobile and desktop platforms
Major vulnerabilities in systems lacking routine patching
Risk of ransomware, data breaches, and unauthorized access

Recommended Mitigation Measures:

Organizations in both public and private sectors are urged to act swiftly:
Maintain 24/7 monitoring of systems and network activities.
Update all security tools, including SIEM, IDS/IPS, and WAF systems.
Enforce VPN access only with Multi-Factor Authentication (MFA).
Block connections from untrusted or public networks.
Apply all critical software and system updates immediately.
Securely back up all critical data and validate recovery processes.

Follow InfoSecBulletin.com for continuous updates on cybersecurity threats and best practices.

New Android Malware ‘Crocodilus’ Targets Banks in 8 Countries

 

Check Also

SAP

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, …