InfoSecBulletin Cybersecurity for mankind
Palo Alto Networks has issued advisories for two critical vulnerabilities in its PAN-OS. The vulnerabilities, CVE-2025-0108 and CVE-2025-0110, may enable attackers to bypass authentication and run arbitrary commands.
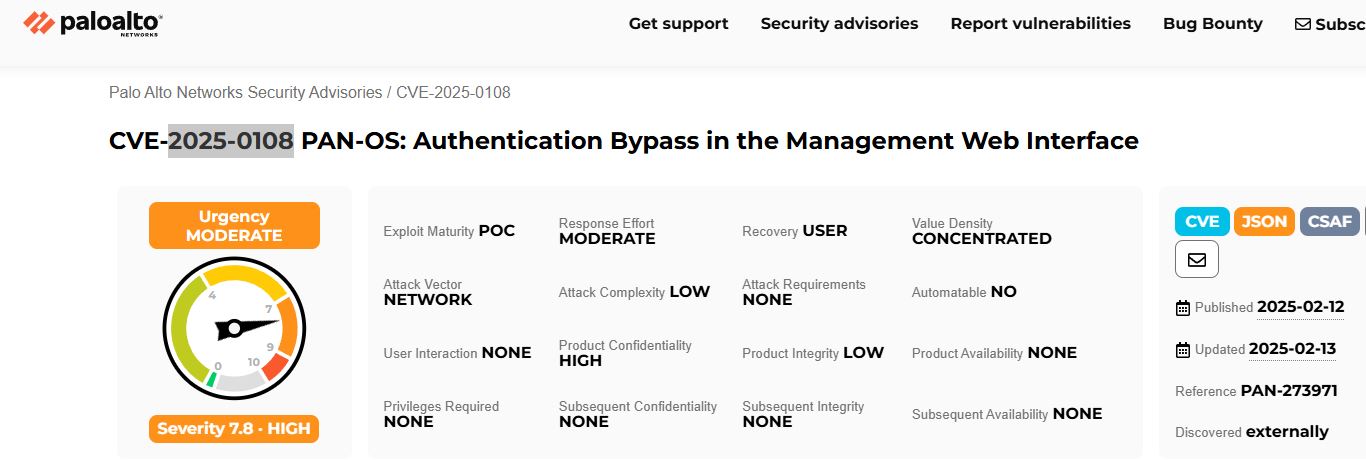
CVE-2025-0108: Authentication Bypass Vulnerability
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

A vulnerability in the PAN-OS management web interface (CVSSv3.1 score 7.8) allows unauthenticated attackers with network access to bypass authentication and run specific PHP scripts. This could compromise the integrity and confidentiality of PAN-OS, although it does not enable remote code execution.
“An authentication bypass in the Palo Alto Networks PAN-OS software enables an unauthenticated attacker with network access to the management web interface to bypass the authentication otherwise required by the PAN-OS management web interface and invoke certain PHP scripts,” the advisory explains.

CVE-2025-0110: Command Injection Vulnerability
The vulnerability (CVSSv3.1 score 7.3) is in the PAN-OS OpenConfig plugin. An authenticated administrator who can send gNMI requests to the PAN-OS management web interface could exploit this flaw to inject and execute arbitrary commands. These commands would have the privileges of the “_openconfig” user, who holds the Device Administrator role.
“A command injection vulnerability in the Palo Alto Networks PAN-OS OpenConfig plugin enables an authenticated administrator with the ability to make gNMI requests to the PAN-OS management web interface to bypass system restrictions and run arbitrary commands,” the advisory states.
Affected Versions and Mitigation:
CVE-2025-0108 impacts PAN-OS versions prior to 11.2.4-h4, 11.1.6-h1, 10.2.13-h3, and 10.1.14-h9. CVE-2025-0110 affects OpenConfig plugin versions before 2.1.2.
Palo Alto Networks has released updates to fix two vulnerabilities. Users are encouraged to update their PAN-OS software immediately and limit management interface access to trusted internal IP addresses only.
Ivanti Patches 3 Critical Flaws in Connect Secure and Policy Secure