 InfoSecBulletin Cybersecurity for mankind
NVIDIA has issued a dual security alert for developers and data scientists, announcing important updates for its Nsight Graphics and Merlin recommender system. Both vulnerabilities have a high CVSS score of 7.8 and can allow harmful code injection attacks that may compromise entire systems.
The flaws jeopardize the tools needed for creating future visual applications and AI models, threatening development processes.
Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

Anthropic prepares “Claude Money” to analyze bank account and financial data

GhostCode Phishing Kit Evades Microsoft 365 MFA to Hijack Accounts in 78 Seconds

CISA Warns of Cisco Secure Email Gateway 0-Day Flaw Actively Exploited in Attacks

VPN flaw exposed 246,000 personnel records in japan

Hackers deploy Casbaneiro Trojan that activates on bank websites

German police read Signal, Telegram, WhatsApp messages without breaking encryption

Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

CVE-2025-33206 is a vulnerability in Nsight Graphics, a tool for debugging graphics applications, affecting its Linux version. This flaw allows attackers to run malicious commands.
According to the security bulletin, “NVIDIA NSIGHT Graphics for Linux contains a vulnerability where an attacker could cause command injection”.
Exploiting this vulnerability could have serious consequences. The bulletin states that a successful attack might allow code execution, privilege escalation, data tampering, and denial of service. This means an attacker could take control of a developer’s workstation or crash their debugging environment.
The vulnerability affects “All versions prior to NSIGHT Graphics 2025.5” on Linux. Developers are urged to “download and install this software update from the Download NVIDIA NSIGHT Graphics page” to version 2025.5.
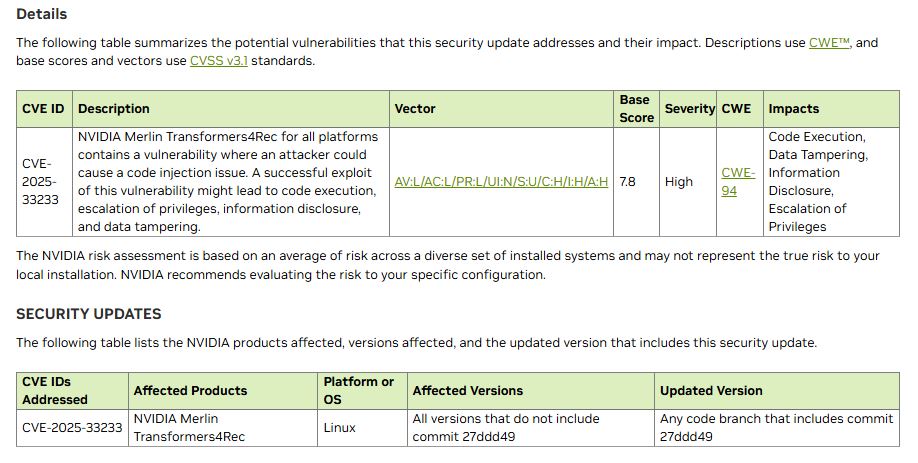
The second patch fixes a security flaw in NVIDIA Merlin Transformers4Rec, a library for creating recommendation systems with Transformers. Known as CVE-2025-33233, this vulnerability affects all platforms and is as severe as the graphics issue.
“NVIDIA Merlin Transformers4Rec for all platforms contains a vulnerability where an attacker could cause a code injection issue,” the advisory states.
Like the Nsight flaw, this vulnerability allows for a range of malicious outcomes, including “Code Execution, Data Tampering, Information Disclosure, and Escalation of Privileges”. For AI researchers working with sensitive datasets or proprietary models, the risk of information disclosure and data tampering is particularly acute.
All software versions lacking a specific security commit are affected. To fix this, users should update to any code branch with commit 27ddd49.



