 InfoSecBulletin Cybersecurity for mankind
Nigeria’s National Data Protection Commission (NDPC) fined Fidelity Bank ₦555.8 million for breaking customer data protection laws.
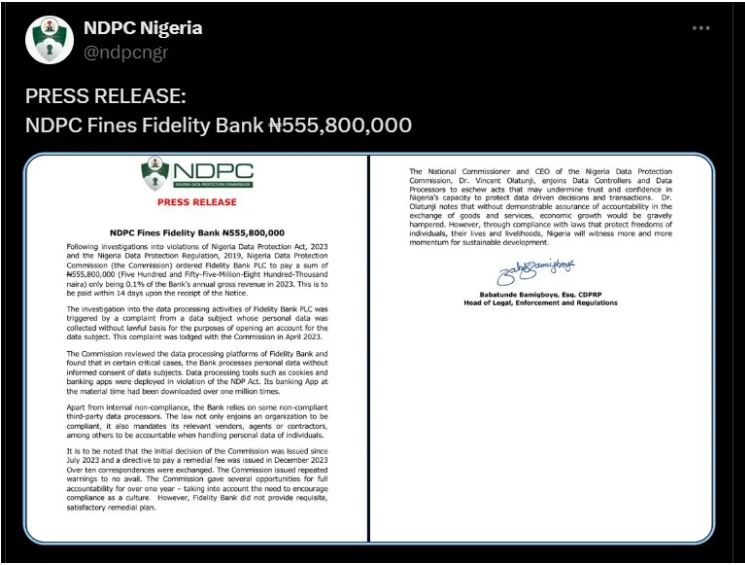
Punch reported that Olatunji said the top bank violated Nigeria’s Data Protection Act and Regulation, resulting in a large fine of 0.1% of the bank’s 2023 revenue.
Citrix NetScaler SAML 0-Day Flaw Under Attack

Major Danish university breached, 200,000 users at risk

Microsoft’s X account hijacked to promote Clippy crypto scam

Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

Commissioner emphasized the importance of following data protection rules and warned that not following them would result in heavy penalties.
“Data protection compliance is important, and we have stated that non-compliance will be punished. We have penalties that range from N10m or up to two per cent of gross earnings for the previous year,” Olatunji said.
He further explained that the bank’s poor cooperation during the investigation aggravated the penalty.
“We have observed serious breaches and have been working with them, investigating the issue since April 2023. But by the time we finalized our findings, they became arrogant, and we decided to issue a full penalty,” Olatunji added.
Fidelity Bank’s Response:
Reacting to this, Fidelity Bank strongly denied the allegations of a data breach. In a statement released on its website, the bank emphasized that it took data privacy and protection very seriously and had implemented robust security measures to safeguard customer information.
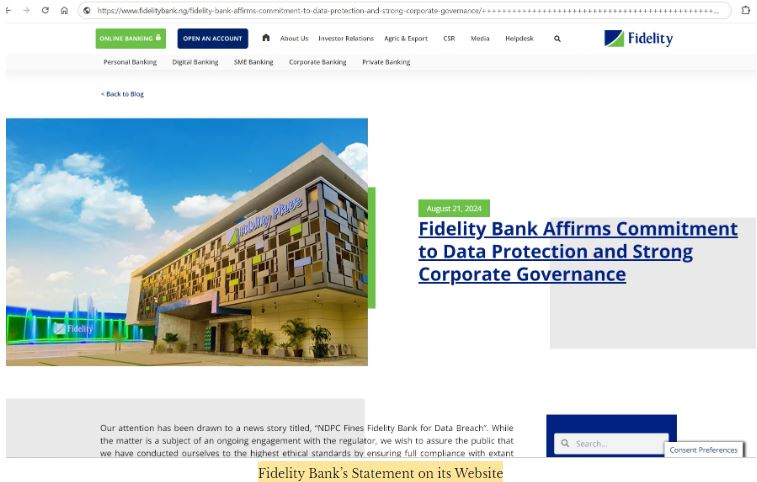
“On May 2nd 2023, we responded to the NDPC that the bank did not violate any law because there was no data breach and that the account opening process was not completed. On our part, we carried out due diligence by immediately blocking the account and subsequently closing the account when we did not receive the outstanding documents. At no point in the process was the account ever operational,” the bank said.
“As a Bank, we remain in discussions with the NDPC over an amicable resolution to this matter,” it added in its statement.



