 InfoSecBulletin Cybersecurity for mankind
Microsoft’s July 2024 Patch Tuesday includes security updates for 142 flaws, including two zero-days that are actively exploited and two that are publicly disclosed.
This Patch Tuesday fixed five critical vulnerabilities, all of which were remote code execution flaws.
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Hacker stole Meta GitHub repos; Stole Source Code

Urgent patch! Zoom,NVIDIA and IBM Patch 41 Security flaws

Microsoft patches record braking 1411 flaws; 2 zero days

Anthropic unveils “OSS Scanner” Free AI Vulnerability Scanner for Open-Source Projects

Rise on RCE Exploits Targeting Hikvision Camera Flaw

July 2024 Patch Tuesday Breakdown:
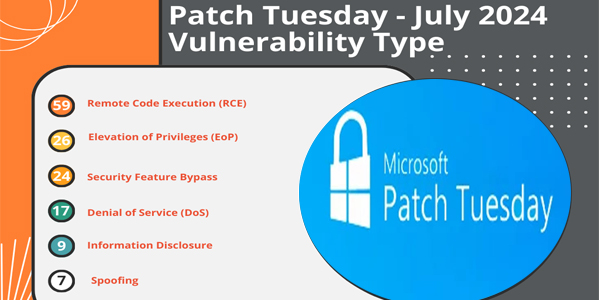
Here is the breakdown of vulnerabilities for July 2024 Patch Tuesday:
59 Remote Code Execution
26 Elevation of Privileges
24 Security Feature Bypass
17 Denial of Service
9 Information Disclosure
7 Spoofing
July 2024 Patch Tuesday Zero-Day Vulnerabilities:
Actively Exploited:
CVE-2024-38080: A vulnerability in Windows Hyper-V called “Opens a new window” could let an attacker gain system access by elevating account privileges. It is highly severe with a CVSS score of 7.8.
CVE-2024-38112: Opening a new window affects the Windows MSHTML Platform and can be used for spoofing, potentially granting unauthorized access to malicious individuals. It has a CVSS score of 7.5.
Publicly Disclosed:
CVE-2024-35264: “Opens a new window” is a vulnerability in .NET and Visual Studio that allows remote code execution. It has a high severity CVSS score of 8.1. Attackers can exploit this vulnerability by closing an HTTP/3 stream and executing remote code.
CVE-2024-37985: “Opens a new window” has a medium severity CVSS score of 5.9 and affects ARM64-based systems. According to Microsoft, an attacker could view heap memory from a privileged process running on the server by successfully exploiting this vulnerability.
The July 2024 Patch Tuesday Security Updates:
The list of resolved vulnerabilities in the July 2024 Patch Tuesday updates can be found in the full report. Each vulnerability is described along with the systems it affects. You can access the full report here.
Recent updates from other companies:
Other vendors who released updates or advisories in July 2024 include:
OpenSSH fixes new regreSSHion RCE vulnerability. A second similar vulnerability tracked as CVE-2024-6409 was disclosed yesterday as well.
Cisco disclosed an NX-OS Software CLI command Injection vulnerability that was exploited in attacks.
Fortinet fixes multiple vulnerabilities in FortiOS and other products.
Mozilla releases Firefox 128 with fixes for multiple vulnerabilities.
Citrix fixed flaws in Windows Virtual Delivery Agent and the Citrix Workspace app.
A GhostScript RCE flaw fixed in May 2024 is now exploited in attacks.
VMware fixes an HTML injection vulnerability in Cloud Director.



