 InfoSecBulletin Cybersecurity for mankind
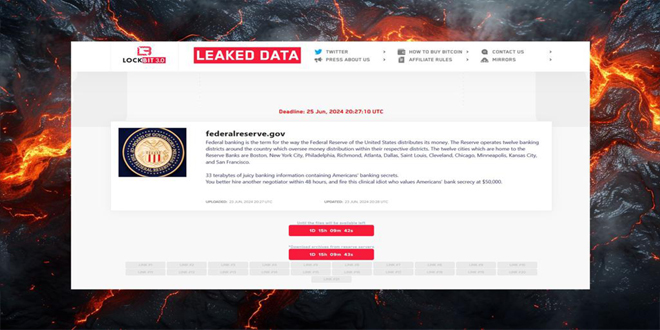
LockBit claimed that it breached Federal Reserve Board (Federalreserve.gov), the central banking system of the United States and exfiltrated 33 TB of sensitive data, including “Americans’ banking secrets.” “The group announced to release the stolen data on 25 June, 2024 20:27:10 UTC.”
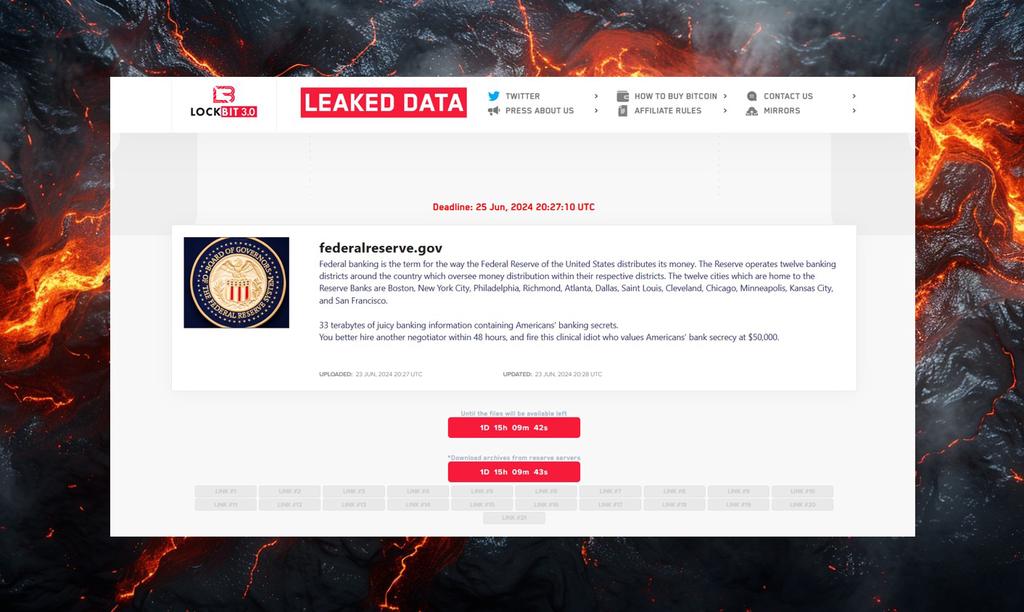
According to the post by the LockBit ransomware group, “Federal banking is the term for the way the Federal Reserve of the United States distributes its money. The Reserve operates twelve banking districts around the country which oversee money distribution within their respective districts. The twelve cities which are home to the Reserve Banks are Boston, New York City, Philadelphia, Richmond, Atlanta, Dallas, Saint Louis, Cleveland, Chicago, Minneapolis, Kansas City, and San Francisco.”
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

The group post reads, “33 terabytes of juicy banking information containing Americans’ banking secrets. You better hire another negotiator within 48 hours, and fire this clinical idiot who values Americans’ bank secrecy at $50,000.”
LockBit is well-known for its major data breaches, such as those affecting companies like Boeing, ICBC Bank, Bangkok Airways, and others. The NCC Group recently reported that LockBit is the most active group behind ransomware attacks, even though its infrastructure was seized and its alleged leader, Dmitry Yuryevich Khoroshev, was exposed by law enforcement authorities.
In early June, the FBI informed that they obtained over 7,000 LockBit decryption keys and was inviting victims of LockBit ransomware to come forward to help them recover their encrypted data for free.
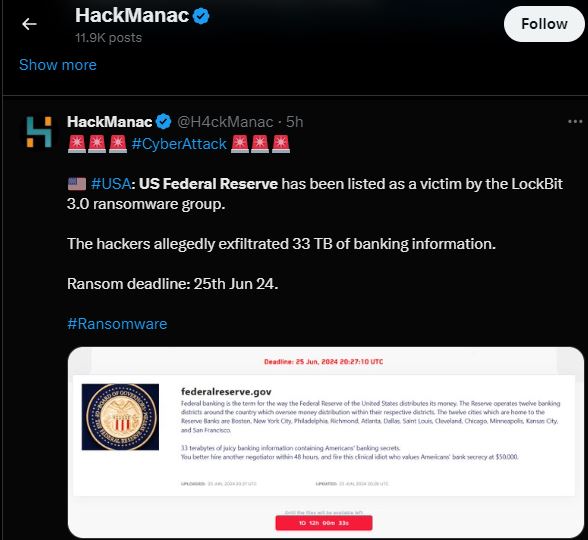
Hackmanac also post on x handle the same picture titled “USA: US Federal Reserve has been listed as a victim by the LockBit 3.0 ransomware group. The hackers allegedly exfiltrated 33 TB of banking information. Ransom deadline: 25th Jun 24.”
The Federal Reserve has not confirmed the breach or shared details about their response efforts, but federal agencies like CISA and the FBI are expected to be actively involved to address the situation.
The supposed cyberattack by LockBit 3.0 on the Federal Reserve shows that all sectors depending on digital infrastructure need to be more vigilant.
(Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided is for reference only, and users are responsible for relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)



