Saturday , November 7 2026
CCTV

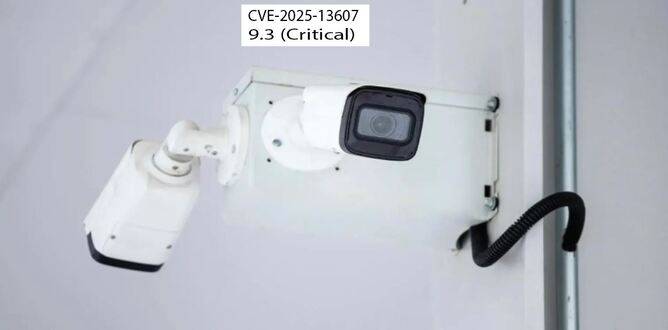
India-based CCTV cameras flaw allow attacker stealing video feeds, credentials

A severe security flaw has been revealed in various CCTV camera brands in India. This vulnerability enables attackers to access video feeds and steal login information without needing to authenticate.

CISA issued an alert on December 9, 2025, with code ICSA-25-343-03. Identifying threats from D-Link India Limited, Sparsh Securitech, and Securus CCTV.

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 million) in a cyber heist...
Read More
Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

OpenAI says that an automated system found and confirmed 948 different Linux kernel security issues in one run. These flaws...
Read More
OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

Apple credits Md Rasel Bhuyan and fellow researcher Musaab Khan for discovering an out-of-bounds write vulnerability affecting multiple Apple operating...
Read More
Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

A flaw in Zyxel GS1900 switches was being used by hackers, and the update to fix it did not work....
Read More
WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Hackers used ARTEX, a free tool for testing security with AI, to attack over 200 organizations in 14 countries. The...
Read More
Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

A cybersecurity incident with Spanish travel tech company Amadeus IT Group has worried the global airline industry. Hackers got into...
Read More
Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

The vulnerability, listed as missing authentication for a critical function (CWE-306), is CVE-2025-13607 and has a critical CVSS v4 score of 9.3. The flaw allows remote attackers to exploit a weak URL endpoint without needing authentication.

Unauthorized access to sensitive camera configuration data, including admin credentials, has been found. The D-Link DCS-F5614-L1 camera model with firmware versions v1.03.038 and earlier is affected.

There are no specific models for Sparsh Securitech and Securus CCTV, but organizations using their cameras have similar risks.

D-Link has issued a security update for affected devices and has released a security advisory. They strongly recommend that users promptly install the patches and verify the updates by checking the firmware version on device interfaces.

Organizations should reach out to vendor support to find out which models are impacted and receive guidance for fixes. CISA suggests important defensive steps, such as reducing network exposure by isolating cameras from the internet.


Check Also

NetamLoader

NetamLoader malware to attack Win10: Customized for Gov.t in Asia

A new malware framework named NetamLoader is attacking a special version of Windows 10 used …