Saturday , November 14 2026

Hackers To Use HTTP Client Tools To Compromise Microsoft 365 Accounts

Hackers are using HTTP client tools for advanced account takeover attacks on Microsoft 365. Seventy-eight percent of Microsoft 365 tenants have been targeted by attacks, showing the changing tactics of threat actors. HTTP client tools are software that allows users to send HTTP requests and receive responses from web servers.
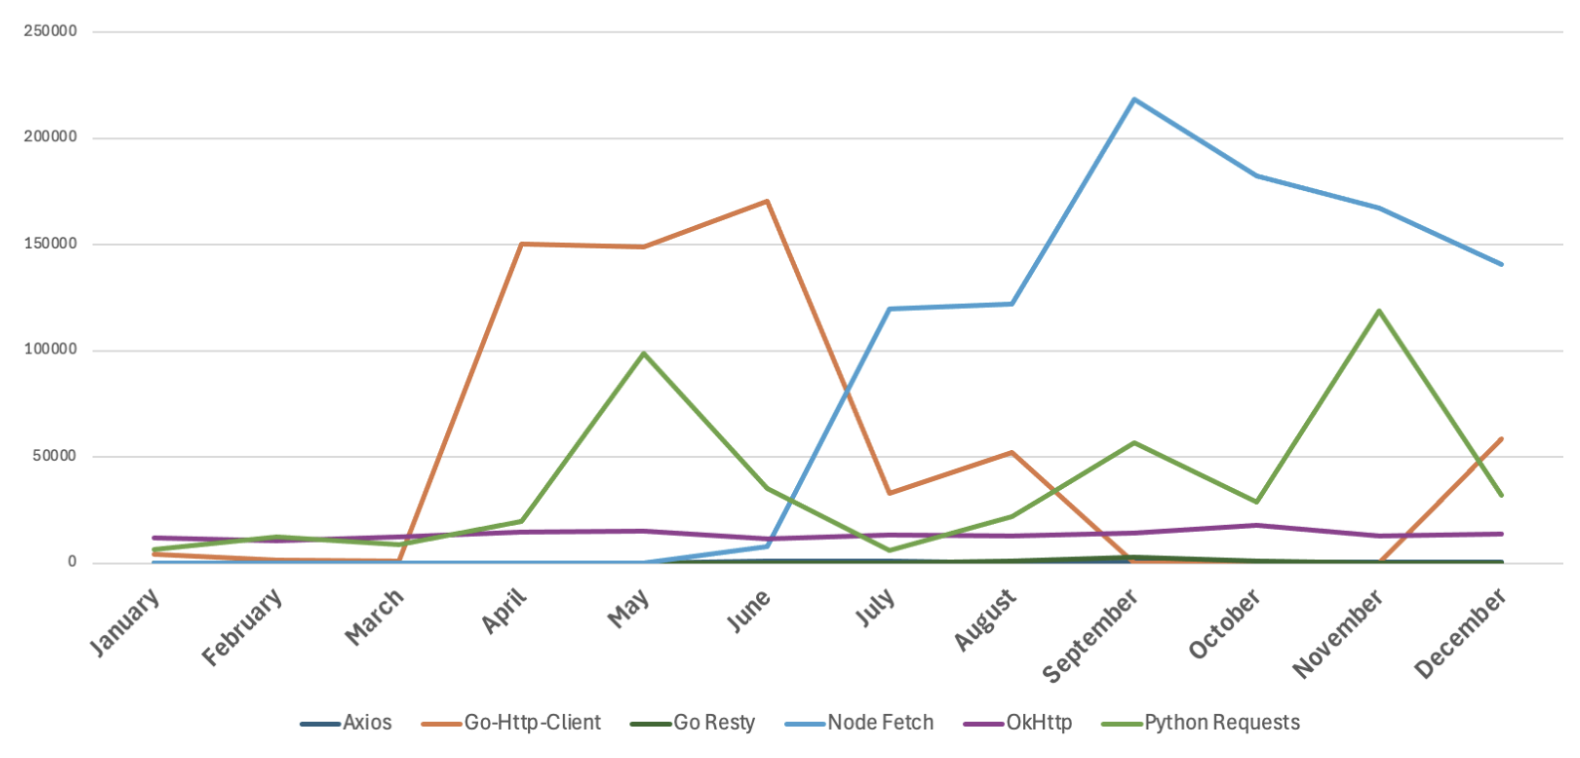
ATO attacks leveraging HTTP clients by volume of affected user-accounts (JAN – DEC 2024).

These tools enable customization of request methods (like GET, POST, PUT, DELETE), headers, and payloads, making them useful for both legitimate and malicious activities.

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

In February 2018, Proofpoint researchers found a widespread campaign targeting Microsoft 365 environments that used an unusual version of the OkHttp client (‘okhttp/3.2.0’).

Proofpoint researchers observed that a nearly four-year campaign targeted high-value individuals, particularly C-level executives and privileged users.

   Volume of Node Fetch based account takeover attacks, by targeted vertical (JUN-DEC 2024).

Attackers used user enumeration to find valid email addresses before launching spear phishing and password spraying attacks.

Since 2018, HTTP clients have been key in account takeover (ATO) attacks. By early 2024, OkHttp variants were popular, but by March 2024, a wider variety of HTTP clients emerged.

A recent campaign using the Axios HTTP client successfully compromised 43% of targeted user accounts. When combined with Adversary-in-the-Middle (AiTM) platforms like Evilginx, Axios can steal credentials, MFA tokens, and session tokens. To read full report click here.

Google patches 47 Android flaws, Including Actively Exploited CVE-2024-53104

 

Check Also

November 2026

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in …