 InfoSecBulletin Cybersecurity for mankind

Hackers misuse Microsoft Entra ID accounts to steal data from Microsoft 365 and Azure. A very advanced cyberattack by a group called Storm-2949 is aiming at Microsoft Entra ID accounts to take sensitive data from Microsoft 365 and Azure.
Storm-2949 used real cloud management tools to get deep access to SaaS, PaaS, and IaaS environments instead of using harmful payloads.
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

The attack started with focused social tricks aimed at important users, like IT workers and top managers. The bad actor took advantage of Microsoft’s Self-Service Password Reset (SSPR) by deceiving users into agreeing to multifactor authentication (MFA) requests.
Attackers pretended to be IT support staff and got victims to approve MFA requests by saying they were checking accounts.
Microsoft says the attack shows a rising trend in cloud attacks, where hackers focus more on stealing identities than using usual malware.
Once they got approval, the attackers changed passwords, took away existing login methods, and set up their own MFA devices. This locked out real users while they kept access.
Hackers Exploit Entra ID
After getting in, Storm-2949 quickly started taking data from Microsoft 365 services, like OneDrive and SharePoint.
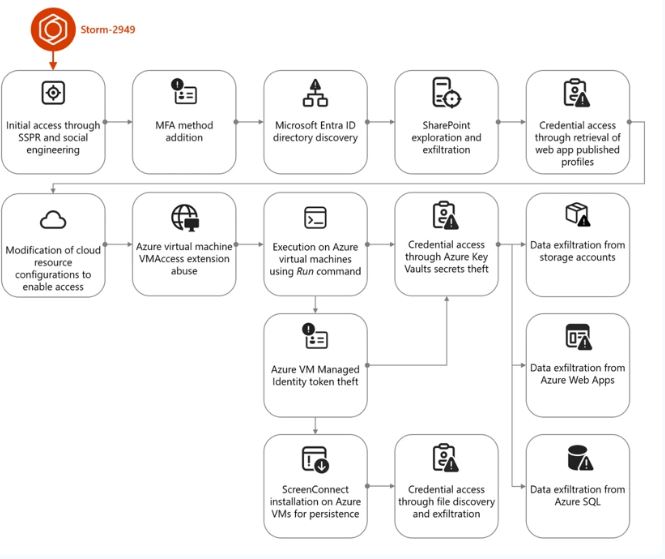
Storm-2949 attack diagram (Source : Microsoft).
The attackers aimed at important files like VPN setups and remote access steps, showing they were ready to move laterally.
Detection and Defense
Microsoft Defender was key in finding the attack by linking signals from identity, cloud, and endpoint areas. This shows how important integrated detection systems are for cloud security today.
This campaign shows a change to attacks focused on identity in cloud systems. By misusing real admin tools, attackers can work quietly with few signs of a breach.
Organizations are advised to:
Strengthen MFA steps and watch for strange approvals.
Limit RBAC permissions by using the least access needed.
Keep an eye on Microsoft Graph API activity for odd queries.
Secure Key Vault access and check how secrets are used.
Activate cross-domain detection with tools like Microsoft Defender XDR.
As more people use the cloud, protecting identity and access is very important to stop big data breaches.
Indicators of compromise (IOCs):
| Indicator | Type | Description |
| 176.123.4[.]44 | IP address | Attacker egressed from this address |
| 91.208.197[.]87 | IP address | Attacker egressed from this address |
| 185.241.208[.]243 | IP address | ScreenConnect instance used by Attacker |



