 InfoSecBulletin Cybersecurity for mankind
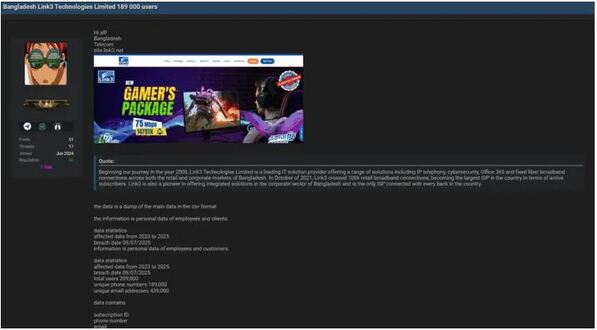
A threat actor claims to have breached Link3, a major IT solutions and internet service provider based in Bangladesh. The data has been put up for sale on a dark web forum.
According to the forum post: Link3 is the largest ISP in the country by active subscribers, offering essential services like fiber broadband and IT solutions for businesses and individuals. It plays a crucial role in Bangladesh’s digital infrastructure and is the only ISP connected to various banks in the nation.
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

The threat actor claims the breach occurred on July 9, 2025, and affects 189,000 unique users, encompassing both customers and employees. The compromised dataset, which is being offered to sell for $400, allegedly contains a wide range of sensitive personal and account information. The exposure of such detailed information could potentially lead to various malicious activities, including identity theft, phishing campaigns, and unauthorized account access.
The leaked data allegedly includes:
Subscription ID
Phone number
Email address
Full username
Subscription password
Full address
Subscription category and status
SMTP logs and newsletter emails
If the hacker’s claim is true, the exposure of personal information could result in identity theft, phishing attacks, financial fraud, and unauthorized access to private accounts.
Users are urged to change passwords and remain vigilant. The breach also underscores the urgent need for stronger cybersecurity measures within the telecommunications sector in Bangladesh.
(Source: Darkweb, Undercode)
(Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided here is for reference only, and users are responsible for reffering and relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)



