 InfoSecBulletin Cybersecurity for mankind
Cross-Site Scripting (XSS) is one of the oldest and most persistent vulnerabilities in modern applications. Despite being recognized for over 20 years, it still affects both legacy systems and new cloud-native architectures.
The Microsoft Security Response Center (MSRC) noted that the threat of XSS remains significant, as it regularly receives reports about it across various services and applications.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

A recent MSRC report highlighted the ongoing threat of XSS vulnerabilities, noting that advanced security measures like Content Security Policies (CSP) and secure libraries are still insufficient.
Since January 2024, the MSRC has addressed over 970 XSS cases, showing their ongoing commitment to handling this type of vulnerability.
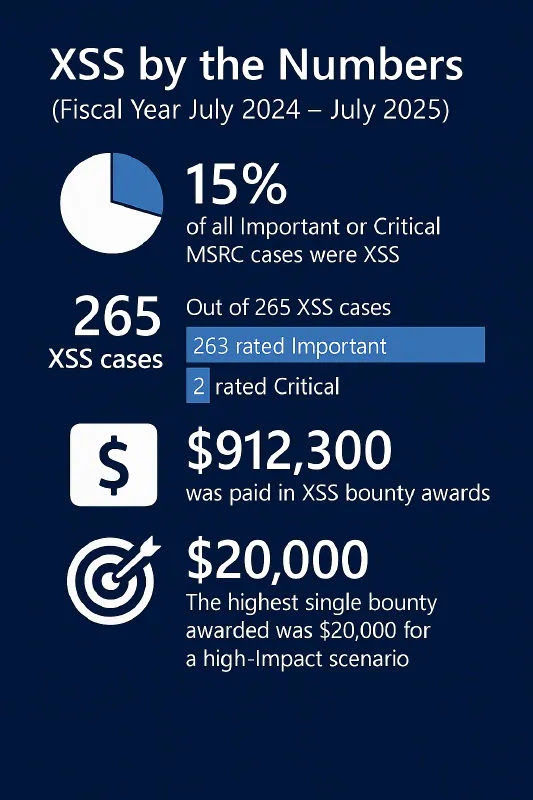
XSS By The Numbers:
Between July 2024 and July 2025, XSS vulnerabilities accounted for 15% of all “Important” or “Critical” security cases handled by the MSRC.
The center handled 265 XSS cases, with 263 deemed Important and two Critical. Microsoft rewarded security researchers with $912,300 for identifying these vulnerabilities.
The highest reward for a significant XSS attack, like token theft or a zero-click exploit, was $20,000. Click here to read the full report here.



