 InfoSecBulletin Cybersecurity for mankind
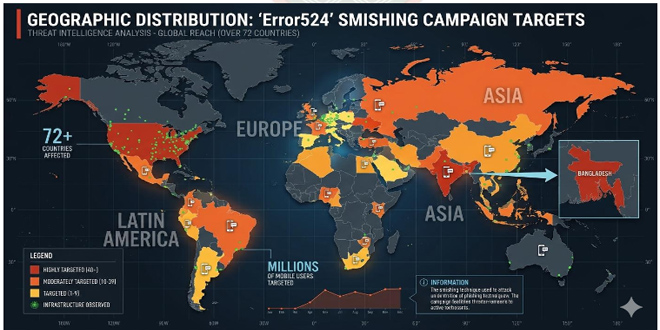
A global smishing scam dubbed “Error524” is hitting many countries, including Bangladesh. BGD e-Gov CIRT said, this scam uses Phishing-as-a-Service (PhaaS) tools to send SMS messages with harmful links.
These links redirect victims to highly convincing phishing websites designed to steal:
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Personal information
Banking credentials
Payment card data
This campaign is a big threat to both organizations and individuals because it uses automation and pretends to be trusted services.
Threat Overview:
Active since late 2025, the Error524 campaign uses:
Shortened malicious URLs, Cloud-based infrastructure, Domain rotation, evasion techniques and so on.
Attackers mimic trusted services such as:
Financial institutions, Government portals, providers, Logistics & delivery services, Retail and loyalty programs.
Impact on Bangladesh
Bangladesh is among the targeted countries, making several sectors vulnerable:
Sector Risk
Financial Services Banking credential theft
Government Services Fake citizen portals
Telecommunications SMS spoofing & distribution
Logistics/Delivery Fake parcel notifications
E-commerce Reward/payment scams
Potential consequences:
Financial fraud
Identity theft
Data breaches
Loss of public trust
Attack Methodology
- Smishing Distribution
Victims receive fraudulent SMS messages with lures such as:
Delivery updates
Unpaid toll/fine alerts
Account verification requests
Reward offers
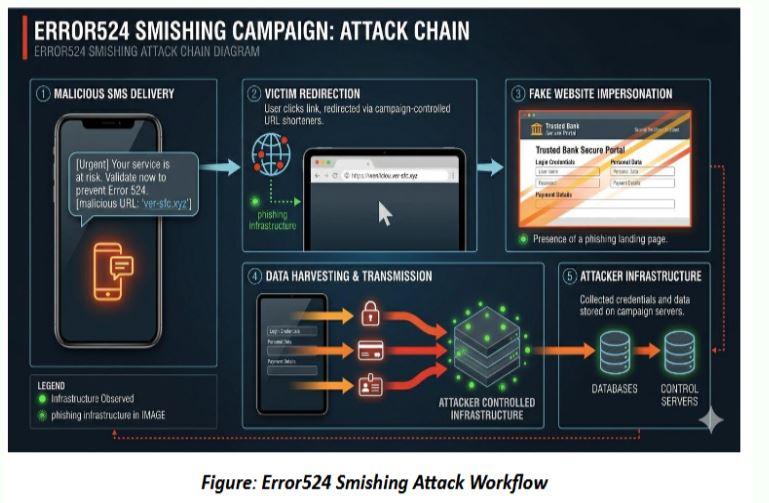
2. Phishing Redirection
Users click a link → redirected to fake websites
Pages closely mimic real platforms.
3. Data Collection
Victims are tricked into submitting:
Login credentials
Personal identification info
Card details
One-time passwords (OTP)
4. Data Exfiltration
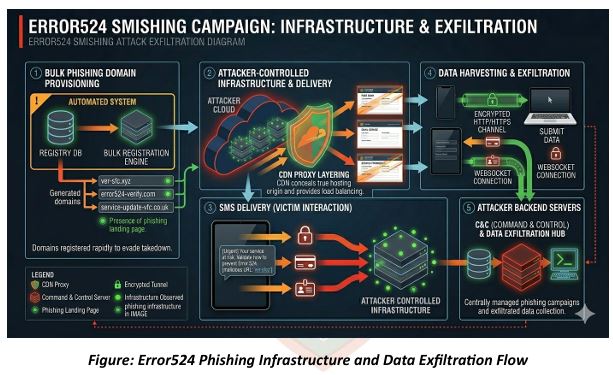
Stolen data is sent via:
WebSocket channels
HTTP POST requests
Centralized phishing servers
Technical Analysis
Infrastructure Characteristics
CDN masking (Cloudflare) to hide origin servers
Hosting on cloud platforms (Tencent, Alibaba)
Bulk domain registrations
Suspicious TLDs: .top, .ink, .bond, .click, .vip, .icu
Evasion Techniques:
Geofencing: Targets specific countries (including Bangladesh)
CAPTCHA filtering: Blocks security scanners
Fake Error Pages: Displays “Error 524” to avoid detection
Device Fingerprinting: Detects sandbox environments
Indicators of Compromise (IOCs)
Malicious Domains (Examples)
americanexpress-bonus306[.]ink
fullcopechilex[.]top
telcoe[.]shop
portalcity[.]top
Suspicious IPs
47.82.154[.]2 (Alibaba Cloud)
43.165.6[.]36 (Tencent Cloud)
154.81.166[.]17 (Credential harvesting)
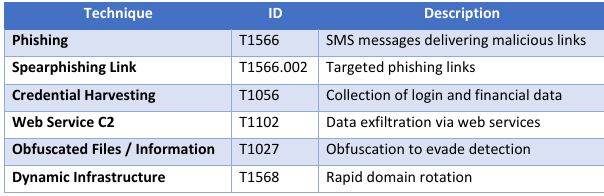
MITRE ATT&CK Mapping
The Error524 smishing campaign shows that SMS phishing attacks are getting smarter. Bangladesh is one of the target locations, so both groups and people need to take steps to stay safe and be alert to reduce risks.



