 InfoSecBulletin Cybersecurity for mankind
The FBI and CISA reported on Wednesday that the ransomware group Ghost has been exploiting software and firmware vulnerabilities as recently as January.
The group targets internet services with old, unpatched vulnerabilities that users could have addressed years ago. Cybersecurity researchers began alerting the public about the group in 2021.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

“This indiscriminate targeting of networks containing vulnerabilities has led to the compromise of organizations across more than 70 countries, including organizations in China,” says the alert, released with the Multi-State Information Sharing and Analysis Center (MS-ISAC).
Vulnerabilities include unpatched bugs in Fortinet security appliances, servers using Adobe ColdFusion, and Microsoft Exchange servers vulnerable to the ProxyShell attack.
Since 2021, various sectors, including critical infrastructure, schools, healthcare, government networks, religious institutions, tech companies, and many small to medium businesses, have been targeted. The main aim is financial gain, with ransom demands often exceeding hundreds of thousands of dollars.
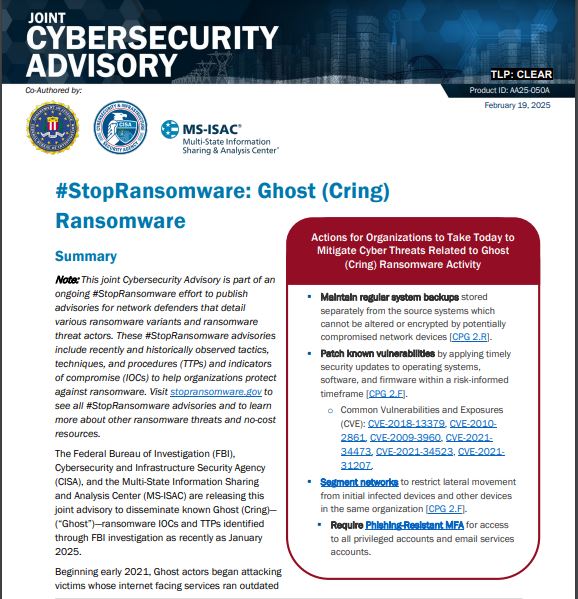
“Persistence is not a major focus for Ghost actors, as they typically only spend a few days on victim networks,” the agencies say. “In multiple instances, they have been observed proceeding from initial compromise to the deployment of ransomware within the same day.”
The group uses well-known hacking tools like Cobalt Strike and Mimikatz, and the malware they deploy often has names like Cring.exe, Ghost.exe, ElysiumO.exe, and Locker.exe, according to the alert.
“The impact of Ghost ransomware activity varies widely on a victim-to-victim basis,” the agencies say. “Ghost actors tend to move to other targets when confronted with hardened systems, such as those where proper network segmentation prevents lateral moment to other devices.”



