 InfoSecBulletin Cybersecurity for mankind
DeepSeek, a Chinese AI startup that recently surpassed OpenAI’s ChatGPT as the top free app on Apple’s App Store in the U.S., is experiencing a major cyber attack and has limit new user registrations.
Founded in 2023, DeepSeek has rapidly become a strong contender in the AI industry, specializing in large language models and pursuing artificial general intelligence (AGI).
Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

The open-source model DeepSeek-R1 is recognized for its efficiency and performance. This cyber incident is significant for DeepSeek, as it enjoys the success of its DeepSeek-V3 model.
DeepSeek-V3 was launched with great enthusiasm and is considered a significant advancement in AI technology, providing excellent performance on multiple benchmarks at a competitive price.
DeepSeek-V3, with 671 billion parameters and a unique Mixture-of-Experts architecture, is gaining attention for surpassing other open-source models and competing with major closed-source models from OpenAI and Anthropic.
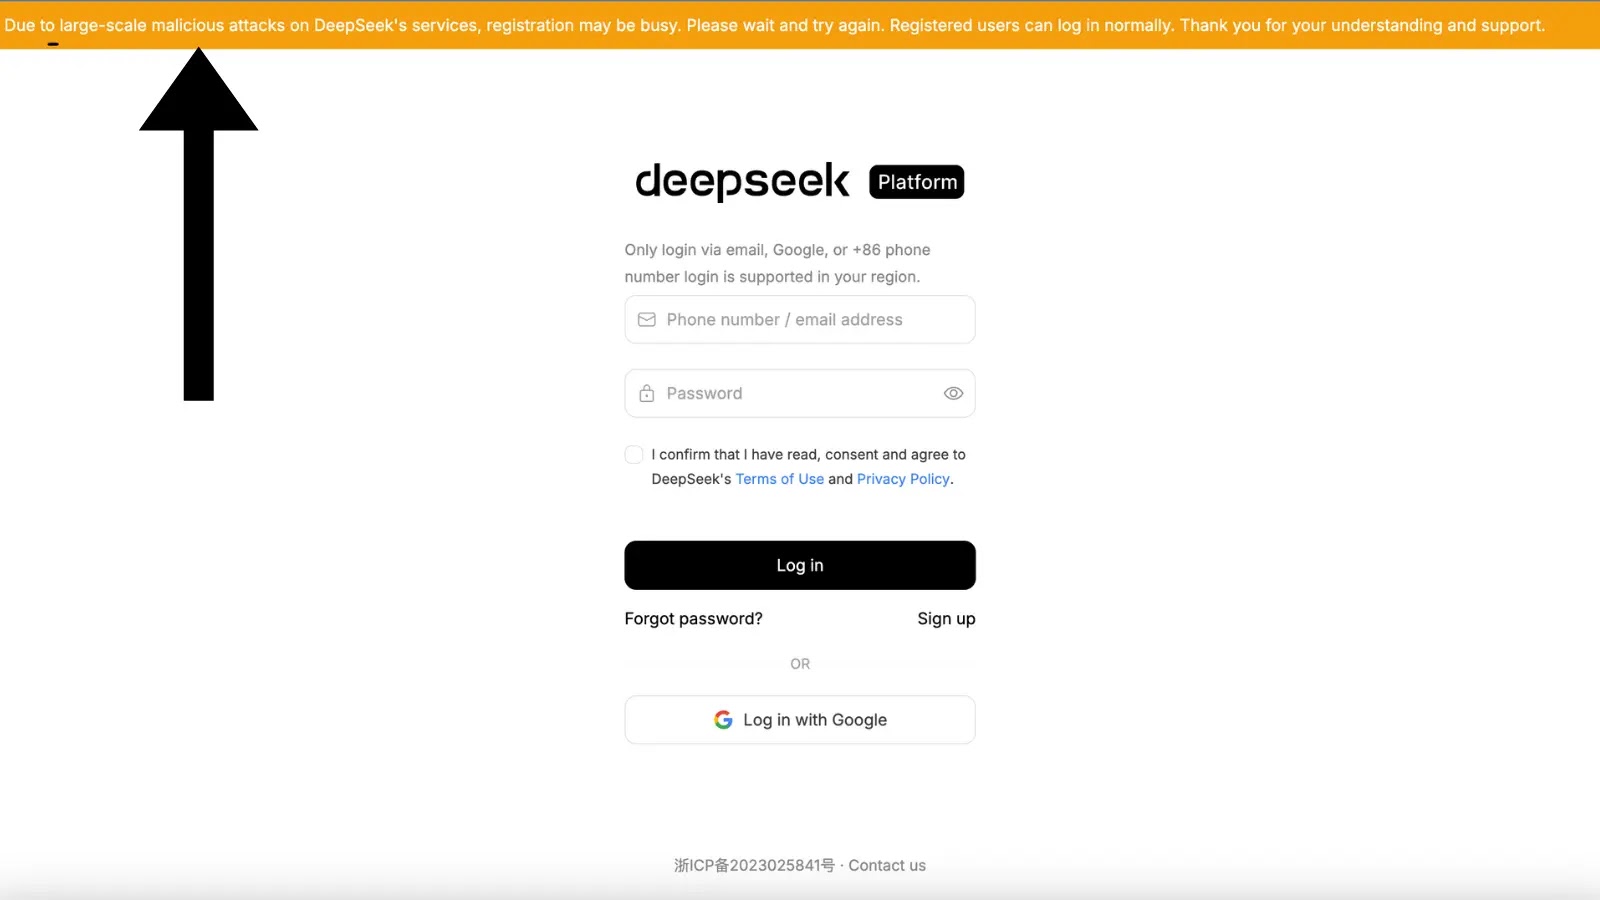
DeepSeek reports that a large-scale, malicious attack is affecting its services.
“Due to large-scale malicious attacks on DeepSeek’s services, we are temporarily limiting registrations to ensure continued service for existing users,” the company stated on its status page. Current users can still log in without any issues.
The attack coincided with DeepSeek’s rapid rise in popularity, as its AI Assistant app just surpassed ChatGPT in downloads, affecting global technology markets. The increase in users has made the company a prime target for cybercriminals.
DeepSeek’s recent success comes from the launch of the DeepSeek-R1 model, an open-source AI known for its advanced reasoning and cost-effectiveness compared to other top AI models. The model’s success has gained a large user base and shaken the tech industry, resulting in a notable drop in AI stocks.
Cybersecurity experts suggest that rapid company growth can attract cyber attacks. Jake Moore, Global Cyber Security Advisor at ESET, noted that DeepSeek’s recent visibility makes it a target for cybercriminals.
The cyber attack has raised concerns about the security of user data and the integrity of DeepSeek’s platform.



