InfoSecBulletin Cybersecurity for mankind
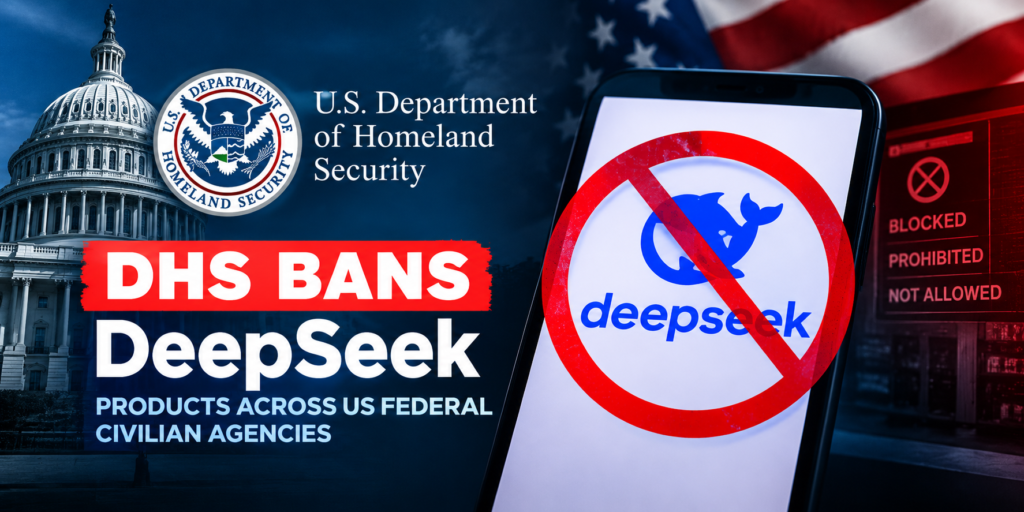
The U.S. Department of Homeland Security (DHS) ordered federal agencies to stop using DeepSeek products and remove it from all government systems. The order includes products from the Chinese AI company’s partners and other products and services made with DeepSeek technology.
The DHS is now taking regulatory action to limit the use of DeepSeek and derivatives on critical systems in the United States, and has issued a notice of order for agencies to:
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Hacker stole Meta GitHub repos; Stole Source Code

Urgent patch! Zoom,NVIDIA and IBM Patch 41 Security flaws

Microsoft patches record braking 1411 flaws; 2 zero days

Immediately exclude covered products from procurement, including approved-product lists and purchasing marketplaces.
Immediately remove covered products from agency IT systems, or seek an exception.
Submit any exception requests within 60 days of the order’s issuance, explaining the justification and proposed risk mitigations. CISA will review requests and issue written approvals or denials.
The order is for federal agencies under DHS and does not stop private or consumer use. DHS said the order is due to worries about the Chinese government getting into DeepSeek systems to gather personal data, track users, and possibly send sensitive government information to China.
The document talks about worries regarding possible malware in DeepSeek models. It mentions a report from NowSecure in February 2025 that found security problems in the DeepSeek iOS app.
NowSecure looked at the app and saw that it had unprotected data transfers, weak encryption methods, unsafe local storage, risks of tracking users’ fingerprints, and it shared data with ByteDance, the Chinese company that owns TikTok.
The order was released in the Federal Register today, one day after it was on Public Inspection.
Executive agencies can ask for exceptions within 60 days after the order is issued. If agencies can’t follow this order due to internal limits, CISA will give the needed technical help.
Related news:
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines