InfoSecBulletin Cybersecurity for mankind
Numerous thefts of multimillion-dollar proportions continue to haunt the cryptocurrency realm, and the most recent occurrence involves attackers draining tens of millions from numerous wallets linked to CoinEx.
There was a coordinated attack on different automaker websites. The attackers managed to collect vehicle IDs and other important car information. They then tried to sell this information on Telegram. Moreover, the infamous Remcos RAT has made a comeback, initiating a clandestine phishing attack targeting several organizations in Colombia.
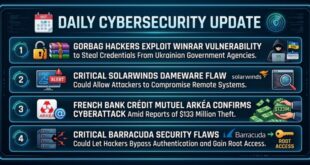
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

Delve into the latest trends from the past 24 hours to stay informed
The platform’s wallets were breached, resulting in the theft of $55 million worth of ETH, TRON, and Polygon coins. CoinEx has officially acknowledged the occurrence of this significant hack. The affected wallet addresses were identified and isolated by the firm.
ALSO READ:
Researcher awarded discovering a Two-Factor Authentication bypass in Facebook
Around 15,000 hacked accounts were discovered by cybersecurity firm Kasada, which were then utilized in an automated attack intended to seize control of various automaker websites. The attack aimed to obtain valuable information, such as vehicle IDs along with car makes and models. Subsequently, this confidential data was made available for sale in exclusive Telegram channels.
Microsoft has successfully deciphered a novel phishing campaign called Storm-0324, in which the perpetrators utilized a publicly accessible tool named TeamsPhishers to breach corporate networks. In the past, the threat actor has been involved as both an initial access broker and a member of the esteemed FIN7 APT group.
A new phishing campaign has been discovered by researchers. This campaign utilizes Microsoft Word documents as a means to distribute harmful malware such as OriginBot, Agent Tesla, and RedLine Clipper onto targeted individuals’ systems. These malware strains enable attackers to siphon cryptocurrency and steal sensitive data.
macOS business users are now being targeted by a dangerous new malware called MetaStealer. This emerging threat has recently been detected in the wild and requires immediate attention. The malware, coded in Golang, is spread using cunning social engineering techniques. Attackers masquerade as fake clients and entice unsuspecting victims into running harmful payloads.