Monday , September 14 2026

Cyber attack on Sparrso; Hacker’s claim, Sparrso’s denial

A hacktivist group named “Team Network Nine” claimed a cyber attack on “Bangladesh Space Research and Remote Sensing Organization (SPARSO). The group claimed that the December 1 attack resulted in Sparrso’s website being down for 1 hour.
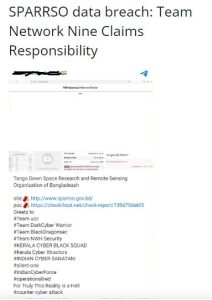
Source: “Team Network Nine” online channel

An Indian media reported on the issue. According to the report, the hacktivist group in coordination with other groups carried out a successful attack on Sparrso’s site. However, the report did not mention any information about how much information Sparrso had leaked.

German police read Signal, Telegram, WhatsApp messages without breaking encryption

German law enforcement agencies are using features built into apps such as WhatsApp to monitor people’s messages without breaking their...
Read More
German police read Signal, Telegram, WhatsApp messages without breaking encryption

Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

GitLab has released an important security update to fix two serious problems. These issues could allow unauthorized file access and...
Read More
Urgent Patch! cPanel, GitLab Flaws Expose Users to RCE, File and Credential Theft

Palo Alto PAN-OS Flaw Enables Root Arbitrary Code Execution

Palo Alto Networks has revealed a serious flaw in PAN-OS. It may let a remote attacker without a password run...
Read More
Palo Alto PAN-OS Flaw Enables Root Arbitrary Code Execution

Critical Check Point VPN flaws allow remote code execution attacks

Check Point Software has revealed and fixed two major VPN flaws, CVE-2026-85102 and CVE-2026-85103. Both have a top CVSS score...
Read More
Critical Check Point VPN flaws allow remote code execution attacks

Cisco confirms CVE-2026-20079 flaw in Secure FMC is exploited in attacks

Cisco has said that a serious security flaw CVE-2026-20079 in its Secure Firewall Management Center (FMC) software is being used...
Read More
Cisco confirms CVE-2026-20079 flaw in Secure FMC is exploited in attacks

Hackers exploit PaperCut flaws using hundreds of AI agents, compromising 440 servers globally

A Russian-speaking hacker has used artificial intelligence like never before. They sent out hundreds of AI agents to find and...
Read More
Hackers exploit PaperCut flaws using hundreds of AI agents, compromising 440 servers globally

CISA Says Chinese Firms Extracted Billions of Tokens From Frontier AI Models

Six Chinese AI companies ran large-scale attacks on American AI models since late 2024, according to U.S. cybersecurity and intelligence...
Read More
CISA Says Chinese Firms Extracted Billions of Tokens From Frontier AI Models

Nightmare Eclipse Drops New Microsoft Defender ‘ShieldCrash’ zero-day

An unknown security expert called Nightmare Eclipse has drops a new Microsoft Defender flaw called "ShieldCrash" right after Microsoft released...
Read More
Nightmare Eclipse Drops New Microsoft Defender ‘ShieldCrash’ zero-day

cPanel Flaw Lets Hosting Accounts With Mail Privileges Execute Code as Root

cPanel has shared CVE-2026-67401, a serious SQL injection flaw in EmailTrack. This flaw could allow attackers with permission to take...
Read More
cPanel Flaw Lets Hosting Accounts With Mail Privileges Execute Code as Root

FortiSandbox, FortiOS, FortiProxy ZTNA flaws unveil, while Fortigate firewall actively exploited

An ongoing attack is focused on FortiGate firewalls. Hackers use a serious flaw to install a special Node.js remote access...
Read More
FortiSandbox, FortiOS, FortiProxy ZTNA flaws unveil, while Fortigate firewall actively exploited

The media said they were unable to contact Sparrso in this regard as the website displayed “HTTP ERROR 500” at the time of publication of the report. Experts say that “HTTP ERROR 500” can occur due to internal server problems. This can mainly be due to malicious code injection, DDoS attack, misconfiguration, data corruption or brute force attack.

In this regard, “Bangladesh Space Research and Remote Sensing Organization (SPARRSO)” information officer Rubel Kanti told , “We didn’t have any trace of such incident or any data breach issue on our site.”

ALSO READ:

15,000 Go Module Repositories on GitHub Vulnerable to Repojacking Attack

Check Also

Chrome

Google issues warning of new Chrome zero-day flaw exploited

Google has updated the Chrome browser to fix a serious security issue in the V8 …