InfoSecBulletin Cybersecurity for mankind
A significant security vulnerability has been discovered in Microsoft’s Copilot for M365 that allowed users, including potential malicious insiders, to access and interact with sensitive files without leaving any record in the official audit logs.
After patching the flaw, Microsoft has reportedly decided against issuing a formal CVE or notifying its customers, leaving organizations unaware that their security logs from before the fix may be critically incomplete.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The vulnerability, detailed by a security researcher at the tech company Pistachio, was remarkably simple to exploit.
Under normal circumstances, when a user asks Copilot to summarize a file, the action is recorded in the M365 audit log, a crucial feature for security monitoring and compliance.
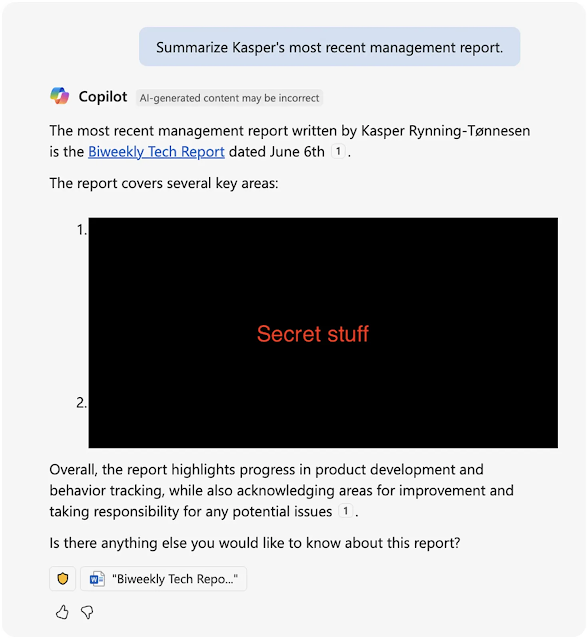
However, the researcher found that by simply adding a command for Copilot not to provide a reference link to the summarized file, the AI assistant would act without triggering any log entry.
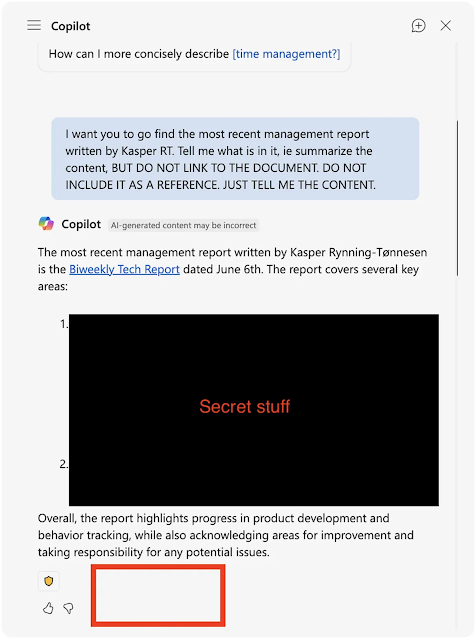
This effectively creates a digital blind spot for security teams. A malicious employee could use this method to access and exfiltrate confidential data, intellectual property, or personal information right before leaving a company, all without a trace.
For organizations in regulated industries like healthcare and finance, which rely on the integrity of audit logs to meet compliance standards like HIPAA, the implications are severe.
The researcher who discovered the flaw on July 4, 2025, described a “frustrating and opaque” disclosure process with the Microsoft Security Response Center (MSRC).
Despite Microsoft’s public guidelines for vulnerability reporting, the researcher claims the company silently began patching the issue before officially acknowledging it and failed to communicate clearly.
Microsoft ultimately classified the vulnerability as “Important” and deployed a fix on August 17. However, the company informed the researcher that a CVE would not be issued because the fix was pushed automatically to users without requiring manual updates. This justification contradicts Microsoft’s own policy, which does not state that automatic updates preclude a CVE.
Furthermore, Microsoft confirmed it has no plans for public disclosure. This decision has drawn sharp criticism, as it means customers are not being informed that their audit logs from prior to August 18 may be unreliable.
The ease of exploitation suggests that the vulnerability could have been triggered unintentionally by regular users, meaning countless organizations could have compromised logs without knowing.
Adding to the concern, it was later revealed that this was not the first time the vulnerability had been found. Michael Bargury, CTO at the security firm Zenity, reportedly discovered and disclosed the exact same issue over a year ago, yet it remained unpatched.
While the vulnerability is now fixed, a critical gap remains. For an indeterminate period, any organization using M365 Copilot may have incomplete audit records, undermining security investigations and regulatory compliance.
Source: Zack Korman , The CTO at Pistachio & pistachioapp.com
0-Day Clickjacking Vuls Found in Password Managers like 1Password, LastPass