InfoSecBulletin Cybersecurity for mankind
Around 750,000 Canadian investors were impacted in a sophisticated phishing attack revealed in August 2025. The self-regulatory organization revealed the details of the breach on January 14, 2026, following a thorough investigation that took over 9,000 hours.
Unauthorized access was due to a phishing campaign that compromised sensitive investor data held by CIRO for its regulatory duties.
Daily Cyber security update for 14.11. 2026

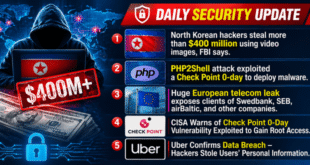
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

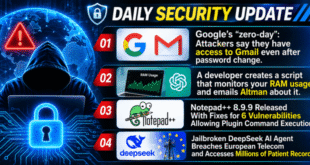
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The affected information includes birth dates, phone numbers, income, social insurance numbers, ID numbers, investment account numbers, and account statements.
CIRO stated that the organization did not gather login credentials, including passwords, security questions, or PINs, ensuring its security during the incident.
The breach impacted certain clients and former clients of CIRO dealer members. CIRO President and CEO Andrew Kriegler apologized and affirmed the organization’s commitment to helping those affected.
Response and Mitigation Measures:
CIRO quickly dealt with the incident and secured its systems. Initial findings indicated that registration data for member firms and individuals was breached, leading to immediate alerts for those affected.
CIRO is offering affected investors two years of free credit monitoring and identity theft protection from major credit agencies. Affected investors started getting letters from CIRO on January 14, 2026, containing instructions to activate protection services.