Hackers are claiming that one of China’s most strategically important computing facilities suffered a massive cyber intrusion, with more than 10 petabytes of sensitive information allegedly taken from a state-run supercomputing environment that experts suspect is the National Supercomputing Center in Tianjin. If true, this event might be one of …
Read More »
CERT-EU report
European Commission hack leaks 30 EU entities 90 GB data
The EU’s cybersecurity agency said on Thursday that a recent hack and data leak at the EU was done by a cybercriminal group called TeamPCP. In a new report, CERT-EU said that hackers exfiltrated about 92 gigabytes of data from an Amazon Web Services (AWS) account linked to the European …
Read More »Threat Actor Claims to breach Adobe: Leaking 13M Records
A bad actor named “Mr. Raccoon” claims to breach Adobe leaking 13 million support tickets with personal data, 15,000 employee records, all HackerOne bug bounty reports, and various internal documents, as stated in a report by International Cyber Digest. The threat actor said the intrusion didn’t start inside Adobe. Instead, …
Read More »ShinyHunters claim to hit Cisco: 3M Salesforce records, GitHub repos allegedly stolen
ShinyHunters claim to compromise over 3 million Salesforce records with personal data, GitHub files, AWS storage, and other compromised company information. On March 31st, ShinyHunters posted extortion demands targeting Cisco Systems. The hackers are threatening the company with “several annoying (digital) problems,” unless their demands are met by April 3rd. “A …
Read More »BD CIRT detected over 27,000 Nymaim/Avalanche Malware related events in BD
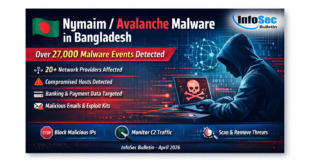
There has been a sharp rise in malware linked to the Nymaim / Avalanche loader in Bangladesh. CIRT BD observed over 27,000 malware events, which means bad actors are trying to infect systems and there is ongoing contact with the botnet. Threat Overview Nymaim (also known as Gozi ISFB Loader) …
Read More »Shwapno data breach: $1.5m ransom demand; preparing file a case
Shwapno said that hackers got into its customer database and want a ransom of $1.5 million, which is over Tk 18.3 crore. The news came out after customer names, phone numbers, and buying histories started appearing on social media. Sabbir Hasan Nasir, the managing director of Shwapno, said hackers took …
Read More »OAuth Device Code Phishing Hits 340+ Microsoft 365 Orgs
Cybersecurity experts are highlighting an ongoing phishing effort that is aiming at Microsoft 365 accounts in over 340 organizations in the U.S., Canada, Australia, New Zealand, and Germany. The event, according to Huntress, was first seen on February 19, 2026. After that, more cases appeared quickly. This campaign uses Cloudflare …
Read More »
270M iPhones Vulnerable to ‘DarkSword’ Exploit
270m iPhones Vulnerable to ‘DarkSword’ Exploit: Hack code now on GitHub
The iPhone is said as one of the safest smartphones now, but like Android phones, it has been attacked by hackers who use various flaws. Last week, a cybersecurity expert found a hacking scheme aimed at iPhone users using a tool named DarkSword. Now, someone has uploaded a new version of …
Read More »
ALERT
BGD CIRT warn of Botnet, APT, RAT and Malware attack during holidays
Bangladesh is preparing for a nationwide Eid holiday; on the contrary a different kind of “celebration” is occurring in the dark corners of the web. While most professionals are logging off for a well-deserved break, automated scripts are just getting started, scanning for “digital silence.” According to cyber security alert …
Read More »Google Alert Zero-Day For 3.5 billion Chrome Users: Forbes
Google has released a second Chrome security update just 48 hours after the first, confirming two zero-day vulnerabilities that are being actively exploited. Google has issued an urgent security update for two zero-day vulnerabilities, CVE-2026-3909 and CVE-2026-3910. Google Confirms CVE-2026-3909 And CVE-2026-3910 are already being exploited. Although full access to the …
Read More »
InfoSecBulletin Cybersecurity for mankind