The Qilin ransomware group is exploiting a flaw in PAN-OS GlobalProtect to break into victims’ networks, says the cybersecurity firm Arctic Wolf. Palo Alto Networks fixed the flaw (CVE-2026-0257) on May 13 and warned that hackers started using it to break into company networks. Rapid7 reported seeing this attack on many …
Read More »
CVE-2026-60137, CVE-2026-63030
Patch immediately! 2 high severity WordPress flaws found
The WordPress security team received reports about these flaws: CVE-2026-60137 : A facilitated SQL injection issue reported as a team by TF1T, dtro, and haongo CVE-2026-63030 : A REST API batch-route confusion and SQL injection issue leading to Remote Code Execution reported by Adam Kues at Assetnote / Searchlight Cyber …
Read More »Windows LegacyHive 0, AWS, Fortinet, TP-LINK multiple flaws got hackers attention
A Windows security flaw called LegacyHive (MSNightmare) misuses the User Profile Service. This allows local users to gain higher privileges, change admin accounts, and run code with admin rights. The public proof‑of‑concept (PoC) from the MSNightmare GitHub account describes the bug as a “Windows user profile service arbitrary hive load …
Read More »
CVE-2026-53412
Zoom Warns of critical account takeover Flaw via Network Access
Zoom has issued updates for a flaw in the Windows desktop client, known as CVE-2026-53412. This issue may allow an unauthenticated user to conduct an account takeover via network access. This flaw arises from improper input validation and may enable unauthenticated attackers to execute account takeover attacks via network access. …
Read More »Microsoft Patch Tuesday July-2026 fixes 570 flaws, 3 zero-days
Microsoft’s Patch Tuesday in July 2026 fixes around 570 security flaws in its products. This comes after June’s big update, which had a record 206 issues and three that were already known to the public. This big update comes after Microsoft’s recent change to use artificial intelligence for finding security …
Read More »CISA warns Cisco IOS flaw, while VMware flaw allows bypassing authentication
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has warned that hackers are using CVE-2008-4128, a CSRF flaw in Cisco IOS versions 12.4(12) and 12.4(4). This weakness was included in CISA’s Known Exploited Vulnerabilities Catalog on July 13, 2026, showing that old networking flaws can still be security threats long …
Read More »Palo Alto Networks Addresses 13 Vulnerabilities
Palo Alto Networks shared warnings on Wednesday about over twelve security issues in its products. The new warnings include 13 security problems for Palo Alto Networks products and over 500 issues that Google recently fixed in Chromium, which is used for the Prisma browser. The worst of the new fixes is …
Read More »Critical GCP Dialogflow Vulnerability Allows Malicious Code Injection
A critical flaw in Google Cloud Platform’s Dialogflow CX lets attackers add harmful code to a company’s AI chatbot system. The flaw, called “Rogue Agent,” was revealed by Varonis Threat Labs. It could secretly steal conversations and allow big phishing attacks, needing just one edit permission to start. GCP Dialogflow …
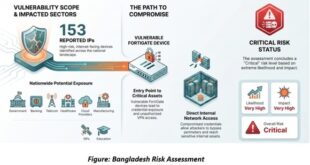
Read More »CIRT identified 153 publicly exposed FortiGate devices in Bangladesh
CIRT identified 153 publicly exposed FortiGate devices in Bangladesh. In an advisory CIRT said, the campaign has been observed globally, affecting organizations across 194 countries. The systems have the “fortibleed” label, meaning they might be at risk for losing login details and being accessed without permission due to issues with …
Read More »CERT/CC Alerts to Hidden Admin Backdoor in Tenda Router Firmware
Several Tenda firmware versions have a hidden backdoor that lets people gain admin access to the device’s web interface. An attacker can use this flaw, known as CVE-2026-11405, to skip the password check and take full control without proper login details, the CERT Coordination Center (CERT/CC) reported on Monday. “An …
Read More »
InfoSecBulletin Cybersecurity for mankind