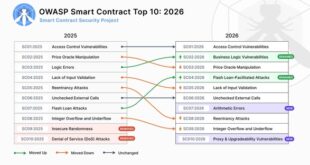
OWASP has released the Smart Contract Top 10: 2026, a guide to help Web3 developers, security auditors, and protocol owners identify critical vulnerabilities in smart contracts. This edition, part of the OWASP Smart Contract Security initiative, uses security incidents and survey data from 2025 to identify the most impactful risks …
Read More »ALERT
Microsoft admits
Copilot reads ‘confidential emails’ bypassing DLP policies
Microsoft has admitted that a coding bug accidentally allowed Copilot Chat to access and summarize confidential emails. Microsoft said that a bug in Microsoft 365 Copilot allowed the AI assistant to access private emails, raising serious privacy issues for companies using the service. Bleeping Computer reports, the flaw bypasses data loss …
Read More »
ALERT
Without bank card, account “Ploutus” malware drains U.S. ATMs
A 19 February 2026 FBI FLASH (FLASH-20260219-001) alerts banks and ATM operators about an increase in “jackpotting,” where criminals use malware to steal cash from machines without actual transactions, becoming a widespread issue in the U.S. The alert focuses on Ploutus, an ATM-targeting malware family that abuses eXtensions for Financial …
Read More »CISA warns feds to fix Dell flaw within 3 days
CISA has ordered government agencies to fix a serious Dell flaw within three days, which has been actively exploited since mid-2024. Mandiant and the Google Threat Intelligence Group report that a vulnerability (CVE-2026-22769) involving hardcoded credentials in Dell’s RecoverPoint is being exploited by a suspected Chinese hacking group named UNC6201. …
Read More »
Critical Alert
Chrome Zero-Day (CVE-2026-2441) Exploited in the Wild
Google released an urgent security update for Chrome to address a high-severity zero-day vulnerability being actively exploited. This flaw, known as CVE-2026-2441, affects the browser’s CSS component and could let attackers run harmful code on a victim’s machine through a compromised webpage. Attackers can use a “dangling pointer” to insert …
Read More »
ALERT
Vulnerability in Palo Alto’s ADNS allow attacker reboot firewall leading maintenance mode
Palo Alto Networks released a security advisory about a DoS vulnerability in its PAN-OS software, particularly in the Advanced DNS Security feature. The vulnerability, identified as CVE-2026-0229, has a CVSSv4 score of 6.6 and may allow unauthenticated attackers to cause firewalls to restart repeatedly, leading to maintenance mode. The vulnerability …
Read More »CISA Flags Microsoft Configuration Manager SQL Injection flaw Exploited in Attacks
CISA warned U.S. government agencies on Thursday to protect their systems from a critical Microsoft Configuration Manager vulnerability that was fixed in October 2024 and is currently being exploited. Microsoft Configuration Manager is a tool for IT management of many Windows servers and workstations. CVE-2024-43468 is an SQL injection vulnerability discovered …
Read More »Zimbra Patches for XSS, XXE, & LDAP Vulnerabilities
Zimbra launched version 10.1.16 addressing serious vulnerabilities like cross-site scripting (XSS), XML external entity (XXE), and LDAP injection. This urgent update, marked as high risk for patch severity and deployment, requires admins to upgrade right away to protect against exploits. Attackers can use unsanitized inputs to insert harmful scripts, which …
Read More »Apple released Patches iOS Zero-Day (CVE-2026-20700) Exploited in wild
Apple has released an urgent security update for all its mobile devices to fix a serious zero-day vulnerability being exploited in a targeted attack describes as an “extremely sophisticated attack” against specific individuals. CVE-2026-20700 is a serious vulnerability that prompted Apple to release iOS 26.3 and iPadOS 26.3 to protect …
Read More »Microsoft fixes 6 zero-days, 58 flaws in February 2026 Patch Tuesday
Today is Microsoft’s February 2026 Patch Tuesday, featuring security updates for 58 flaws, including 6 that are actively exploited and 3 publicly disclosed zero-day vulnerabilities. This Patch Tuesday fixes five “Critical” vulnerabilities: three elevate privileges and two disclose information. The details of vulnerabilities by category are as follows: 25 Elevation …
Read More »
InfoSecBulletin Cybersecurity for mankind