 InfoSecBulletin Cybersecurity for mankind
QNAP has urgently advised users and released patches for seven zero-day vulnerabilities exploited during the Pwn2Own Ireland 2025 competition, affecting their NAS devices. These patches address critical flaws in the core operating systems and key applications, such as backup and malware removal tools.
Top security research teams, including Summoning Team, DEVCORE, Team DDOS, and a CyCraft intern, showcased their successful exploits at Pwn2Own.
CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

The vulnerabilities in the QNAP system pose a serious risk to user data on NAS devices. Patches have been released for the main operating systems, QTS and QuTS hero, along with key applications.
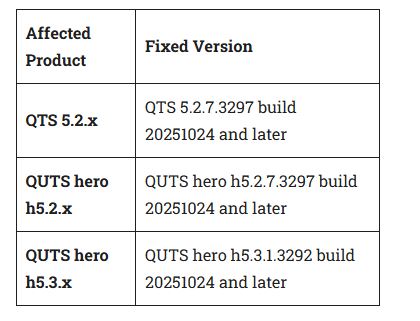
1. Core Operating Systems: QTS and QuTS hero
Multiple vulnerabilities (CVE-2025-62847, CVE-2025-62848, CVE-2025-62849) in QNAP’s operating systems were discovered. Although official CVSS scores are not listed, the zero-day status and context of a Pwn2Own exploit indicate a High Risk for remote code execution and data compromise.
2. Backup and Data Protection Apps
Two major applications designed to safeguard data were found to be vulnerable:
HBS 3 Hybrid Backup Sync (CVE-2025-62840, CVE-2025-62842) has multiple critical vulnerabilities that were fixed. As this tool manages backup routines, attackers could potentially access historical data and remote backups if it is compromised. Users on versions 26.1.x and earlier should update to HBS 3 version 26.2.0.938 or later.
Hyper Data Protector (CVE-2025-59389): A vulnerability in this dedicated data protection tool was fixed in version 2.2.4.1 and later.
3.Malware Remover (CVE-2025-11837)
A zero-day vulnerability was even found in QNAP’s security tool, Malware Remover. Users on versions 6.6.x must update to Malware Remover 6.6.8.20251023 and later.
The vulnerabilities were demonstrated to be exploitable in a lab setting, meaning attackers can easily use these methods in real-world scenarios. Since NAS devices store valuable data, QNAP users should update their firmware and applications right away.



