The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has listed two flaws in PaperCut NG and PaperCut MF in its Known Exploited Vulnerabilities (KEV) Catalog. They warn that hackers are using these flaws in real attacks. The flaws with PaperCut, known as CVE-2026-81578 and CVE-2026-82078, can be linked together. This …
Read More »Fire Ant hackers convert Cisco routers into spy platforms
The researchers discovered Fire Ant’s new tactic after finding an active GRE (Generic Routing Encapsulation) tunnel interface on a Cisco IOS XR router that could not be explained by a running configuration or commit history. According to incident response company Sygnia, The threat actor moved from attacking VMware hypervisors to breaking …
Read More »Five Critical WordPress Flaws Lead to Site Takeover or RCE
Many serious security flaws have been found in WordPress plugins and themes, such as WPMU DEV Dashboard, Avada, TranslatePress, Pods, and GiveWP. These issues could let hackers bypass login, take over accounts, and run any code. The vulnerabilities, according to Wordfence and Patchstack, are listed below: CVE-2026-76581 (CVSS score: 9.8): …
Read More »ServiceNow warns of three critical security vulnerabilities
ServiceNow issued security updates for three new serious AI Platform problems that can be used in code injection, SQL injection, and privilege escalation attacks. The ServiceNow AI Platform, which was once called the Now Platform, is a strong Platform-as-a-Service (PaaS). It helps add AI to important business tasks and supports …
Read More »270+ Zimbra servers compromised in continuous attacks
Threat actors have already compromised more than 270 Zimbra instances in attacks that let them run code remotely. These attacks focus on a serious flaw in the Zimbra Collaboration Suite (ZCS). Synacor fixed the security flaw (called CVE-2026-73570). This flaw lets attackers run code from far away by using a …
Read More »
Chameleon SEO Poisoning
Hackers poison Bing and Google search results to deliver phishing banking pages
Bank customers looking for a login page can now fall into a trap before getting a strange email or text. Hackers are changing Google and Bing results so fake banking pages show up where people think they will find real services. The Chameleon SEO Poisoning campaign turns regular searches for …
Read More »Five new malware families actively targeting Asian Gov.t infra
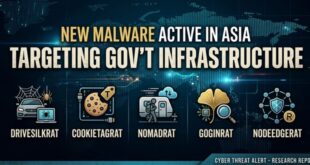
Central Asian government agencies have been attacked in a cyber spy operation that used a small but different range of remote access tools. The action called SilkParasite used fake government documents and trusted Windows programs to secretly install malware on victims’ computers. The campaign seems to be aimed at intelligence gathering …
Read More »Splunk, Zyxel Patch Multiple Flaws Enabling RCE and Root Command Execution
Splunk has issued security fixes for 17 weaknesses in different apps and add-ons, such as Splunk MCP Server, Splunk AI Toolkit, and Splunk Connect for Kafka. The biggest flaw, listed as CVE-2026-76404, is a serious flaw that allows remote code execution. It has a CVSS score of 9.1. The notice …
Read More »Oracle Issues 943 Security Patches, Including Critical WebLogic Flaw
Oracle has put out 943 new security updates in its August 2026 Critical Security Patch Update. These updates fix problems in its business software. The update contains important Oracle WebLogic Server problems. These issues can let a remote attacker, who is not logged in, gain full control of the affected servers. …
Read More »Apple Patches 28 Security Flaws in macOS, iOS, and iPadOS
Apple has put out security updates for macOS, iOS, and iPadOS. These updates fix 28 problems that could let users lose data, crash apps, access kernel memory, and run unwanted code. The updates came out on August 17, 2026. They have macOS Tahoe 26.6.2, iOS 26.6.1, iPadOS 26.6.1, iOS 18.7.10, and …
Read More »
InfoSecBulletin Cybersecurity for mankind