 InfoSecBulletin Cybersecurity for mankind
AWS announced new security features at its re:Inforce conference, such as identity and malware protection services. The cloud giant added passkeys to the list of supported multi-factor authentication (MFA) mechanisms for root and Identity and Access Management (IAM) users.
The company also started enforcing MFA on root users, particularly AWS Organization management account users.
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

“You can use the built-in authenticators in your phones and laptops to unlock a cryptographically secured credential to your AWS sign-in experience,” AWS said. “And when using a cloud service to store the passkey (such as iCloud keychain, Google accounts, or 1Password), the passkey can be accessed from any of your devices connected to your passkey provider account. This helps you to recover your passkey in the unfortunate case of losing a device.”
IAM Access Analyzer now has custom policy checks to detect policies that allow access to important AWS resources or grant public access. AWS has also introduced guided revocation in IAM Access Analyzer. This feature helps users by providing guidance on how to revoke unnecessary permissions that grant access.
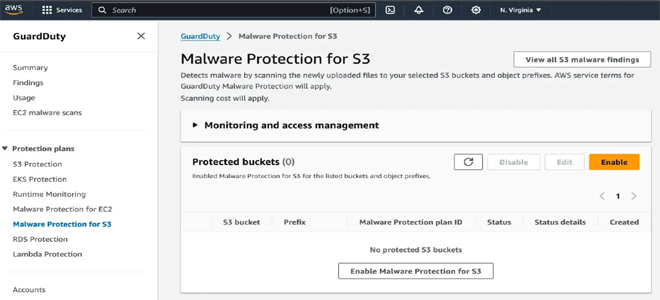
AWS announced that Amazon GuardDuty Malware Protection is now available for the Amazon S3 service. This feature allows users to detect malicious files in S3 buckets. Previously, GuardDuty Malware Protection only provided agentless scanning on Amazon EBS volumes attached to EC2 and container workloads.
The company introduced a new feature in AWS CloudTrail Lake. This feature uses gen-AI to help customers analyze CloudTrail logs for compliance, security, and operational needs.



