Sunday , November 15 2026
rat

APT36 to attack Windows Systems Absuing Google Drive & Slack

ElizaRAT is malware that mainly targets Windows systems and acts as a remote access tool (RAT), allowing attackers to access infected devices without permission. This malware is often distributed through phishing campaigns or malicious downloads.

CheckPoint researchers found that APT36 (aka “Transparent Tribe”) is a Pakistan-based APT group, hackers are targeting high-profile Windows users with ElizaRAT.

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

ElizaRAT was initially identified in 2023, and since then, it has evolved significantly by incorporating advanced features.The infection chain of ElizaRAT begins with “phishing emails” containing malicious “CPL” files distributed via “Google Storage links.”

It establishes persistence by creating a “unique victim ID,” “setting up working directories in %appdata%,” and deploying secondary payloads like “ApoloStealer.”
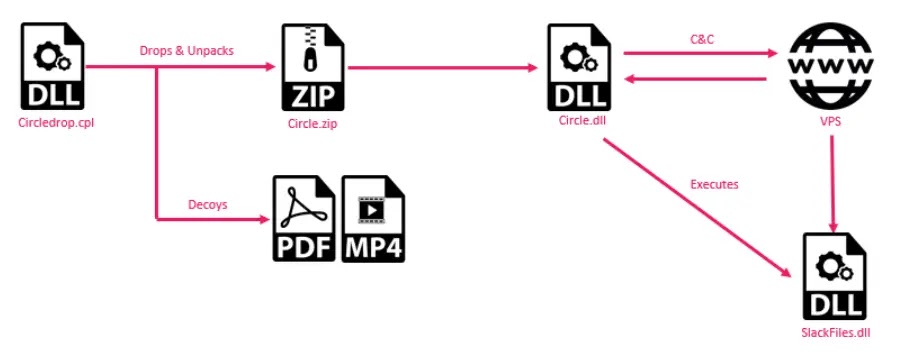
      Infection Chain (Source – CheckPoint)

The Checkpoint report states that this stealer component targets sensitive file types (“.doc,” “.pdf,” “.ppt,” “.xls”) and performs “systematic data exfiltration” via encrypted channels.

The malware employs sophisticated evasion techniques like:-

Time zone verification checks for India Standard Time.
Maintains reliability via various C2 communication methods.
Ranging from Slack API calls to Google Cloud Storage service account authentication using X.509 certificates.
Each campaign variant illustrates increasingly sophisticated capabilities while maintaining the core objective of persistent data theft from targeted “Indian institutions.” ‘ConnectX’ is a USB-targeting malware component within the ElizaRAT ecosystem.

click here to read full report.

Check Also

ARTEX

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Hackers used ARTEX, a free tool for testing security with AI, to attack over 200 …