InfoSecBulletin Cybersecurity for mankind
A cybersecurity incident with Spanish travel tech company Amadeus IT Group has worried the global airline industry. Hackers got into its booking systems and accessed passenger information linked to several international airlines.
Airlines like Cathay Pacific, Japan Airlines, Qantas, Malaysia Airlines, Korean Air, and Asiana Airlines have said they are affected or looking into possible exposure after the incident. All Nippon Airways (ANA) has also stated that customer booking details may have been accessed.
Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

Multiple European supermarket fridges got hacked: Temperatures reached high as 55°C

Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks

Daily Cyber security update for 31.10. 2026

NetamLoader malware to attack Win10: Customized for Gov.t in Asia
‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text
NIST Unveiled Guidance for Post-Quantum Cryptography Transition
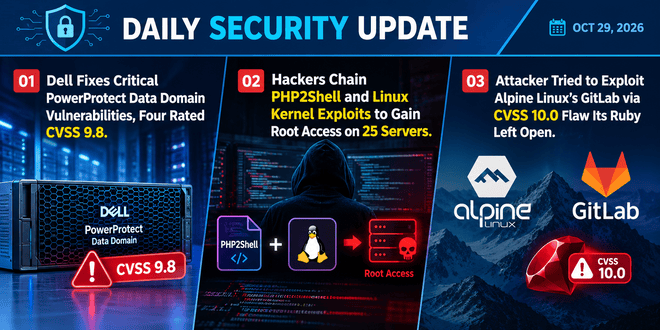
Daily Cyber security update for 29.10. 2026
Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries
CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace
According to airline disclosures, the unauthorized access involved reservation data processed through Amadeus systems between August 2023 and September 2026. The incident concerns a third-party technology provider rather than a confirmed compromise of the airlines’ own internal IT infrastructure.
What Information Was Exposed?
The information potentially accessed varies by airline and passenger record. It may include:
Passenger names and booking reference numbers (PNRs).
Flight dates, routes and travel details.
Email addresses and telephone numbers.
Passport numbers and nationality.
Frequent flyer membership numbers.
Ticket and seat information.
The amount of affected bookings varies by airline. Cathay Pacific said about 53,000 bookings were affected, while Japan Airlines reported around 92,000 affected customers. ANA said about 37,800 customers might be affected.
The airlines said there is no proof that anyone accessed credit card or payment info in the reported cases.
Airlines and Reported Impact
| Airline | Reported information |
|---|---|
| Cathay Pacific | Approximately 53,000 bookings affected. |
| Japan Airlines (JAL) | Approximately 92,000 customers affected. |
| All Nippon Airways (ANA) | Approximately 37,800 customers potentially affected. |
| Korean Air | Unauthorized access to reservation information confirmed. |
| Asiana Airlines | Reservation-related information accessed. |
| Malaysia Airlines | Potential exposure of customer information; exact number not disclosed. |
| Qantas | Amadeus confirmed unauthorized access; Qantas is investigating whether its bookings were affected. |
Sources: Airline statements and reporting by Reuters, CNA and other news organizations
Investigation and Security Response
Amadeus reportedly took steps to fix the problem, like changing passwords and improving their system checks and alerts. The airlines involved have started looking into the issue and taking safety steps. Japan Airlines and Cathay Pacific said their flights were not impacted.
Malaysia Airlines said that its IT systems were safe. Qantas also confirmed that its systems and databases are secure. They have informed Australia’s cybersecurity authorities and are working with Amadeus to check if any Qantas booking information was impacted.
No airline has reported any signs that financial information has been accessed. However, the release of passenger names, booking references, and travel details may lead to targeted scams, social engineering, and travel fraud.
Customers should be careful of unexpected emails, calls, and messages asking for personal info, payment details, or travel document info.
The event shows the cybersecurity dangers that come with using outside technology providers in the global airline industry. Even if airlines have secure systems, a breach in an external reservation platform can reveal private passenger data across different companies. The inquiry is still happening, and we do not yet know how many airlines and customer records are involved.
Related News:
Korean Air thousands of employees’ personal info leaked
Air Canada admits hack of employee data
Again! Two big airlines disclosed data breaches