
Tuesday , November 10 2026

Checkmarx blog post
170K+ Python Developers GitHub Accounts Hacked

The Checkmarx Research team found out that hackers attacked the software supply chain and managed to breach the Top.gg GitHub organization, which has over 170,000 users, and also targeted individual developers.
These hackers took over accounts by stealing browser cookies, added bad code with verified commits, created a fake Python mirror, and uploaded harmful packages to the PyPi registry. This blog will discuss the attack and how the hackers did it.

This malicious campaign is based on an attacker combining various techniques to quietly attack the software supply chain, especially targeting the Python ecosystem. The campaign cleverly spread a harmful dependency through a fake Python infrastructure, linking it to well-known GitHub projects and official Python packages.
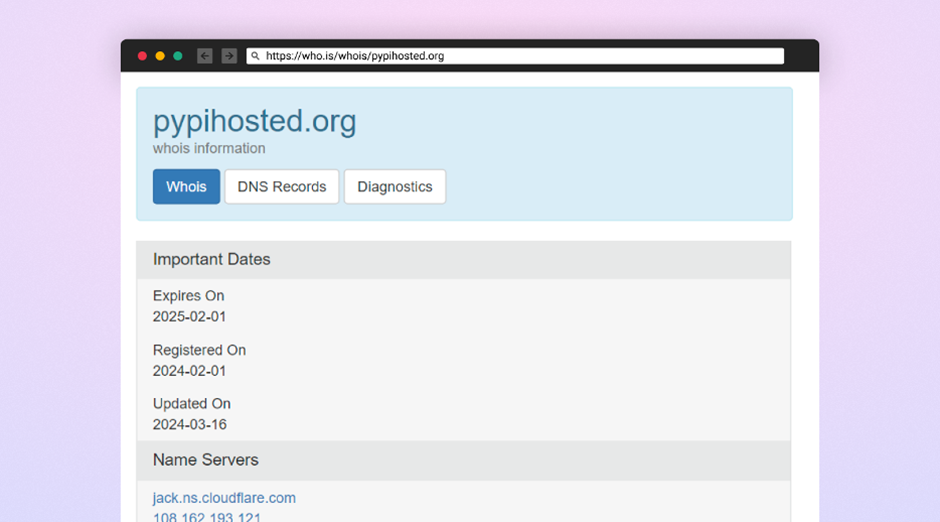
            Python mirror -files.pythonhosted.org

Mohammed Dief, a Python developer and victim of the campaign, provided a disturbing account of the attack’s stealth and impact. Dief saw a strange error on his laptop, which was the first clue that his computer was hacked.

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 million) in a cyber heist...
Read More
Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

OpenAI says that an automated system found and confirmed 948 different Linux kernel security issues in one run. These flaws...
Read More
OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

Apple credits Md Rasel Bhuyan and fellow researcher Musaab Khan for discovering an out-of-bounds write vulnerability affecting multiple Apple operating...
Read More
Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

Among the notable victims of this campaign is the Top.gg GitHub organization, a community boasting over 170,000 members.

Attackers took over GitHub accounts with high reputations, including “editor-syntax,” who had write permissions to Top.gg’s repositories.

They carried out harmful actions and made their harmful repositories more visible and credible, affecting both individual developers and entire communities.
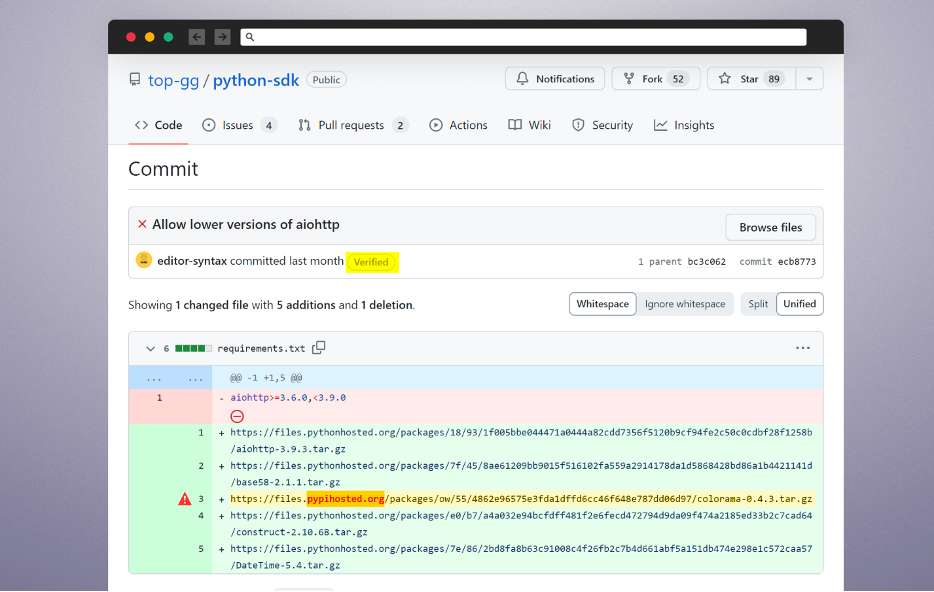
Software supply chains are at risk of advanced attacks, including social engineering, account hijacking, and harmful software being uploaded to the PyPi registry. The campaign appears to have successfully exploited multiple victims. To read out the full article click here.


Check Also

973 flaws

Microsoft Patch Tuesday September 2026 Fixed 973 Flaws Fixed, 2 Zero-Days

Microsoft shared its September 2026 security updates on September 8. These updates fix 973 flaws, …

