 InfoSecBulletin Cybersecurity for mankind
“A critical vulnerability has been identified in the Google Authentication mechanism of the application. By manipulating the ID and email parameters in the authentication request, an attacker can obtain an access token for any user. This allows the attacker to take over any account without any user interaction, leading to a complete compromise of the victim’s account.”
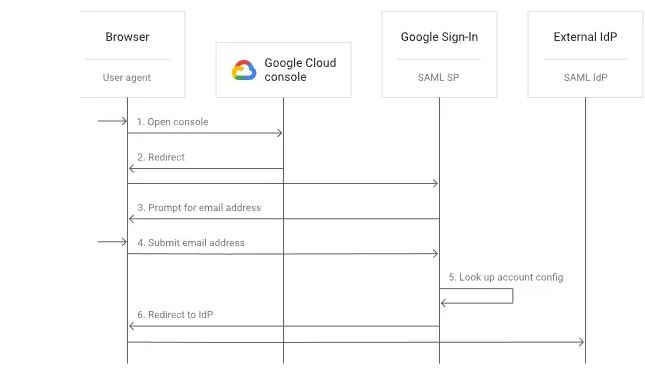
What is the Single Sign-On (SSO):
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Using Single Sign-On (SSO) with Google Cloud is a smart choice for organizations. It improves security and makes user authentication easier. SSO centralizes authentication through a trusted Identity Provider (IdP), reducing risks. It also makes it easier for IT teams to manage user access and enforce security policies, including multi-factor authentication (MFA).
To transition smoothly to SSO, organizations should follow these steps: select a compatible IdP, configure settings, and thoroughly test the setup. SSO offers several benefits: improved security, better user experience, simplified administration, and compliance with regulatory standards.
Proof of Concept (PoC):
1-Login with Google:
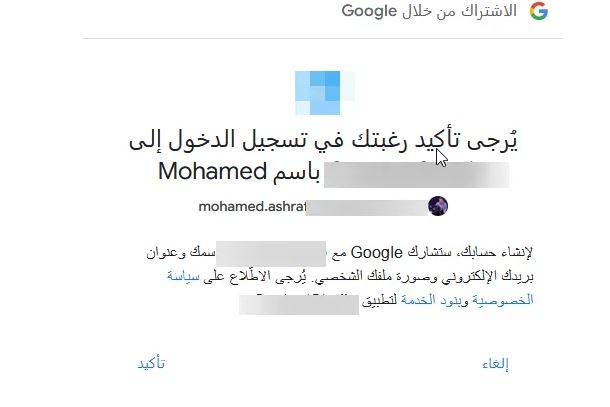
2-Intercept the OAuth Request:
3-Modify the Request:
Change the id field to any ID.
NOTE In changing the ID, you can try any number because it does not verify whether this number is correct or not, but it verifies whether the ID existed before or not, so you can enter anything, for example
“id”:”1″ or “id”:”123456”…. etc
Change the email field to the victim’s email address.
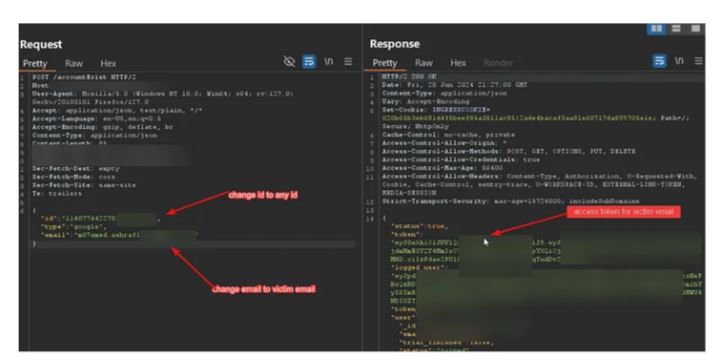
4- now Gain Access to Victim’s Account:
Conclusion
This situation shows how a vulnerability can be used to take over accounts without any action from the user. It is important to fix this problem quickly to protect user data and the reputation of Example.com.
This article is first published in medium.com written by Elcapitano. He can be reach on X Elcapitano.



