InfoSecBulletin Cybersecurity for mankind
Security researchers were able to bypass authentication on three popular laptops by testing the fingerprint sensors used for Windows Hello. The research was done by Blackwing Intelligence and Microsoft’s MORSE.
Target devices include a Dell Inspiron 15 with a Goodix fingerprint sensor, a Lenovo ThinkPad T14s with a Synaptics sensor, and a Microsoft Surface Pro X with an ELAN sensor. The embedded fingerprint sensors and the host were targeted with software and hardware attacks.
Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks

Daily Cyber security update for 31.10. 2026

NetamLoader malware to attack Win10: Customized for Gov.t in Asia
‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text
NIST Unveiled Guidance for Post-Quantum Cryptography Transition
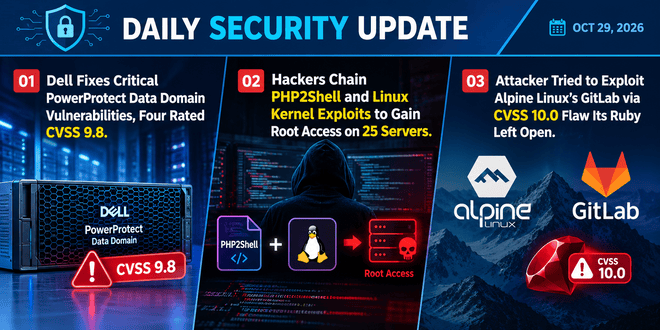
Daily Cyber security update for 29.10. 2026
Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries
CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace
Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE
CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw
AlSO READ:
By 2025, Domestic cloud market expected $46.3 million; MD “DataHub Asia”
The sensors that were tested are Match-on-Chip, meaning the chip has a microprocessor and memory, and the fingerprint data always stays within the sensor. To bypass authentication, one would need to physically attack the chip itself.
To carry out the attack, the attacker needs to physically get hold of the device. This means they would have to either steal the device or use the evil maid method.
The researchers showed how to carry out attacks by connecting a hacking device to a laptop using USB or by connecting a specially crafted rig to the fingerprint sensor.
For Dell and Lenovo laptops, the Windows Hello fingerprint authentication was bypassed by manipulating valid user fingerprint ID numbers and enrolling the attacker’s fingerprint by imitating a legitimate user’s ID.
To hack the Surface device, the attacker must disconnect the Type Cover, which is the keyboard and fingerprint sensor, and connect a USB device that tricks the fingerprint sensor into thinking it’s an authorized user logging in.
Blackwing published a blog post on Tuesday about their findings. Microsoft also released a video of the Blackwing researchers presenting their findings at the BlueHat conference in October.