 InfoSecBulletin Cybersecurity for mankind
Bangladesh Government’s Computer Incident Response Team (BGD e-GOV CIRT) proactively releases critical threat intelligence information to ensure the security of Bangladesh’s cyberspace. Following this, CIRT has recently identified critical vulnerabilities for critical information infrastructure (CII).
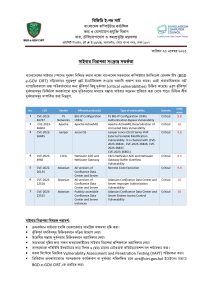
CIRT published cyber alert for critical information infrastructure (CII) on Thursday (23 November). The report includes the CVE of the f5, Apache, Juniper, Citrix and Atlassian ranging score from 9.8 to 10.
Citrix NetScaler SAML 0-Day Flaw Under Attack

Major Danish university breached, 200,000 users at risk

Microsoft’s X account hijacked to promote Clippy crypto scam

Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

The vulnerabilities identified include F5 BIG-IP Configuration Utility Authentication Bypass, Apache ActiveMQ Deserialization of Untrusted Data, Juniper Junos OS EX Series PHP External Variable Modification, Citrix NetScaler ADC and NetScaler Gateway Buffer Overflow, Remote Code Execution, Atlassian Confluence Data Center and Server Improper Authorization, and Atlassian Confluence Data Center and Server Broken Access Control.
The detail information are as follow:
 In cyber security advice, CIRT said, to prevent increasing cyber attacks, increasing overall efficiency, taking initiatives to identify vulnerable threats, identifying causes of vulnerability and taking measures, training on cyber security, monitoring network communication logs of last six months and conducting VAPT.
To see the full report click here.



