Wednesday , November 11 2026
Artica Proxy

Unpatched PHP Deserialization Vulnerability in Artica Proxy

SonicWall Capture Labs found a vulnerability with the Artica Proxy appliance. This vulnerability affects over 100K servers globally. Artica Proxy is a proxy solution that performs tasks like web filtering, SSL inspection, and bandwidth management. SonicWall has developed measures to mitigate the vulnerability.

There is a security vulnerability called CVE-2024-2054 in the administrative web interface. It allows users to execute code without authentication, which can lead to the execution of code under the “www-data” user account. The severity score is 9.8. This affects version 4.50 and earlier versions. Although there are currently no reports of active attacks, there is a publicly available proof of concept provided by the Korelogic research team.

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 million) in a cyber heist...
Read More
Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

The vendor has not released a patch yet. Organizations are strongly advised to follow the steps in the mitigation section below. SonicWall customers are already protected with IPS signature 19786, released on March 18th.

Technical Overview:

An unauthenticated user can send an HTTP POST request to the “/wizard/wiz.wizard.progress.php” endpoint with the “build-js” query parameter.
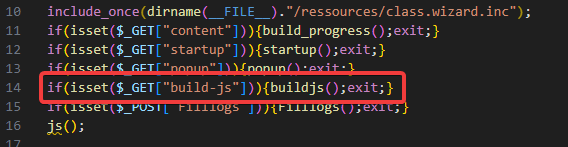
             Figure 1: wiz.wizard.progress.php lines 10-16

During the “build-js” user input processing, it decodes the base64 value and sends it to the “unserialize” PHP function. This is depicted in Figure 2.
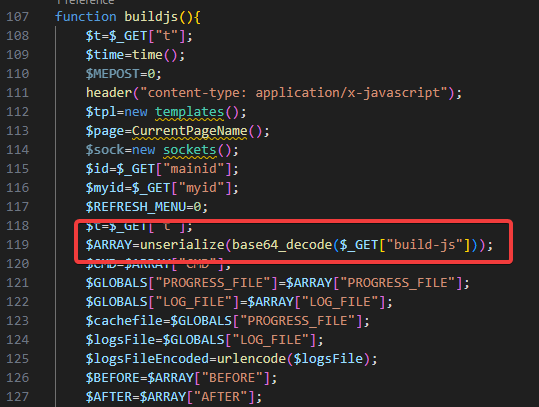
          Figure 2: wiz.wizard.progress.php buld.js function


This is the root cause of the vulnerability, as an unauthenticated attacker can control the base64 encoded input which is then directly deserialized.

Triggering the Vulnerability:

To exploit this vulnerability, an attacker needs to send an HTTP POST request to the Artica Proxy instance with the manipulated “build-js” parameter set to a base64-encoded payload. The public PoC code demonstrates this using the Linux “curl” command as shown in Figure 3.
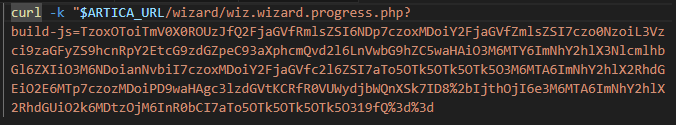
                  Figure 3: Triggering the vulnerability using curl

to read the full report click here.

 

Check Also

Dahua

14,000 Dahua cameras compromised: TP-Link flaws enable RCE

Over 14,000 Dahua security cameras connected to the internet have been hacked in a 35-day …