 InfoSecBulletin Cybersecurity for mankind
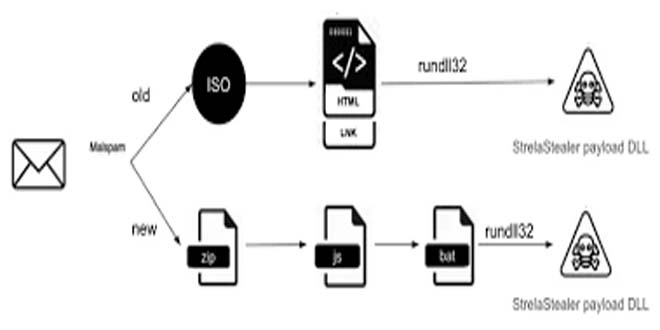
StrelaStealer malware steals email login data from popular email clients and sends it to the attacker’s server. The attacker can then use this information to launch more attacks. Since its first appearance in 2022, the threat actor has carried out many email campaigns and shows no sign of stopping.
Unit42 researchers have found a wave of big StrelaStealer campaigns affecting more than 100 organizations in the EU and U.S. These campaigns involve spam emails with attachments that activate the StrelaStealer’s DLL payload.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Attackers change email attachment file formats to evade detection. This prevents detection from previously generated signatures or patterns. The malware author frequently updates the DLL payload with improved obfuscation and anti-analysis techniques. This makes analysis more difficult for analysts and security products.
Last Large-Scale Campaign of 2023:
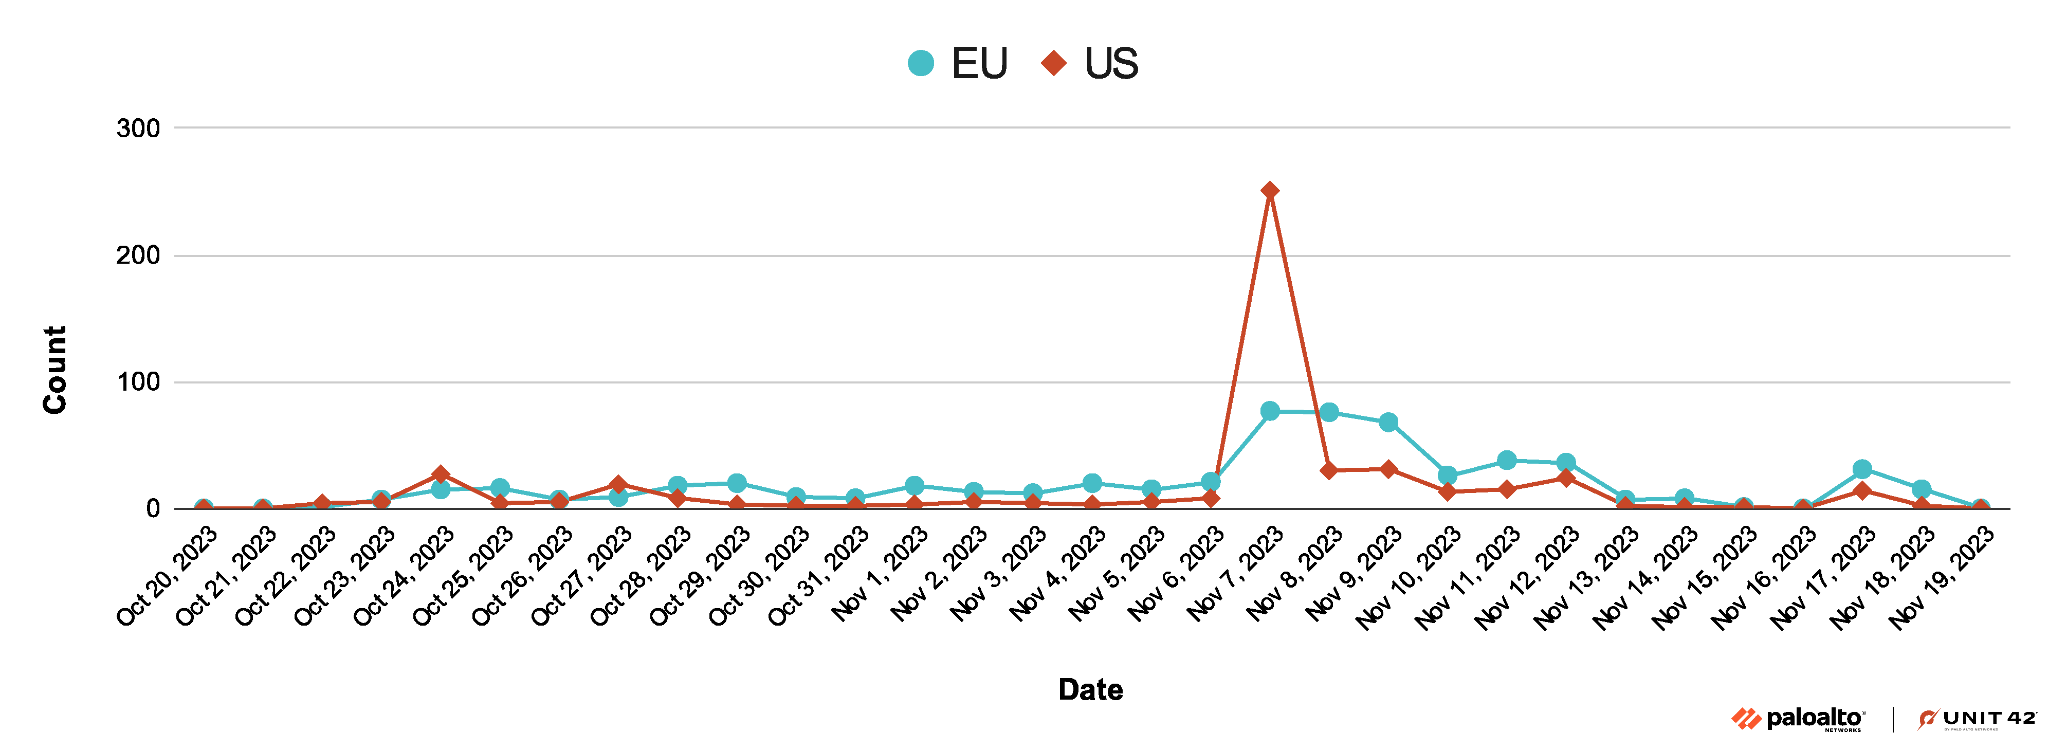
StrelaStealer has been causing multiple large-scale campaigns. The most recent campaign in November 2023 targeted organizations in the U.S. and EU. Figure 1 shows the timeline of this campaign.
Recent Large-Scale Campaign in 2024
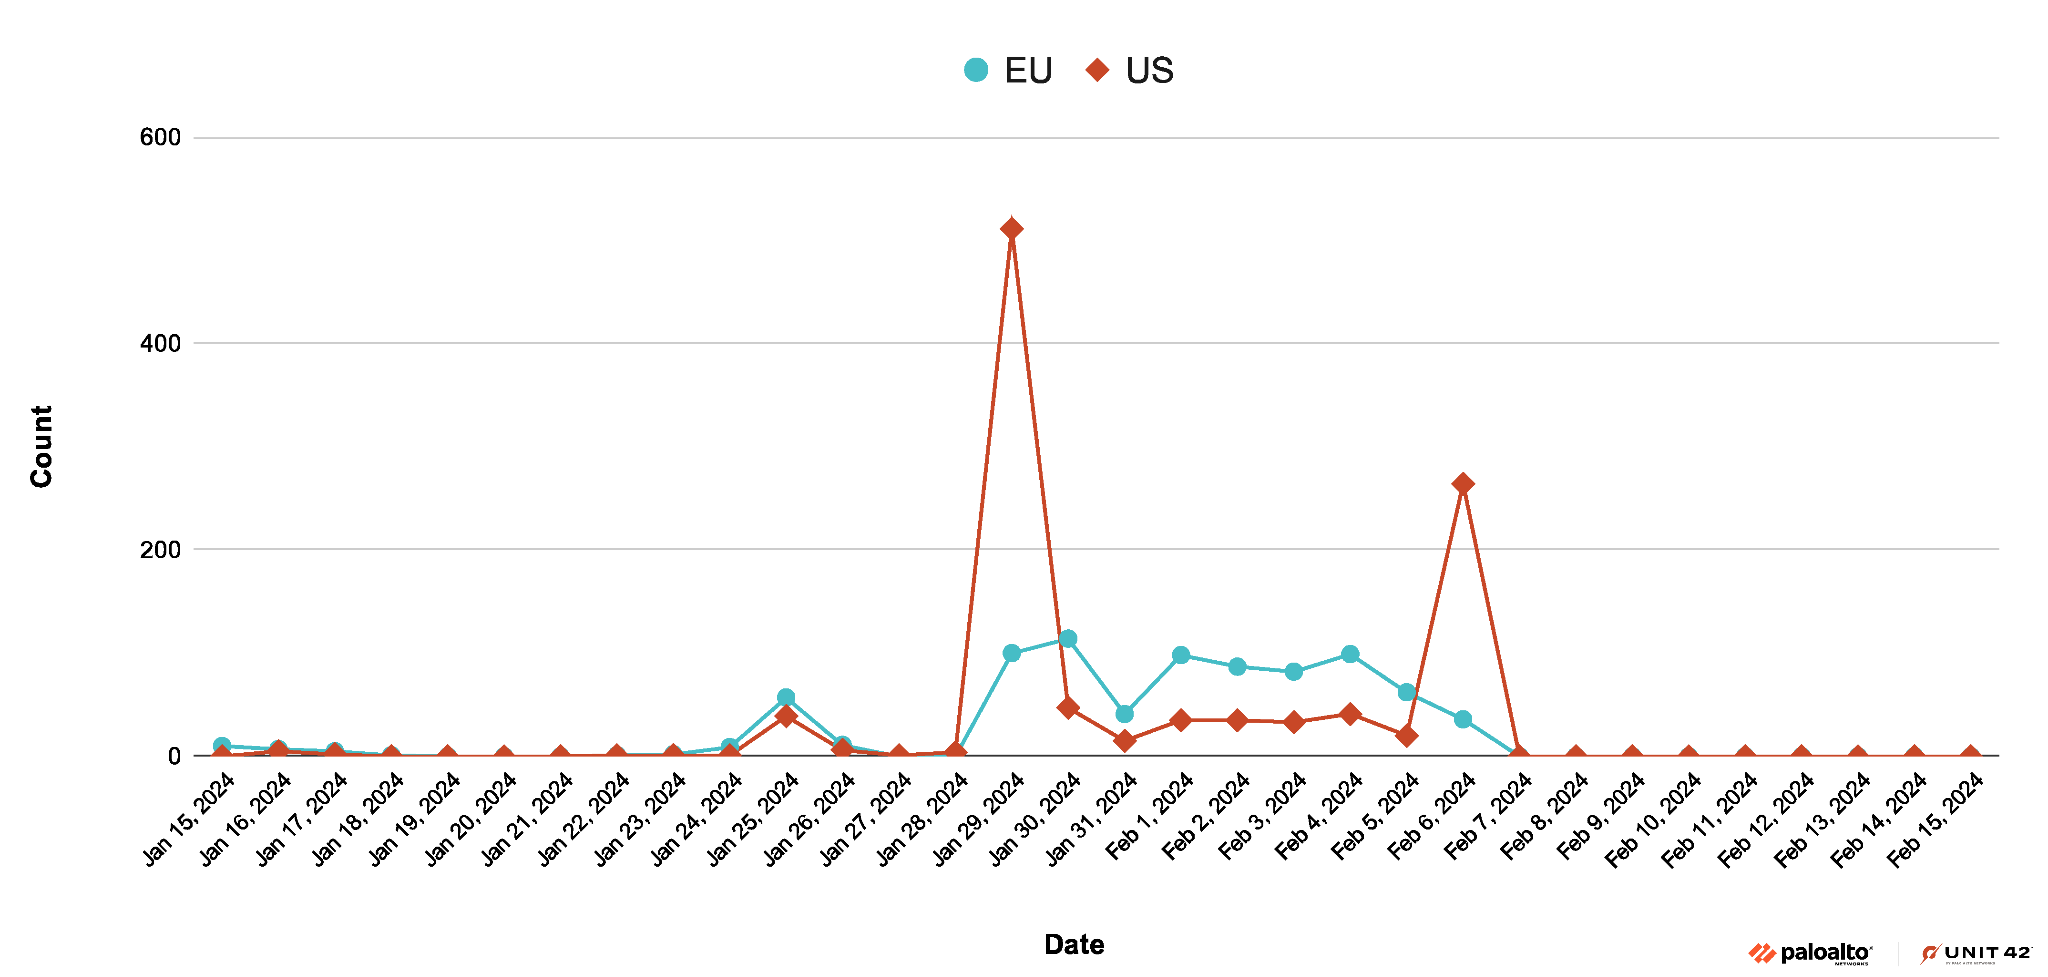
In January 2024, the StrelaStealer threat actors started a big campaign targeting organizations in the same areas as before. The campaign peaked on Jan. 29, 2024.
The language of the StrelaStealer spam email seen during this campaign is localized and the subject line has the pattern of Factura/Rechnung/invoice####. Figure 3, below, is a sample email in German.
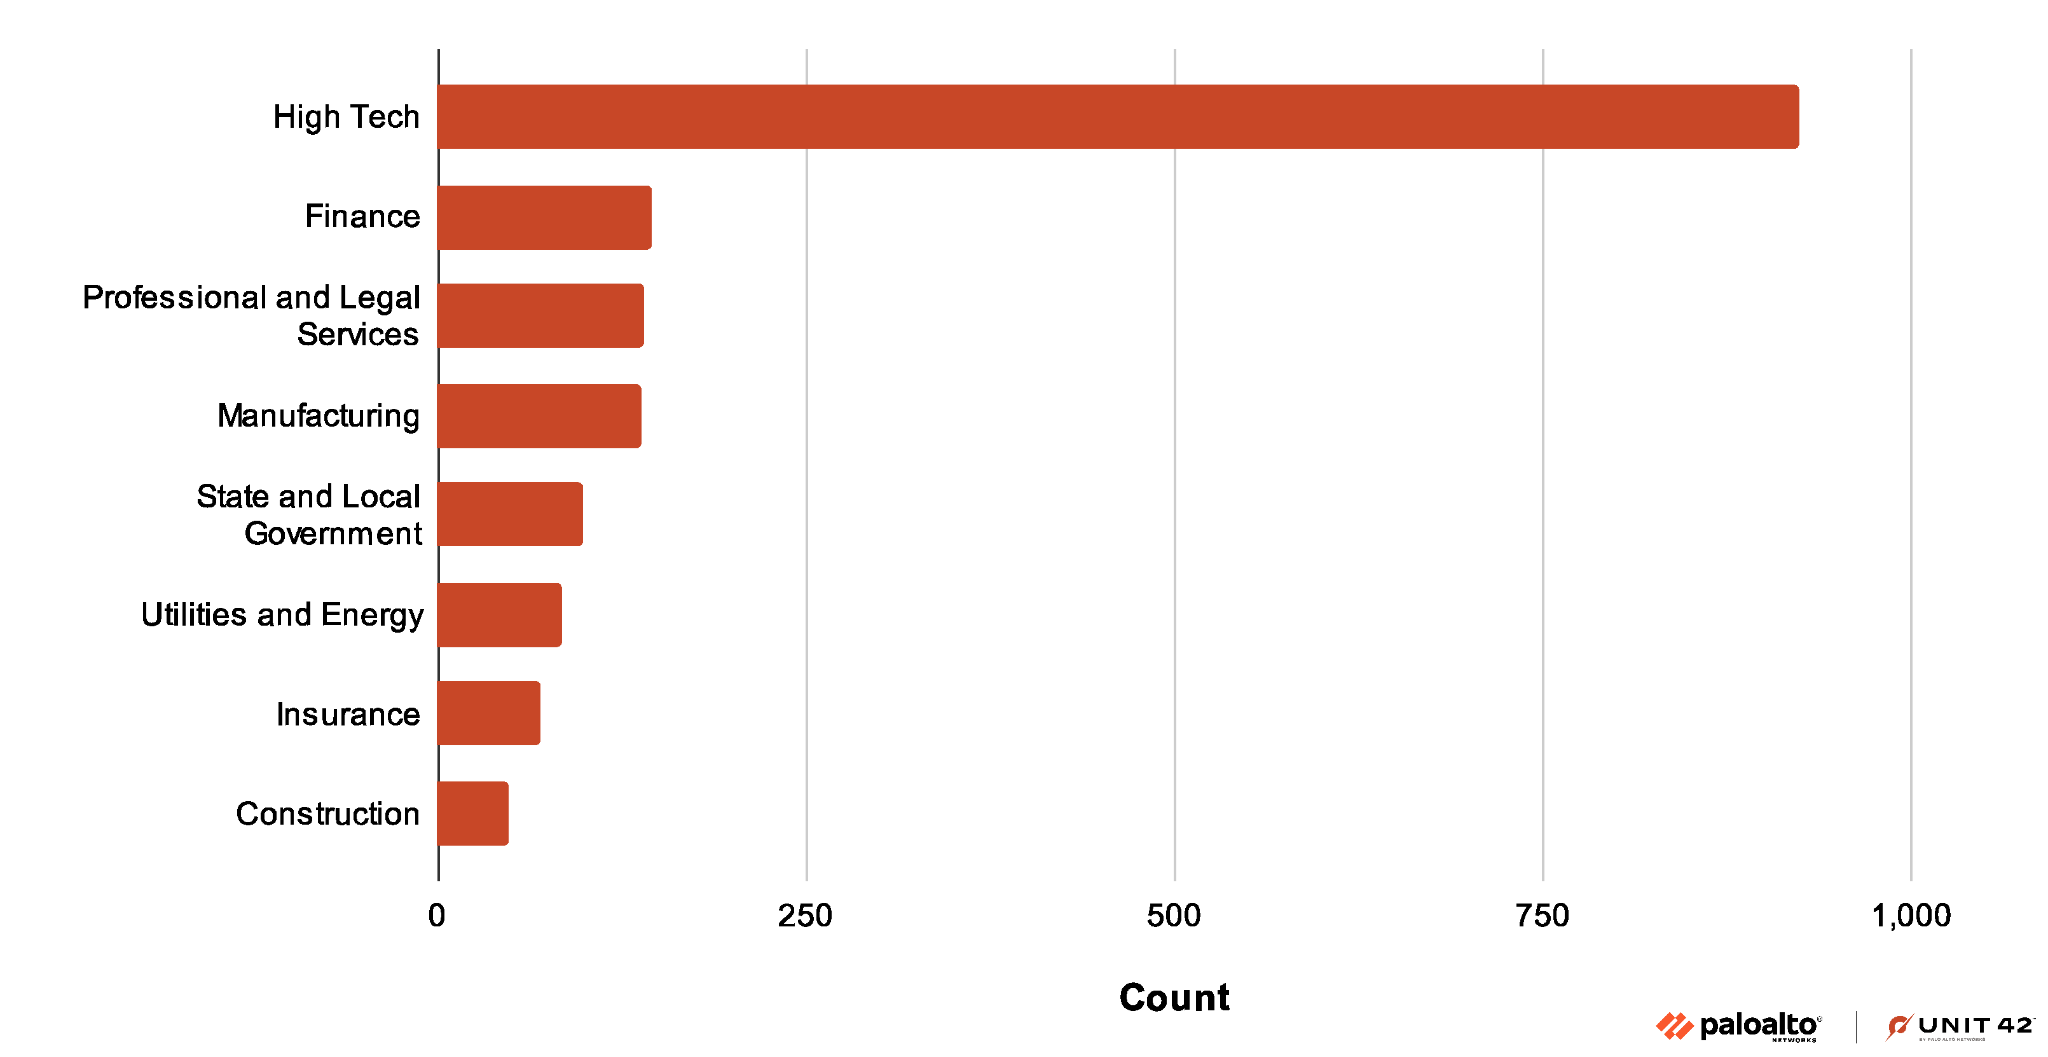
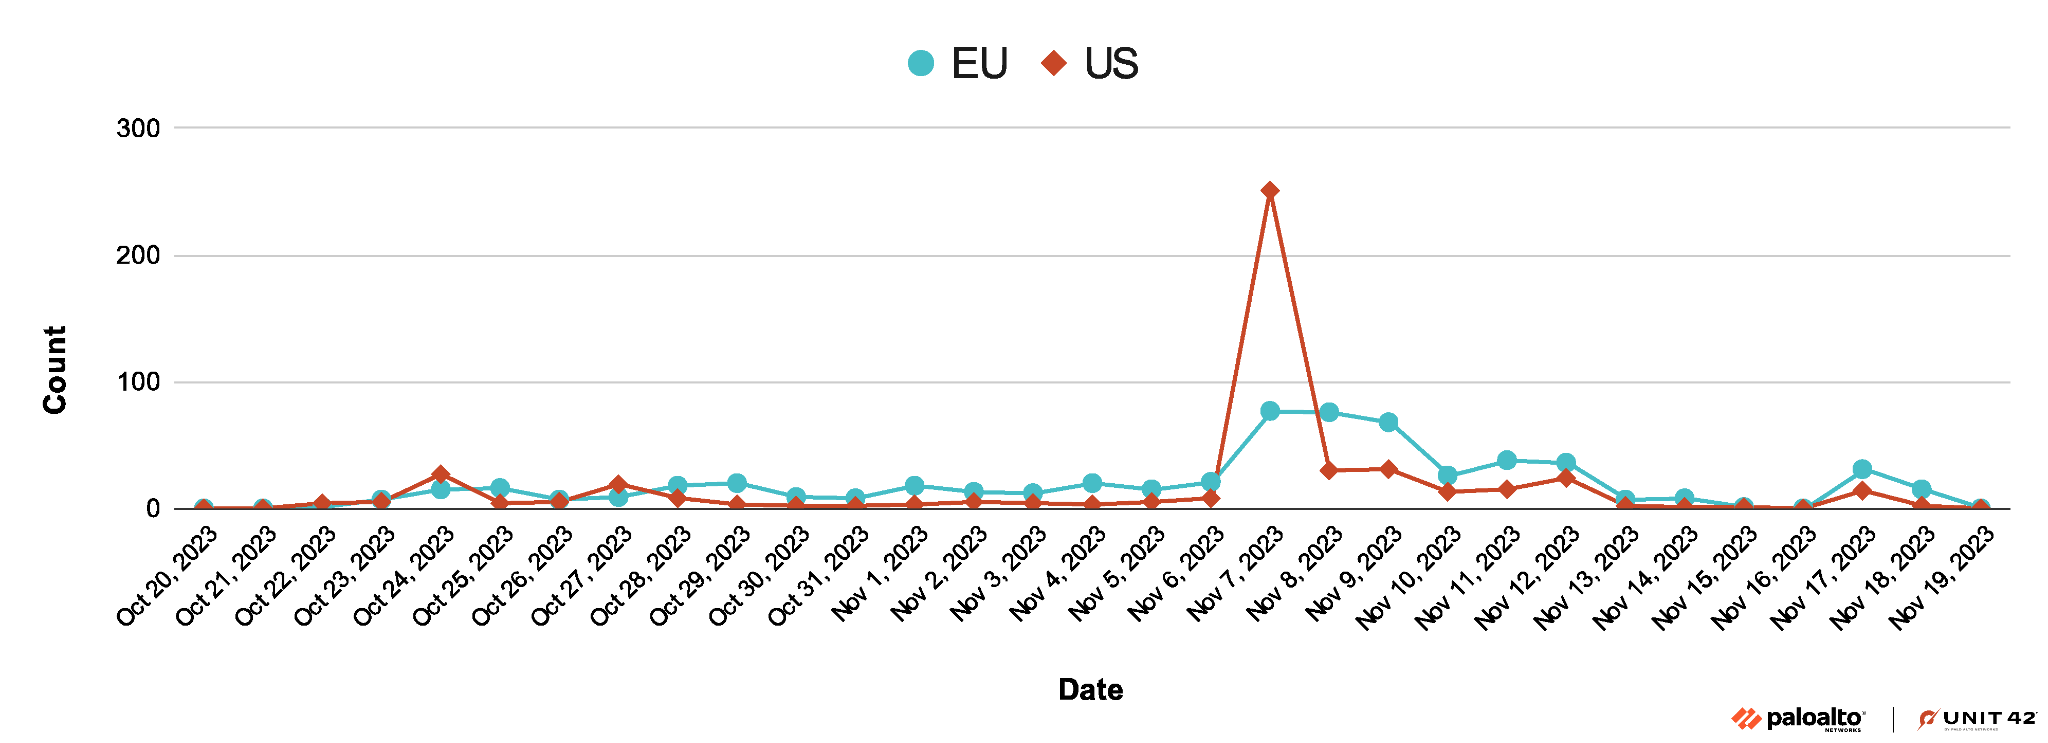 Figure 4 shows that while this recent campaign seems to target organizations in many industries, organizations in the high tech industry have been the largest target.
For the technical analysis click here.



